Passive Intelligence Gathering Analytics
Explore passive intelligence gathering techniques, open-source intelligence, and data analysis using Just-Metadata. Learn to identify threats and enhance cybersecurity through practical tools and methodologies.
Scaling MISP With The Cloud
Learn strategies for scaling MISP using cloud technologies to enhance threat intelligence sharing and improve cybersecurity operations in large-scale environments.
Discover How EclecticIQ Platform and MISP Go Together
Explore the synergy between EclecticIQ Platform and MISP for enhanced threat intelligence sharing, automated analysis, and streamlined incident response workflows.
MISP Summit 2017 - MISP and Open Formats
Explore MISP's open formats, standardization efforts, and governance in threat intelligence sharing, emphasizing complexity management and interoperability.
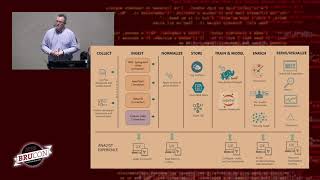
Cloud SIEM - What Happened and What's Next?
Explore cloud SIEM's impact on cybersecurity, from real-time threat detection to AI-driven responses. Learn how this technology reshapes security teams, risk management, and the future of threat hunting.
Open Source Security Orchestration
Explore open-source security orchestration using Adaptive Network Protocol (ANP) for efficient threat response, automated network defense, and improved visibility across multiple systems and clouds.
Creating REAL Threat Intelligence with Evernote
Explore threat intelligence creation using Evernote, covering data-driven feeds, task management, and open-source intelligence gathering for effective organizational security strategies.
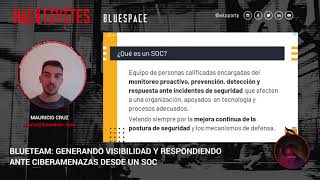
Blue Team - Generando Visibilidad y Respondiendo Ante Ciberamenazas Desde un SOC
Metodología para detectar y responder ante ciberamenazas en organizaciones, abordando visibilidad, priorización y automatización desde un SOC. Incluye servicios, componentes y herramientas para una gestión eficaz.
Why the LinkedIn Hack Could Be Your Biggest AppSec Threat
Explore account takeover threats, their long-term impact, and effective defense strategies. Learn about hacking techniques, credential stuffing, and tools to protect against evolving cyber risks.
Malware Automation
Explore automated malware production techniques, tools, and methodologies used by attackers to generate thousands of threats daily, including a live demonstration of the process.
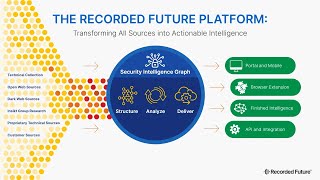
Intelligence Led Security Operations in Microsoft Azure Sentinel
Integrate Recorded Future with Azure Sentinel to quickly identify, prioritize, and action threats using external threat intelligence, maximizing existing security investments.
Defending Democratic Institutions - Election 2018 and Beyond
Experts discuss strategies to protect elections and democratic institutions from foreign interference, focusing on cybersecurity, misinformation, and collaborative efforts between tech companies and government agencies.
Freaky Leaks from a Chic Geek
Explore leakware, data breaches, and vulnerabilities. Learn to identify risks, share threat intelligence, and protect assets using OWASP Top Ten 2017. Discover real-world examples and strategies for improved cybersecurity.
Intelligence Led Penetration Testing
Explore intelligence-led penetration testing using threat intel and OSINT to create bespoke, realistic assessments that mimic real-world attack techniques and toolkits.
Disinformation as a Service
Explore disinformation tactics, their impact, and automated propagation methods in this eye-opening talk on cybersecurity threats and their real-world consequences.
Creating Data-Driven Threat Intelligence Signals in a Zero Trust Environment
Explore dynamic, data-driven threat intelligence signals for "Zero Trust" environments, reshaping security approaches for modern network architectures.
Operation PZCHAO - Dissecting a Cyber-Attack
Explore a sophisticated cyber-attack targeting Asian institutions, dissecting its modules, capabilities, and impact on victims' data in this in-depth analysis of Operation PZCHAO.
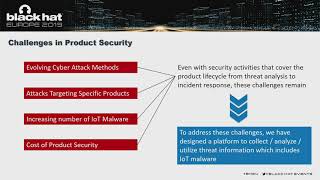
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.

Conducting a Successful False Flag Cyber Operation - Blame it on China
Explore techniques for conducting false flag cyber operations, including persona creation, toolchain analysis, and exploitation methods. Learn to understand and counter attribution attempts in cybersecurity.
Death to the IOC - What's Next in Threat Intelligence
Explore ML-driven automation for cyber threat intelligence, including custom entity extraction and attack pattern identification, moving beyond traditional IOC approaches.
Incident Response
Explore incident response and threat intelligence with Palo Alto Networks' SVP Wendi Whitmore, discussing cybersecurity consulting, ransomware trends, and prevention strategies.