APT Reports and OPSEC Evolution
Explore how advanced threat actors adapt to security innovations and APT reports, and discover strategies for improving cybersecurity defenses.
Deconstructing APT28's XAgent for OSX
Detailed analysis of APT28's XAgent malware for macOS, exploring its advanced spying capabilities including keylogging, screen capture, and data exfiltration from iOS backups.
My Phishing Kit Burnbook
Explore phishing kit ecosystems, organized crime groups, and PhishPond tool for detection and analysis in this cybersecurity deep dive.
Rise of the Vermilion - Cross-Platform Cobalt Strike Beacon Targeting Linux and Windows
Explore the first cross-platform Cobalt Strike re-implementation, Vermilion Strike, targeting both Linux and Windows in real-world attacks. Learn about this significant malware discovery.
Our Biggest Bet Yet
Explore strategies to supercharge security intelligence and unite against future threats, addressing data explosion, skills shortage, and persistent attackers.
In Curation We Trust - Generating Contextual and Actionable Threat Intelligence
Optimizing threat intelligence with MISP: Learn to curate, contextualize, and automate TI feeds for actionable insights, reducing false positives and enhancing SOC, IR, and malware analysis collaboration.
Dissecting of Non Malicious Artifacts - One IP at a Time
Dissecting non-malicious artifacts from online malware scanners to reveal sensitive data leaks and build intelligence platforms. Explores the risks of security solutions sharing data with external services.
Decepticon
Explore Decepticon, an innovative cybersecurity tool for creating deceptive network environments to detect and analyze attacker behavior in real-time.
A Better Way to Get Intelligent About Threats
Explore innovative approaches to threat intelligence, focusing on data collection, automation, and analysis using the Diamond Model for more effective cybersecurity strategies.
Finding the Best TI Provider for a Specific Purpose
Explore methodologies for evaluating and selecting the most suitable Threat Intelligence provider, focusing on comparison metrics, data analysis, and key takeaways for various cybersecurity roles.
The Snake Keeps Reinventing Itself
Explore the evolution and tactics of "The Snake" malware, including infection vectors, lateral movement, and backdoor mechanisms in this cybersecurity analysis.
Real World - Threat Intelligence
Explore real-world threat intelligence in activism, emergency response, and political adversaries. Learn to diagnose problems, develop treatment plans, and understand various security threats.
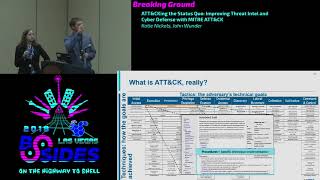
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
Leveraging Threat Intelligence in the Prioritization of Detection Sources - DefCamp - 2021
Explore threat intelligence integration for prioritizing detection sources, enhancing security strategies with MITRE ATT&CK, and leveraging internal and external intelligence for effective threat modeling.
Threat Intelligence! DIY! - DefCamp - 2016
Aprenda a implementar inteligência de ameaças DIY usando Splunk. Descubra técnicas práticas para configurar, pesquisar e criar dashboards para melhorar sua segurança da informação.
From Threat Intelligence to Rapsheets in Just a Few Steps - DefCamp - 2016
Explore threat intelligence transformation into actionable data using innovative techniques like honeypots, passive DNS, and graph-based models for enhanced cybersecurity analysis and decision-making.
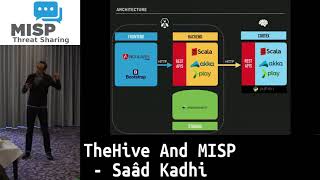
TheHive and MISP
Explore TheHive and MISP integration for enhanced threat intelligence sharing, analysis, and incident response capabilities in cybersecurity operations.
On Strategy
Guidance for development teams on implementing effective security strategies, covering risk assessment, compliance, staffing, and integrating security into organizational culture and processes.
Barncat - Using MISP for Bulk Surveillance of Malware
Explore MISP for large-scale malware surveillance, focusing on config extraction, analysis techniques, and practical applications in cybersecurity threat intelligence.
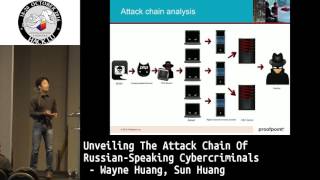
Unveiling the Attack Chain of Russian-Speaking Cybercriminals
Unveiling the sophisticated attack chain of Russian-speaking cybercriminals, detailing their infrastructure, techniques, and resources accumulated since 2007, including billions of compromised emails and millions of infected servers.
Finding the Best Threat Intelligence Provider
Explore threat intelligence providers, focusing on data quality, formats, and alignment to enhance network security monitoring and defend against advanced persistent threats.