NLP for Security Log Analysis - Learning to Crawl Before You Run
Explore the application of NLP in security analysis, focusing on embeddings for insider threat detection and the impact of large language models on the field.
Angler Lurking in the Domain Shadows
Explore the Angler exploit kit, domain shadowing, and cybersecurity threats. Learn detection methods and gain insights into evolving attack techniques and defense strategies.

State of the Onion - Security Onion Conference 2021
Comprehensive overview of Security Onion's latest developments, features, and future roadmap, presented by Doug Burks at the annual conference.

Security Onion 2017 - Pivoting Effectively to Catch More Bad Guys
Learn effective pivoting techniques to enhance threat detection and investigation skills, improving your ability to identify and catch malicious actors in cybersecurity.
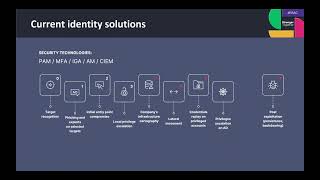
Hybrid Active Directory Attacks - Anatomy and Defenses
Explore Active Directory vulnerabilities and defense strategies for both on-premises and Azure environments. Learn to identify and mitigate common attack vectors to enhance organizational security.
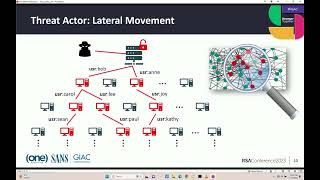
Hunting Stealth Adversaries with Graphs & AI
Discover how machine learning and graph modeling can uncover hidden adversaries in cybersecurity. Learn to apply the CHRYSALIS framework for effective threat detection using real-world data.
Blue Team Visibility
Explore strategies for enhancing blue team threat detection capabilities, leveraging multiple data sources to stay ahead of sophisticated attackers in an ever-evolving cybersecurity landscape.
Hunting for Malicious Infrastructure Using Big Data
Explore innovative machine learning techniques for detecting malicious infrastructure in HTTP responses, focusing on uniqueness and header order features to identify command and control servers.
O-Checker - Detection of Malicious Documents Through Deviation From File Format Specifications
Explores detection of malicious documents by identifying deviations from file format specifications, focusing on targeted email attacks in Japan and introducing the o-checker tool for high detection rates.
MITRE ATT&CK - The Play at Home Edition
Learn how various cybersecurity teams can leverage MITRE ATT&CK framework to enhance threat tracking and protection strategies, with practical insights for immediate implementation.
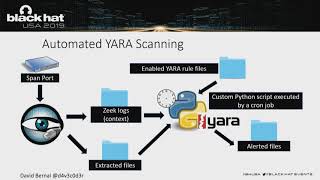
Detecting Malicious Files with YARA Rules as They Traverse the Network
Learn to detect malicious files using YARA rules and Zeek IDS for early-stage attack identification, enhancing network security with improved performance and targeted scanning techniques.
Malware Buried Deep Down the SPI Flash - Sednit's First UEFI Rootkit Found in the Wild
Uncover Sednit's groundbreaking UEFI rootkit campaign, exploring its sophisticated techniques for deep system compromise and implications for cybersecurity in high-profile attacks.
Lost in Transaction - Process Doppelgänging
Explore Process Doppelgänging, a stealthy attack technique that evades security solutions. Learn its advantages over Process Hollowing and understand its detection challenges.
Inside Out - The Cloud Has Never Been So Close
Explore a novel graph-based approach to cloud infrastructure attacks, revealing vulnerabilities in resource relationships and demonstrating potential privilege escalation techniques.
Burning Down the Haystack to Find the Needle
Explore network flow pattern analysis to detect and prevent contemporary threats, and learn how to build a security analytics program for enhanced threat visibility and response.
Baited Canaries - Monitoring Attackers with Active Beacons
Explore innovative techniques combining document viewing environments and canary tokens to detect and monitor potential attacks, gaining valuable insights into attacker behavior and victim interactions.
Inside Magecart - Their Web Skimming Tactics Revealed
Explore Magecart's evolution, tactics, and techniques in compromising e-commerce sites for credit card skimming. Learn about high-profile breaches and the criminal underworld behind this cybercrime phenomenon.
No Silver Bullet - Multi Contextual Threat Detection via Machine Learning
Explore multi-contextual threat detection using machine learning, covering big data processing, modeling adversaries, and building custom solutions for defense at scale.
Detecting the Elusive Active Directory Threat Hunting
Learn advanced techniques for detecting and hunting threats in Active Directory environments from security expert Sean Metcalf.
How I Learned to Stop Worrying and Build a Modern Detection & Response Program
Discover a framework for building effective, modern detection and response programs. Learn key capabilities and strategies to enhance your cybersecurity approach.
Why You Need to Detect More Than Pass-the-Hash
Explore advanced techniques for detecting compromised credentials beyond Pass-the-Hash, focusing on efficient methods to identify misused or stolen login information.