Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.
New Trends in FastFlux Networks
Explores new trends in fast-flux networks, including slower change rates, shared resources, multi-level structures, and similarities with benign applications. Proposes novel detection approaches based on these findings.
Putting 2 and 2 Together
Explore advanced cybersecurity techniques and threat analysis strategies in this Black Hat conference talk, focusing on connecting disparate pieces of information to uncover hidden vulnerabilities and potential attacks.
Honeypots
Explore honeypot technology for network security, including deployment strategies, data analysis, and legal considerations in this comprehensive presentation by Lance Spitzner.
Protecting Your IP Network Infrastructure
Learn strategies to safeguard your IP network infrastructure from threats, vulnerabilities, and attacks. Gain insights into best practices for network security and risk mitigation.

Security Onion Hybrid Hunter Beta 3 - Community ID and Sysmon Integration
Explore Security Onion Hybrid Hunter Beta 3, Community ID, and Sysmon features for enhanced network security and threat detection in enterprise environments.
Using Security Onion to See Adversary Activity through All Phases of the Kill Chain
Explore how Security Onion detects and analyzes adversary activities across all stages of the cyber kill chain, enhancing threat detection and response capabilities.

Augmenting the Onion - Facilitating Enhanced Detection and Response with Open Source Tools
Explore open-source tools for enhancing threat detection and response capabilities in Security Onion, improving network security monitoring and incident handling processes.
Lifting the Fog of War
Explore MS-RPC's role in Windows, its vulnerabilities, and defensive mechanisms. Learn to utilize built-in features for tracking and defending against RPC-based attacks, with practical tools and signatures.
DNS Spikes, Strikes, and The Like
Explore DNS query patterns to identify potential threats using unsupervised learning methods. Learn to analyze traffic trends and distinguish malicious domains from benign spikes.
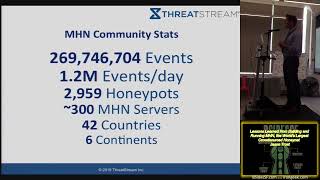
Lessons Learned from Building and Running MHN, the World's Largest Crowd-sourced Honeynet
Explore insights from building the world's largest crowdsourced honeynet. Learn about deploying diverse honeypots globally, analyzing security data, and creating a distributed sensor network for tracking threats.
Detecting and Handling IoT Interaction Threats in Multi-Platform Multi-Control-Channel Smart Homes
Explore IoTMediator: a system for detecting and handling interaction threats in complex smart home environments with multiple platforms and control channels.

Introduction to Security Onion 2.4
Explore Security Onion 2.4's features and capabilities for network security monitoring, threat hunting, and incident response in this comprehensive overview.
Avoiding the Landmines in Your Own Backyard
Discover strategies to identify and mitigate hidden security risks within your organization's internal network infrastructure and practices.
Is the IDS Dead?
Explore the current state and future prospects of Intrusion Detection Systems (IDS) in cybersecurity, examining their effectiveness and potential obsolescence.
Seeing Red In Your Future
Explore advanced techniques for Red Team operations, including strategies for evading detection and improving effectiveness in penetration testing scenarios.
IOCaware - Actively Collect Compromise Indicators and Test Your Entire Enterprise
Learn to actively collect compromise indicators and test your entire enterprise using IOCaware, enhancing your organization's cybersecurity posture and threat detection capabilities.
Follow the Foolish Zebras - Finding Threats in Your Logs
Discover effective techniques for identifying security threats by analyzing log data, enhancing your ability to detect and respond to potential risks.
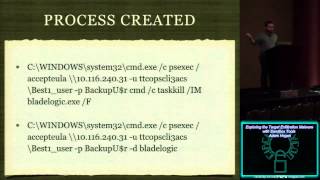
Exploring the Target Exfiltration Malware with Sandbox Tools
Explore target exfiltration malware using sandbox tools. Learn static and dynamic analysis techniques, process management, and considerations for effective malware detection and security automation.
Its Not Easy Being Purple
Explore the challenges and strategies of purple team cybersecurity with insights from industry experts on effective defense and offense integration.
Are You a Beefeater Focused on Protecting Your Crown Jewels
Explore strategies for safeguarding critical assets in cybersecurity, drawing parallels to the historic role of Beefeaters protecting the Crown Jewels.