DroidGuard - A Deep Dive into SafetyNet
Explore SafetyNet's internal mechanisms, VM design, and security checks for detecting Magisk, emulators, rooted devices, and Pegasus in this comprehensive analysis of DroidGuard.
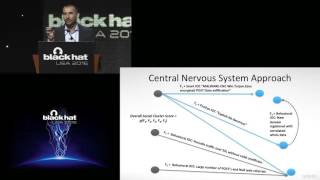
From False Positives to Actionable Analysis
Modeling human behavior in network traffic to automatically label security events, using distributed forensic AI for threat detection and response optimization.
Writing Badass Malware for OS X
Explore advanced OS X malware techniques, persistence methods, and security bypasses. Learn to create sophisticated threats and enhance Mac protection against current and future malware.
Cybercrime in the Deep Web
Explore automated detection of cybercrime in anonymous networks beyond TOR, including I2P and FreeNET. Learn about DeWA system for identifying emerging threats in the Deep Web.
The Security Wolf of Wall Street - Fighting Crime With High-Frequency Classification
Explore real-time threat detection using machine learning on massive DNS data. Learn about Avalanche stream processing and NLP-Rank for automated phishing detection at scale.
BGP Stream
Explore BGP Stream: real-time detection of potentially malicious BGP/ASN changes for enhanced network security and traffic flow monitoring.
Detecting 0-Days Attacks with Learning Intrusion Detection Systems
Explore cutting-edge techniques for detecting zero-day attacks using advanced learning intrusion detection systems, enhancing cybersecurity defenses against emerging threats.
Next Gen Application Proxies Protect Against The Latest Attacks & Intrusions
Explore advanced application proxies for enhanced cybersecurity, covering application awareness, privilege management, stateful inspection, and threat detection techniques.
Tracking Prey in the Cyberforest
Explore advanced techniques for tracking and analyzing cyber threats in complex network environments, enhancing your ability to detect and respond to sophisticated attacks.
The Fox is in the Henhouse - Detecting a Breach Before the Damage is Done
Detect network breaches early using visibility tools, data analysis, and real-time decision-making. Learn to choose and integrate security solutions for proactive threat response.
Back to the Future - How to Respond to Threats Against ICS Environments
Explore strategies for responding to threats in Industrial Control System environments, focusing on current challenges and future-oriented solutions for enhanced cybersecurity in critical infrastructure.
Splunking the Clouds - Finding the Needle in AWS & Azure
Explore cloud security techniques for AWS and Azure, focusing on identifying and addressing potential vulnerabilities using Splunk's powerful data analysis capabilities.
Fileless Malware – Beyond a Cursory Glance
Explore fileless malware techniques, their evolution, and advanced detection methods in this in-depth analysis of a growing cybersecurity threat.
Active Defense Untangled
Explora estrategias de defensa activa en ciberseguridad, analizando técnicas y consideraciones éticas para proteger sistemas y redes de manera proactiva frente a amenazas emergentes.
No More Time - Closing the Gap with Attackers
Explore strategies to reduce cybersecurity response times and close the gap with attackers. Learn how organizations are leveraging data to detect and respond to threats more quickly and effectively.
TARDIS - Rolling Back the Clock on CMS-Targeting Cyber Attacks
Automated system for detecting and remediating long-lived multi-stage attacks on CMS-based websites using nightly backups, improving security beyond traditional "backup and restore" models.
Detection At Scale
Explore strategies for implementing large-scale threat detection systems, focusing on efficiency, scalability, and effectiveness in modern cybersecurity environments.
Detection as Code - The Engineering-Focused Future of Detection and Response
Explore engineering-focused principles for building scalable threat detection programs, moving beyond traditional SOC models to create more effective and efficient security responses.
Revoke-Obfuscation - PowerShell Obfuscation Detection and Evasion Using Science
Explore PowerShell obfuscation detection techniques using scientific methods, including character frequency analysis, cosine similarity, and machine learning algorithms for improved cybersecurity.
To Normalized Logs, and Beyond - Building a Threat Detection Platform from Scratch
Deep dive into building a scalable, lean threat detection pipeline. Learn automation techniques for data ingestion, detections-as-code, and filtering to create a serverless platform for effective threat detection.
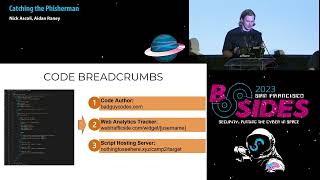
Catching the Phisherman
Uncover the largest credential harvesting campaign: its discovery, impact, and ongoing response. Gain insights into cybersecurity threats and investigative techniques.