Wireless Sensors' Power Consumption and IoT Security
Explore IoT security challenges and innovative solutions using power behavioral profiling and deep learning to detect threats in distributed sensor environments.
The Seven Most Dangerous New Attack Techniques, and What's Coming Next
Explore cutting-edge cyber threats, their mechanisms, and defense strategies. Learn about PowerShell attacks, Android vulnerabilities, and industrial control system risks from leading security experts.

Hunting and Tracking Rogue Radio Frequency Devices
Explore dangers of rogue radio frequencies and learn techniques to identify, locate, and protect against potential threats in organizational and personal contexts.
Hunting Linux Malware for Fun and Flags
Explore Linux server malware analysis techniques, from basic artifact examination to advanced memory dumping and network capture, enhancing your cybersecurity skills.
How Threat Intelligence Sharing and Automation Wins the War against Attackers
Explore how real-time threat intelligence sharing, automation, and orchestration can enhance cybersecurity efforts and effectively combat attackers in today's digital landscape.
AI Security Engineering - Modeling - Detecting - Mitigating New Vulnerabilities
Explore AI security threats, including adversarial attacks and data poisoning. Learn detection, protection, and mitigation strategies for AI/ML systems from Microsoft experts.
Undocumented MS Word Features Abused by Attackers
Explore undocumented MS Word features exploited by attackers, focusing on remote picture links and their potential for profiling activities. Learn detection methods and threat actor insights.
Log in Your Own Eye - Exploiting a Stealthy C2 Channel in Azure Logging Infrastructure
Explore Azure Log Analytics exploitation as a covert channel, uncovering potential security threats in cloud logging infrastructure and learning mitigation strategies.
Fantastic AWS Attacks and Where to Find Them
Explore AWS attack techniques and build effective cloud defenses using the ATT&CK framework. Learn to create and operationalize detections for enhanced AWS infrastructure security.
Graph Based Detection and Response with Grapl
Explore graph-based security analytics with Grapl, leveraging Python for powerful attack detection, behavior analysis, and streamlined investigations in complex environments.
Guarding Against Protocol Subversion at Coinbase
Explore blockchain security strategies at Coinbase, focusing on safeguarding assets against protocol subversion, 51% attacks, and smart contract vulnerabilities in Proof of Work and Ethereum networks.
The Bucket List - Experiences Operating S3 Honeypots
Insights from operating S3 honeypots: Discover who's hunting for exposed buckets, their methods, and how to protect your AWS assets through monitoring and defensive strategies.
Building a Predictive Pipeline to Rapidly Detect Phishing Domains
Learn to build a predictive pipeline using Python and machine learning to detect phishing domains in real-time, leveraging Certificate Transparency logs and supervised learning techniques.
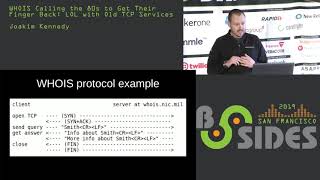
WHOIS Calling the 80s to Get Their Finger Back
Explore creating a remote access trojan using TCP services like Whois and Finger, discussing implementation, detection, and mitigation strategies for this Live Off the Land technique.
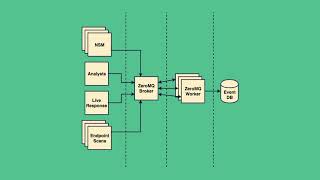
Beyond AV - Detection-Oriented File Analysis
Explore advanced file analysis techniques for enhanced threat detection, focusing on Strelka's features and applications in enterprise security.

Detecting Credential Compromise in AWS
Learn techniques to detect and mitigate credential compromise in AWS, a widespread concern for cloud-based companies. Explore various attacker motives and outcomes.
Catch Me, Yes We Can - Pwning Social Engineers Using Natural Language Processing Techniques in Real-Time
Explore techniques to detect and prevent social engineering attacks across various communication channels using content-based analysis and natural language processing.
What the Log - So Many Events, So Little Time
Explore Windows Event Log for efficient adversary detection, leveraging automation and MITRE ATT&CK framework to enhance cybersecurity monitoring and response capabilities.
Real-Time Detection of Attacks Leveraging Domain Administrator Privilege
Discover a real-time method to detect attacks using Domain Administrator privileges, including Golden Tickets, through Domain Controller Event logs for immediate threat mitigation.
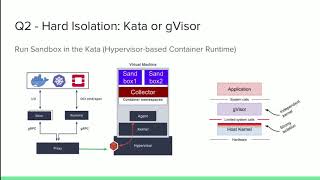
Cloud-Native Sandboxes for Microservices - Understanding New Threats and Attacks
Explore redesigned sandboxing for container environments, improving detection of microservice-oriented attacks and addressing performance challenges in contemporary systems.
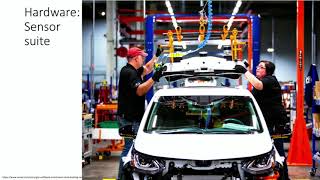
Applied Self-Driving Car Security
Explore self-driving car security with industry experts, covering technology, potential attacks, and defense strategies for this emerging field.