Virus! Malware! and Threats! Oh My!
Explore 50 years of cyber threats, detection tactics, and containment strategies. Learn about the cybercriminal economy and how to understand your opponents in today's digital landscape.
Solving Threat Detection
Explore key issues in threat detection, including information sharing, SOC models, and tooling challenges. Learn practical solutions and real-world examples from Countercept's hunt team experiences.
A Year in the Wild - Fighting Malware at the Corporate Level
Explore Yelp's automated malware defense system, featuring in-house tools like AIR and OSXCollector, complemented by open-source solutions for swift threat detection and response in corporate networks.
Sherlock Holmes - Finding Threats We Didn’t Know We Were Looking For
Explore threat detection using human intuition, visualization, and abductive reasoning. Learn to uncover hidden security risks and develop actionable intelligence through innovative analytical approaches.
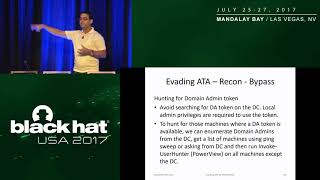
Evading Microsoft ATA for Active Directory Domination
Explore techniques to bypass Microsoft ATA's threat detection in Active Directory, covering reconnaissance, credential attacks, lateral movement, and persistence methods.
Exploit Kit Cornucopia
Explore creative techniques for detecting Exploit Kit infrastructure, including compromised websites, gates, and dedicated hosts, while understanding their underlying architecture.
My Bro The ELK - Obtaining Context From Security Events
Automate security event analysis using ELK, Bro IDS, and threat intelligence feeds. Learn to integrate frameworks for faster incident response and enhanced threat detection.
Office Drama on macOS
Explore macOS-specific Office macro attacks, their growing popularity, and unique exploit techniques. Learn about analysis, sandbox bypassing, and detection methods for these emerging threats.
The Future of Securing Intelligent Electronic Devices Using the IEC 62351-7 Standard for Monitoring
Explore threat detection in smart grids using IEC 62351 and SNMP, with live coverage analysis and demonstrations of active monitoring for securing intelligent electronic devices.
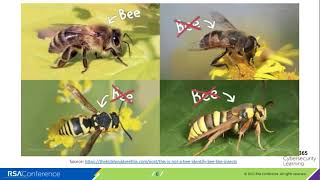
What Cybersecurity Practitioners Can Learn from Honeybees
Explore the fascinating parallels between honeybee colonies and cybersecurity organizations, learning valuable insights for threat detection, risk assessment, and organizational structure.
My Threat Model is Your Threat Model
Explore evolving threat landscapes, from nation-state conflicts to sophisticated attacks on individuals and devices. Learn about below-OS mitigations to protect BIOS, firmware, and data.
Rage Against the IDOR's - Using Machine Learning Models to Detect and Stop Authorization Bypass Vulnerabilities
Explore ML techniques to detect and prevent authorization bypass vulnerabilities in web applications, focusing on successful attacks and minimizing false positives.
Early Detection of Malicious Patterns in Event-Streaming Data
Explore advanced techniques for detecting malicious patterns in event streams using behavioral indicators and machine learning, focusing on early detection and automated pattern discovery.
Tracing Adversaries - Detecting Attacks with ETW
Explore advanced threat detection using ETW, covering process tracking, PowerShell monitoring, and file I/O analysis for enhanced cybersecurity defenses.
I Simulate Therefore I Catch - Enhancing Detection Engineering with Adversary Simulation
Enhance detection engineering skills through adversary simulation techniques, focusing on prevention controls, resilience validation, and automated simulation for improved cybersecurity.
Early Detection through Deception
Explore early threat detection through deception techniques, including examples of network intrusion, system compromise, and phishing prevention strategies.

You Moved to Office 365 - Now What
Explore Office 365 security, auditing, and protection strategies. Learn about cloud attack prevention, Azure Sentinel, and identity protection to enhance your organization's cloud security posture.
Embrace the Red - Enhancing Detection Capabilities with Adversary Simulation
Enhance detection capabilities through adversary simulation techniques. Learn to leverage offensive skills, conduct purple teaming, and test resilience using tools like Password Frame and Empire Spray.
Enterprise Security Monitoring - Seeing Clearly with Security Onion - Wes Lambert
Learn to implement enterprise-level security monitoring using Security Onion, covering tools, data types, interfaces, and deployment strategies for effective threat detection and analysis.
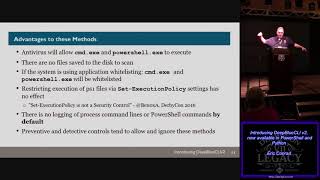
Introducing DeepBlueCLI v2 Now Available in PowerShell and Python
Explore DeepBlueCLI v2's enhanced features for Windows malware detection, including PowerShell and Python implementations, regex improvements, and automated whitelisting techniques.
Leveraging Apple's Game Engine to Detect Threats
Explore macOS threat detection using Apple's game engine. Learn about monitoring frameworks, rule-based systems, and a comprehensive platform for detecting and responding to cyberthreats on Mac systems.