Practical Steps for Reducing Exposure and Detecting Compromise
Strategies for securing DNS services, protecting against common attacks, and monitoring traffic for compromise. Covers both authoritative and recursive perspectives to enhance overall network security.

Atomic Threat Coverage - Being Threat Centric
Atomic Threat Coverage framework: Automatically generate actionable analytics to combat threats based on MITRE ATT&CK model, unifying detection, response, mitigation, and simulation for efficient security operations.
Catching WMI Lateral Movement in an Enterprise Network
Detecting WMI lateral movement in enterprise networks: overview, challenges, and custom IDS fingerprints for improved security. Practical insights for SOC analysts to enhance threat detection capabilities.
Unified DNS View to Track Threats
Explore innovative techniques for tracking cyber threats using a unified DNS view, enhancing network security and threat intelligence capabilities.
Grapl - A Graph Platform for Detection and Response
Explore a graph-based platform for enhanced cybersecurity detection and response, covering node relationships, log analysis, and advanced investigation techniques.
Red Team Revenge - Attacking Microsoft ATA
Explore techniques for attacking Microsoft Advanced Threat Analytics, including alert suppression, identity exemption, and remote control. Learn about ATA's vulnerabilities and defensive strategies.
Defeating APT10 Compiler-level Obfuscations
Explore techniques to overcome compiler-level obfuscations used by APT10, enhancing your ability to analyze and defend against advanced persistent threats.
DeTT&CT - Mapping Your Blue Team to MITRE ATT&CK
Explore MITRE ATT&CK framework for blue team mapping, focusing on attack techniques, gap analysis, and event query language to enhance cybersecurity defenses.
Graph-Charged Cybersecurity Intelligence
Explore Oracle's graph-powered cybersecurity intelligence system for real-time threat detection, featuring interactive visual interpretation for investigators to analyze machine learning model explanations.
Responding to the Ever Evolving Threat Landscape - DefCamp - 2021
Explore evolving cybersecurity threats, from ransomware to DNS tunneling, and learn strategies to protect against sophisticated attacks in this DefCamp 2021 presentation.
TIDS - A Framework for Detecting Threats in Telecom Networks
Explore a framework for detecting threats in telecom networks, covering monitoring, data collection, and analytics to protect infrastructure and subscribers from various attacks and privacy issues.
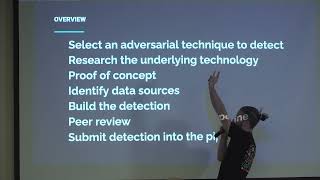
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.
Evading Microsoft ATA for Active Directory Domination
Explore techniques for evading Microsoft ATA in Active Directory environments, including threat detection bypasses, attack chain modifications, and strategies for maintaining domain dominance.
Revisiting Ring3 API Hooks: Tricks to Defeat Analysis Tools - Rafael Salema Marquez - Ekoparty - 2021
Explore innovative ring3 API hook techniques for malware development, focusing on "Egg hook" and "Hollow hook" methods to evade detection by analysis and forensics tools.
Blue Space - Open Threat Research - Roberto y Jose Luis Rodriguez - Ekoparty Security Conference - 2020
Exploración de Open Threat Research: colaboración global en seguridad informática mediante proyectos de código abierto, enfocado en desarrollo de detecciones y análisis de amenazas.
Behaviors and Patterns of Bulletproof and Anonymous Hosting Providers - USENIX Enigma Conference - 2017
Explore bulletproof and anonymous hosting providers' role in cybercrime, focusing on The Netherlands as a case study. Learn about threat detection, jurisdictional challenges, and potential solutions.
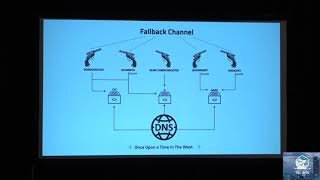
Once Upon a Time in the West - A Story on DNS Attacks
Explore DNS attack techniques used by notorious hacking groups, examining their tools and patterns to improve detection and defense strategies against evolving cyber threats.
The Importance of the Cloud and the Developers Communities in Fighting Cyber Crime
Explore cloud and AI's role in cybersecurity, innovative trends, and Microsoft's strategies to combat evolving cyber threats in this insightful talk by a leading industry expert.
Detect Unknown Threats with User and Entity Behavioral Analytics in Azure Sentinel
Explore Azure Sentinel's User and Entity Behavioral Analytics to identify anomalies, detect threats, and enhance threat hunting and response through behavioral analytics and entity profiling.
Optimizing Your Azure Sentinel Platform with CyberProof
Enhance Azure Sentinel's threat detection capabilities with CyberProof's expert insights on cloud security, cost optimization, and advanced SOC management techniques.
Ask the Experts - Protecting Always Connected Windows on ARM PCs for the Hybrid
Explore modern security solutions for hybrid work environments, focusing on Snapdragon-powered PCs with Windows secured-core features to protect against threats in real-time.