Creating Zero-CVE Base Images for Dockerfiles
Create CVE-free base images for Dockerfiles using BuildSafe. Search and add required packages easily. Simplify the process of building secure artifacts with zero vulnerabilities.
AI as an Enabler for Sustainability - Case Konecranes
Explore AI's role in sustainable logistics and supply chain management, focusing on reducing emissions, improving efficiency, and enhancing resilience and security.
Activities in Japan and 10 Streams of OSS Security Mobilization Plan
Explore Japan's OSS security activities, SBOM adoption challenges, and potential certification uses in cloud services. Gain insights into unique industry perspectives and future preparedness.
SBOMs Everywhere - Work in Progress and Challenges Ahead
Explore the progress and challenges of Software Bill of Materials (SBOMs) implementation across industries with insights from a leading expert in dependable embedded systems.
SBOM Everywhere - Understanding Software Bill of Materials
Explore the importance of Software Bill of Materials (SBOM) in securing open source supply chains and learn about its widespread implementation.
What's New in the World of SBOMs?
Explore recent developments in Software Bill of Materials (SBOMs) with industry experts, discussing advancements, challenges, and best practices in software supply chain security.
We Make Python Safer Than Ever
Explore efforts to enhance Python's security, including PyPI audits, improved practices, and community involvement. Learn about challenges, progress, and future plans for a safer ecosystem.
Making Python Safer Than Ever
Explore Python ecosystem security improvements, best practices for library maintainers and users, and PSF's efforts to enhance safety in the open-source supply chain.
Building a Secure IoT Device
Explore challenges and solutions for building secure IoT devices, covering provisioning, trust, integrity, connectivity, attestation, and firmware updates in the context of PSA and Trusted Firmware M.
Warpforge - Decentralized Supply Chain Management for Building Everything
Explore Warpforge, a build sandbox tool enhancing software creation with reproducibility, decentralized package management, and flexible filesystem composition for improved supply chain security.
Embrace Security in Your Supply Chain
Comprehensive guide to integrating security throughout the software supply chain, focusing on DevOps-friendly tools and practices to mitigate risks without hindering development.
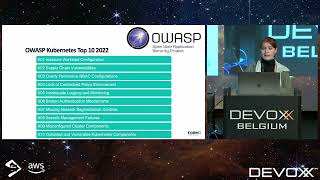
The Hacker’s Guide to Kubernetes Security
Comprehensive guide to Kubernetes security risks, focusing on OWASP Top 10. Live demos of exploits, common vulnerabilities, and best practices for hardening k8s clusters.
Supply Chain Security for OpenSource Projects
Explore supply chain security for open-source projects, covering potential threats, attack points, free tools, and strategies to protect against cyber attacks in software development.
Exploiting Vulnerabilities and Flaws to Attack Supply Chain
Explore attack vectors in the supply chain ecosystem, including vulnerabilities in IDEs, SCMs, package managers, and CI/CD platforms trusted by developers.
Supply-Chain Security: What Helping 200 Projects Improve Their Security Looks Like
Discover how Google's Open Source Security Team helped 200+ projects improve their supply-chain security, with insights on maintainer collaboration and practical security implementation strategies.
Secure Numerical Computing is Hard: Lessons from 10 Years of Open Data Science and the Long Road Ahead
Explore key security challenges and lessons learned from a decade of open data science, focusing on enterprise adoption of ML/AI technologies and emerging threats in numerical computing.
The Simple Yet Lethal Anatomy of a Software Supply Chain Attack
Explore software supply chain vulnerabilities through an attacker's lens, examining open-source security flaws and defense strategies with practical demonstrations and countermeasures.
Analysis of and Lessons from the Xz-Utils Vulnerability - What Might Come Next
Delve into the technical analysis of the xz-utils vulnerability incident, exploring the combined attack techniques, social engineering aspects, and future implications for open-source software security.
Micron Authenta Cloud Platform - Securing Edge Computing Solutions Through Customer Blueprints
Explore how pioneering companies leverage Authenta Cloud Platform to establish trust layers for secure manufacturing and innovative edge computing solutions across data centers and automotive sectors.
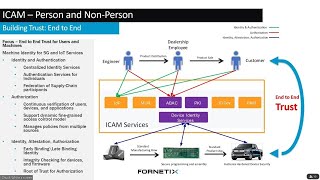
Identity and Access Management for Micron Devices - Bridging IT and OT Security
Explore identity and credential management fundamentals for building trust in IT/OT environments, focusing on authentication, authorization, and secure supply chain communication principles.
Device Security in the OCP Supply Chain - Overview of How OCP SAFE Addresses Device Firmware Challenges
Explore how OCP S.A.F.E. framework tackles device firmware security challenges and strengthens supply chain integrity through expert insights and practical solutions.