
Secret Scanning in Open Source at Scale - An In-Depth Analysis
Discover critical insights into large-scale secret scanning across NPM packages, WordPress plugins, and Ruby Gems, exploring supply chain vulnerabilities and implementing preventive measures in CI/CD pipelines.
Threat Hunting Space and Digital Energy with Physics - Session 5
Explore innovative physics-based approaches to threat hunting in ICS/SCADA networks, focusing on IoMT and IoST monitoring techniques for detecting complex adversarial activities.
Protecting Yourself From Supply Chain Attacks - Trust Is Overrated
Discover practical strategies and tools for validating hardware and software integrity, minimizing supply chain risks, and implementing effective security measures across your technology stack.
Grand Theft Actions - Abusing Self-Hosted GitHub Runners for Supply Chain Attacks
Dive into critical security vulnerabilities in GitHub Actions, exploring real-world attacks on self-hosted runners and learning how to prevent supply chain compromises in major open-source projects.
The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.
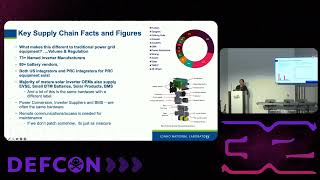
Navigating a Secure Clean Energy Transition - Cybersecurity Challenges and Solutions
Explore the cybersecurity challenges and policy implications of clean energy adoption, focusing on supply chain vulnerabilities, security strategies, and balancing economic pressures with sustainability goals.
Security Vulnerabilities in Video Surveillance Systems and Supply Chain Analysis
Explore security vulnerabilities in surveillance systems, focusing on NVR devices from major vendors like Hikvision and Dahua, while examining supply chain risks and exploitation scenarios.
Open Source Software Supply Chain Security - Understanding Threats and Best Practices
Explore critical threats to open source software supply chains, industry best practices for security, and practical strategies for protecting against vulnerabilities and cyberattacks.
International Port Security: Threats and Case Studies About Incident Response
Explore real-world port security challenges and incident response strategies through case studies, focusing on protecting global supply chains from cargo theft and cyberattacks.
サイバー経済安全保障と民主政・僭主政 - 第11回
Explore サイバー空間における経済安全保障の課題、ファーウェイ問題からグーグルと中国政府の対立まで、民主主義とサイバーセキュリティの関係性を深く考察する講義。
Product Security Certifications: Understanding Requirements, Standards, and Implementation
Explore product security certifications, their importance in supply chain security, and key considerations for implementation, focusing on major certification options and compliance requirements.
Supply Chain Security with Go
Learn Go-specific supply chain security practices to protect your software from vulnerabilities and attacks.
Essential Security Checks for Your Go Project
Implement essential security checks in Go projects using open-source tools like gosec, govulncheck, and sigstore/cosign. Learn to integrate code analysis, vulnerability scanning, and supply chain security.
Security Threat Model Analysis and Protection Practice in Edge Computing
Análisis de modelos de amenazas y prácticas de protección en computación de borde, incluyendo auditoría de seguridad de KubeEdge, iniciativas de mejora y cumplimiento SLSA L3 para fortalecer la seguridad en escenarios de edge computing.
Safeguarding Cloud Native Supply Chain - Notary Project Overview and New Features
Explore how Notary Project enhances cloud native supply chains through authentic container images and OCI artifacts. Learn about new features, roadmap, and upcoming developments in software supply chain security.

Making Python Safer Than Ever
Explore Python ecosystem security efforts, best practices for library maintainers and users, and PSF's initiatives to enhance safety in the open-source supply chain.
Automating Configuration and Management of GitHub Repositories with Minder
Learn to automate GitHub repository management using Minder, an open-source platform. Write custom Rego rules to enforce security policies across multiple repositories, enhancing supply chain security.
Below the Radar: Identifying Hidden Threats Within the Development Ecosystem
Explore critical threats in cloud-native environments, focusing on hidden exposed secrets in code. Learn about vulnerabilities in source code management, Kubernetes secrets, and Shadow IT, with mitigation strategies and tools.
Peaceful Sleeping in the Age of Shells
Explore top software vulnerabilities and learn tools to automate security for your source code and supply chain. Stay informed about threats and enhance your codebase protection.
Making the Edge Tamper-Proof: Security Challenges and Solutions in Edge Computing
Discover essential security practices for edge computing deployments, focusing on firmware protection, supply chain security, and tamper-proofing strategies using EVE-OS in remote environments.
Common Kubernetes Attack Vectors and How to Secure Your Cluster
Discover essential security strategies for Kubernetes deployments, covering authentication, network policies, pod security, and threat detection techniques for robust cluster protection.