State of the Art Supply Chain Security - In-toto, TUF, and SigStore
Explore cutting-edge supply chain security with in-toto, TUF, and SigStore. Learn how these tools create a transparent, hack-proof system to protect software from developer to end-user.
Hardening JavaScript for Supply Chain Security
Explore advanced techniques for securing JavaScript dependencies, including Compartments and LavaMoat, to protect against supply chain attacks and enhance runtime security.
Supply Chain Security Features for Dart and Flutter Projects on GitHub
Enhance Dart and Flutter project security on GitHub: verify code authenticity, validate dependencies, and monitor vulnerabilities for a robust security posture.
Semi-Advanced Threats vs the Semi-Critical Infrastructure
Explore how skilled hackers target vulnerable supply-chain dependencies, potentially affecting millions. Learn budget-friendly strategies to protect semi-critical infrastructure from disruptions.
Fortify Your Code: Secure Your Supply Chain with Scorecard
Discover how to assess and strengthen open-source software security using Scorecard, gaining practical insights into dependency risk management and implementing robust supply chain protection measures.
Continuous Assurance of Supply Chain Security Levels of Open Source Artifacts Using SLSA 0.1
Discover how to verify SLSA provenance in trusted build systems to enhance supply chain security and protect against modified sources, compromised builds, and package tampering.
Trojan Model Hubs: Hacking the ML Supply Chain and Defending Against Model Serialization Attacks
Discover essential strategies for protecting ML systems from supply chain attacks, focusing on model scanning and cryptographic signing to defend against Model Serialization Attacks in public model hubs.
End-to-End Secure Machine Learning Development - Building a Secure AI Supply Chain
Discover essential security practices for AI development, from dataset handling to production deployment, focusing on supply chain security, model provenance, and risk mitigation in machine learning applications.
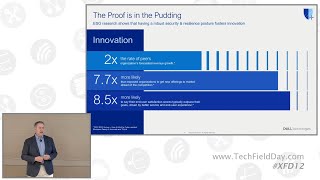
Dell Technologies Cybersecurity Strategy and Implementation
Discover Dell's comprehensive cybersecurity approach, from secure supply chain to zero trust principles, focusing on attack surface reduction, threat response, and recovery strategies.
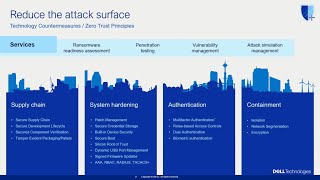
Reducing the Attack Surface: Cybersecurity Strategies and Best Practices
Discover effective strategies and best practices for minimizing cybersecurity vulnerabilities, from silicon root of trust to endpoint security and supply chain management.
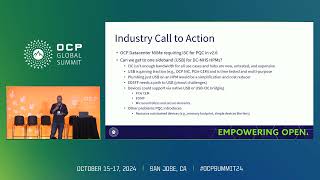
Post-Quantum Cryptography Impact on I2C Communication and Security Protocols
Explore how post-quantum cryptography's larger signatures affect I2C interfaces in server management, and discover potential industry solutions for SPDM implementation challenges.
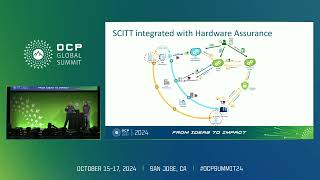
Device to Cloud Supply Chain Provenance: End-to-End Security and Attestation
Explore end-to-end supply chain security, from identity management to attestation frameworks, focusing on Caliptra's role in establishing trust from device to cloud computing environments.
Unorthodox Vectors for Cloud Attacks: Understanding CI/CD Security Risks
Explore modern cloud security challenges, focusing on CI/CD vulnerabilities and supply chain attacks rather than traditional security vectors. Learn preventive measures and emerging threat patterns.
Trojan Model Hubs - Hacking the ML Supply Chain and Defending Against Security Threats
Discover essential security strategies for ML model hubs, focusing on detecting Model Serialization Attacks and implementing cryptographic signing to protect against compromised artifacts and system vulnerabilities.
Mapping the Minefield of Open Source Software Risks - DevOps 2024
Explore open source software risks, vulnerabilities, and remediation strategies. Learn about software composition analysis, reachability, and semantic versioning for effective dependency management.
Automatic Trusted Publishing with PyPI
Explore PyPI's Trusted Publishing feature for secure, automated package releases from CI/CD pipelines. Learn implementation details and recent expansions beyond GitHub.
Exploring Essential Security Checks for Open Source Go Projects
Discover essential security tools for Go projects: gosec, govulncheck, and sigstore/cosign. Learn to enhance code security, scan vulnerabilities, and secure the supply chain.
SBOMs Go Global: Current State and Emerging Trends
Explore the global impact and emerging trends of Software Bill of Materials (SBOMs) with insights from industry expert Kate Stewart.
SBOM: The Inescapable Way of Tracking Dependencies
Explore SBOM's role in preventing cyber-attacks, its formats, and implementation across the software development lifecycle. Learn to generate, manage, and monitor SBOMs for enhanced security.
Defending Cloud Native Apps Against the Serverless Top 10
Explore serverless security risks, map OWASP Top 10 to app layers, and learn practical defense strategies using open-source tools for cloud-native applications.
Building Zero CVE Docker Images - Strategies and Solutions
Explore strategies for building zero-CVE Docker images, focusing on Chainguard images and discussing potential improvements in supply chain security. Includes resources for further learning.