Static Code Analysis in Software Development Process
Explore static code analysis integration in DevOps workflows, code reviews, and verification pipelines to enhance software quality and streamline development processes.

Effective CMake
Comprehensive guide to CMake, CTest, and CPack, covering best practices for building, testing, and packaging C++ projects, including dependency management and cross-platform development.
Securing Code with the Python Type System
Explore how Python's type system can enhance code security, from simple annotations to advanced tools, preventing vulnerabilities and enabling incremental improvements in project safety.
An Overview of the Python Code Tool Landscape 2023
Comprehensive overview of Python static code analysis tools, including linters, type checkers, and formatters. Introduces beginners to type hints and highlights the fast Rust-based linter Ruff.
The Butler and the Snake - Continuous Integration for Python
Explore effective Continuous Integration for Python projects, drawing insights from a large-scale open-source implementation. Learn key principles, tools, and best practices for automated testing and integration.
Protocols and Practices Enforcing in Python Through Bytecode and Inspection
Explore Python's bytecode and inspection capabilities to enforce protocols and best practices in third-party code, ensuring adherence to design philosophies and preventing misuse of libraries.

Streamlining the AngularJS to Angular Migration
Discover strategies for seamless AngularJS to Angular migration, including tools like AngryDog and Angular Upgrade. Learn about static analysis, automation, and overcoming common upgrade challenges.
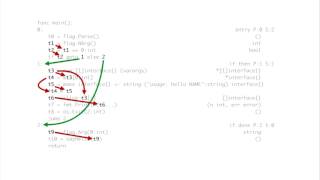
Static Code Analysis Using SSA
Explore Single Static Assignment (SSA) in Go compilers and learn to build static analysis tools using the go/ssa package for code optimization and analysis.
Find Out If Your Design System Is Better Than Nothing
Learn data-driven techniques to measure and improve your design system's adoption, ensuring it outperforms one-off components and third-party libraries through static code analysis.
NVMe Technology in Cloud Service Providers
Discover a pre-auth remote vulnerability in Linux kernel's NVMe implementation. Learn open-source vulnerability research, static code analysis, and NVMe technology. Includes live demos and practical tips.
Implement DevSecOps in Azure
Comprehensive guide to implementing DevSecOps in Azure, covering security controls, governance, and best practices for secure development and deployment across the entire application lifecycle.
Event-based Fuzzing, Patch-based Research, and Comment Police - Finding Bugs Through a Bug
Discover innovative bug-hunting techniques: event-based fuzzing, patch analysis, and comment inspection. Learn to leverage known vulnerabilities for deeper security research in Chrome and Android.
Secure Code, Safe Future: Mastering Security in Critical Software Development
Discover practical secure coding techniques and strategies for developing robust software, including vulnerability management, SBOM implementation, and hands-on security practices for critical infrastructure projects.
Raising Python Quality Across a Large and Diverse AI Organization
Discover effective strategies for scaling Python engineering excellence in AI organizations, from automated code quality tools to best practices using Poetry, Pytest, Black, Flake8, and Mypy.
Rules Lint: Formatting and Linting All Languages
Discover how to streamline code formatting and linting across multiple programming languages using rules_lint, enabling consistent workflows and efficient static analysis integration.
Secrets of the Source
Explore source code analysis techniques with industry experts, uncovering insights to enhance software quality and development practices.
Mapping the Minefield of Open Source Software Risks - DevOps 2024
Explore open source software risks, vulnerabilities, and remediation strategies. Learn about software composition analysis, reachability, and semantic versioning for effective dependency management.
Organizational Design for Efficient Product Development
Explore organizational structures' impact on product development. Learn to choose and implement the best structure for your team's needs and product stage.
Select Bugs From Binary Where Pattern Like CVE Days
Explores static code analysis techniques for vulnerability detection in binary code, focusing on pattern extraction and efficient searching across large codebases, with practical examples.
Security as Code - A DevSecOps Approach
Explore Security as Code methodology, integrating security into CI/CD pipelines for continuous vulnerability detection. Learn to implement CodeQL queries for early identification of security issues.
Security Tooling in Your DevOps Pipeline
Explore strategies for integrating security tools and automation into CI/CD pipelines, including vulnerability scanning, static analysis, and dynamic testing to enhance DevOps agility.