The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
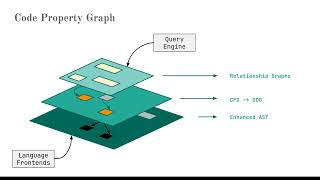
Building an Automated Machine for Discovering Privacy Violations at Scale
Exploring static analysis techniques for detecting and fixing privacy leaks in large codebases, addressing challenges in building privacy-focused tools for developers and privacy engineers.
What is Our Ethical Obligation to Ship Secure Code?
Explore ethical obligations in secure coding, data breaches, and developer responsibilities. Gain insights on improving security practices and addressing user privacy concerns.
Trick or Treat - Unveil the "Stratum" of the Mining Pools
Unveil mining pool strategies, identify Stratum servers, and explore cryptomining malware detection techniques through static and dynamic analysis, web scraping, and network scanning.
The Ways Hackers Are Taking To Win The Mobile Malware Battle
Explore cutting-edge mobile malware techniques, security paradigms, and detection methods. Live demo showcases creation of undetectable malware, highlighting challenges in mobile security.
Practical Static Analysis for Continuous Application Security
Explore practical static analysis techniques for continuous application security, from simple grep to custom tools, enhancing software development lifecycle with targeted security checks.
Why Hackers Are Winning The Mobile Malware Battle - Bypassing
Explore mobile malware challenges, hacker tactics, and bypassing techniques in this insightful talk on the evolving landscape of mobile security threats and defenses.
Myths of Threat Modeling - AppSec California
Debunking common misconceptions about threat modeling in software security, providing insights to initiate and improve this crucial design activity for better application protection.
Flipping the Script on Application Security
Learn about GitHub's developer-first approach to application security, addressing common DevSecOps challenges and exploring innovative solutions like credential scanning and static analysis.
Hacking the Hacker - The Story - DefCamp - 2019
Explore the journey of hacking a Honda vehicle, from initial assumptions to uncovering vulnerabilities. Learn about tools, techniques, and insights gained during this ethical hacking process.
Hunting Android Malware - A Novel Runtime Technique for Identifying Malicious Applications
Novel runtime technique for identifying malicious Android apps through instrumentation, addressing frustrations with static analysis and offering practical demonstrations and insights.
Agnition - The Security Code Review Swiss Army Knife - David Rook - Hack in Paris
Explore Agnitio, a comprehensive tool for secure code review, offering checklists, guidance modules, and automated analysis to enhance software development security practices.
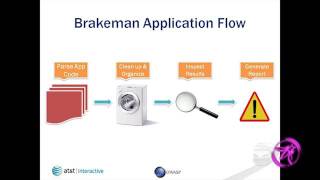
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
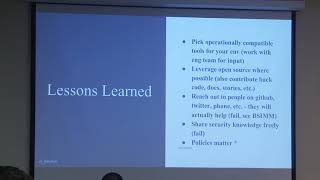
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
Your Security Tools Are Just a Stop-Gap to Secure DevOps
Secure DevOps: Beyond tools, focus on risk assessment, threat modeling, and custom security controls. Learn to integrate security effectively in CI/CD pipelines for robust application protection.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Lessons Learned from the DevSecOps Trenches
Panel discussion on scaling AppSec programs, featuring insights from security leaders at major tech companies. Covers high-ROI efforts, effective tools, and lessons learned to help organizations improve their security practices.
Battle Tested Application Security
Insights on building effective Application Security programs, focusing on security culture, defensive capabilities, and organizational empowerment across different environments.
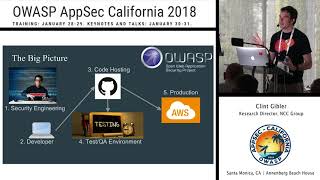
SecDevOps - Current Research and Best Practices
Explore current research and best practices in SecDevOps, covering static and dynamic analysis, security scaling, and infrastructure best practices for improved application security.
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.