Injecting Security Into Web Apps With Runtime Patching And Context Learning
Explore advanced web application security techniques using Runtime Application Self Protection (RASP) to prevent code injections and other vulnerabilities through dynamic analysis and patching.
Full Steam Ahead Serverless Hacking 101
Explore serverless hacking techniques, including environment setup, demonstrations, and common vulnerabilities like SQL injection and cross-site scripting in this comprehensive tutorial.
macOS Security Features Bypasses by Example
Explore macOS security features, vulnerabilities, and bypass techniques with a Microsoft security expert. Gain insights into SIP, TCC, and potential exploit avenues for researchers and professionals.
Give Me a SQL Injection, I Shall PWN IIS and SQL Server
Explore SQL injection vulnerabilities in IIS and SQL Server, uncovering unexpected attack vectors and their implications for Microsoft's ecosystem security.
Web Applications Bug Hunting - Fundamentals
Explore web application security fundamentals, attack vectors, and tools for bug hunting. Learn key concepts to kickstart your career in application security.
Bye-Bye False Positives - Using AI to Improve Detection
Explore AI-based injection detection using neural networks to reduce false positives in security solutions. Learn about architecture, implementation, and real-world applications.
AutoSpear - Towards Automatically Bypassing and Inspecting Web Application Firewalls
Explore techniques for automatically bypassing and inspecting web application firewalls, examining vulnerabilities in WAF-as-a-service solutions and cloud security services.
Blended Web and Database Attacks on Real-Time, In-Memory Platforms
Explore innovative attack vectors on real-time, in-memory platforms, blending web and database vulnerabilities. Learn about new SQL injection techniques, server-side JavaScript exploits, and R-based attacks in SAP HANA.
Going Auth The Rails On A Crazy Train
Explore common authentication and authorization pitfalls in Rails applications, and learn about a new dynamic analysis tool for penetration testing and securing large-scale Rails projects.
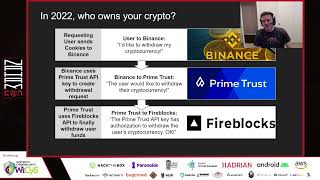
Breaking Into Cloud Wallets - Hacking Crypto Web Apps
Explore cloud wallet vulnerabilities and crypto web app hacking techniques in this talk by @samwcyo, covering blind XSS, SQL injection, and account takeovers in the cryptocurrency ecosystem.
Facebook's Approach to Common Web Vulnerabilities
Explore Facebook's strategies for combating web vulnerabilities, including XSS, CSRF, and SQL injection, through security libraries, automated detection, and lint rules.
Hackproofing Oracle EBusiness Suite
Explore vulnerabilities in Oracle eBusiness Suite and learn effective strategies to secure systems against potential attacks, including remote code execution and SQL injection.
Web Application Firewalls - Analysis of Detection Logic
Explores detection logic in Web Application Firewalls, focusing on regular expressions. Analyzes security flaws in popular WAFs and introduces tools for identifying vulnerabilities in regex patterns.
Web Security And You
Comprehensive overview of web security vulnerabilities, including XSS, CSRF, and SQL injection, with code examples and practical solutions for protecting websites.
Hunting Asynchronous Vulnerabilities
Explore techniques for uncovering hidden vulnerabilities in backend systems using exploit-induced callbacks. Learn to detect and exploit asynchronous issues across various technologies and platforms.
Kill All Humans - Bugs - Machine Learning to the Rescue of Code Review
Explore machine learning techniques for efficient security code reviews, reducing false positives and automating vulnerability classification in large-scale applications.
Practical AppSec - Quick Wins for More Secure Software
Practical steps to enhance application security with minimal effort, including quick wins, finding attack surfaces, and engaging developers. Introduces a software security maturity model for measuring progress.
Automate Security Tests for APIs with Syntribos - An Open Source Security Scanner
Explore Syntribos, an open-source automated security scanner for RESTful APIs. Learn its design, configuration, and capabilities to detect vulnerabilities like SQL injection and DoS attacks efficiently.
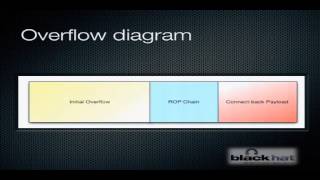
SQL Injection to MIPS Overflows - Rooting SOHO Routers
Explore SQL injection techniques to exploit buffer overflows and gain root access to Netgear routers, including file extraction and live demonstration of vulnerabilities in SOHO devices.
SQL Injection Detection - Joint Force Database Auditing & Anomaly Intrusion Detection
Explore advanced SQL injection detection techniques, combining database auditing and anomaly intrusion detection for enhanced cybersecurity measures.
XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.