How SIG Release Cooks Trustworthy Artifacts From Raw Source Code - Kubernetes Build Process
Explore how Kubernetes SIG Release transforms source code into trusted artifacts, focusing on SLSA compliance, community-controlled infrastructure, and expanded artifact signing.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
Software Supply Chain Aspects in Infrastructure as Code
Explore infrastructure-as-code security risks, focusing on supply chain vulnerabilities in reused templates and containers. Learn strategies to mitigate threats and ensure robust IaC practices.
Securing Your Infrastructure as Code Pipeline
Explore techniques for securing Infrastructure as Code pipelines, including static analysis, RBAC, and open-source tools like Open Policy Agent and Sigstore, to enhance productivity and compliance.
Securing Kubernetes Manifests with Sigstore Cosign - Options and Best Practices
Explore options for verifying Kubernetes manifests with Sigstore Cosign. Learn about integrating security solutions, GitOps tools, and policy engines to enforce security policies and prevent unwanted changes in your cluster.
Docker Scout - Securing the Complete Software Supply Chain
Explore Docker Scout's real-time vulnerability detection, remediation suggestions, and policy evaluation for enhanced software supply chain security across the entire development lifecycle.
Kubernetes Supply Chain Security - Building a Secure Software Factory
Explore Kubernetes supply chain security, software factory approaches, and defense strategies against attacks. Learn about signing, verification, and lessons from SUNBURST to enhance cloud-native security.
Open Tools for Secure Supply Chains in Kubernetes - From Release Engineering
Explore open-source tools for secure software supply chains, focusing on Kubernetes' journey to SLSA Level 3 compliance and how other projects can leverage these tools for enhanced security.
Software Supply Chain Aspects in Infrastructure as Code and How to Secure It
Explore software supply chain risks in Infrastructure as Code, learn about KICS for security, and discover strategies to safeguard your infrastructure from vulnerabilities in reused components.
Demystify Modern Signing: Keys, Certificates, and Envelopes
Explore practical aspects of cryptographic signing tools, covering key algorithms, signing envelopes, certificates, and verification, with a focus on identity-based signing using short-lived keys.
Secure Development with Docker - Workshop
Comprehensive workshop on securing software supply chains using Docker, covering common attacks, remediation strategies, and leveraging Docker Scout for actionable insights and early problem detection.
VEXinating Container Images: The European Approach to Software Supply Chain Security
Explore VEX implementation for container image security, addressing European legislation and enhancing software supply chain resilience through machine-readable vulnerability management.
Building the Software Supply Chain on Docker Official Images
Explore Docker's approach to securing the software supply chain, focusing on Official Images and integrating tools like SBOMs, cryptographic signing, and verification for enhanced developer security.
The Secure Software Supply Chain
Explore tools and live demos for securing the software supply chain, addressing industry-wide attacks and shifting approaches to writing and shipping software.
Emerging Best Practices in Software Supply Chain Security - What We Can Learn from Google, the White House, OWASP, and Gartner
Explore emerging best practices in software supply chain security, analyzing guidelines from major organizations to compile key strategies for mitigating risks in deployment pipelines.
Understanding Trust and Security Processes in the Open Source Software Ecosystem
Explores security challenges in open source software, including code review, dependency management, and trust issues. Shares insights from interviews and offers practical advice for improving supply chain security.
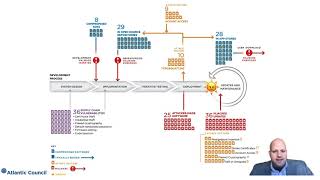
Breaking Trust – Shades of Crisis Across an Insecure Software Supply Chain
Explore software supply chain security threats, their impact, and potential solutions through analysis of 115 attacks and vulnerabilities from the past decade.
As Strong as the Weakest Link - Securing the Software Supply Chain
Explore software supply chain security, recent high-profile attacks, and defense strategies. Learn about dependencies, vulnerabilities, and best practices for protecting your production systems.
Management & Security at Scale with Docker Business
Explore Docker Business features for secure software supply chain management, team scalability, and image access control in enterprise development environments.
Take Your Projects to the Next Level with the Docker-Sponsored Open Source Program
Explore Docker's Open Source Program: Collaborate, innovate, and advance projects with enhanced benefits and criteria. Featuring insights from NYPL, Intel Owl, Jenkins, and nf-core.