Docker and Pyrsia - Securing the Software Supply Chain
Explore securing the open-source software supply chain with Pyrsia and Docker. Learn about vulnerabilities, exploits, and innovative solutions to enhance security in modern application development.
Transparency in the Software Supply Chain - Making SBOM a Reality
Explore the concept of Software Bill of Materials (SBOM) and its potential to enhance transparency in the software supply chain, discussing benefits, challenges, and implementation strategies.
Unearthing Malicious and Risky OpenSource Packages Using Packj
Explore PACKJ, a security framework for detecting risky open-source packages. Learn about supply chain attacks, defense strategies, and real-world examples to enhance your software security practices.
Zoom 0-Day - How Not to Handle a Vulnerability Report
Uncover the journey of a critical Zoom vulnerability, from discovery to disclosure, and its far-reaching implications for software security and responsible reporting practices.
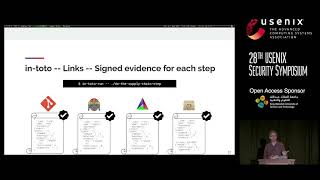
In-toto - Providing Farm-to-Table Guarantees for Bits and Bytes
Explore in-toto, a framework ensuring software supply chain integrity from inception to deployment, addressing vulnerabilities and protecting millions of users across various cloud environments.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
Securing the Software Supply Chain with the In-toto and SPIRE Projects
Explore securing software supply chains using in-toto and SPIRE projects. Learn about cryptographic attestation, automated certificate issuance, and building trust in software releases.
Securing Content Distribution with The Update Framework - TUF
Explore The Update Framework (TUF) for securing content distribution. Learn about its architecture, attack prevention, and real-world applications in cloud ecosystems and software supply chains.
On the Importance and Challenges of Reproducible Builds for Software Supply Chain Security
Explore the significance and hurdles of reproducible builds in enhancing software supply chain security, drawing insights from experts across renowned institutions.
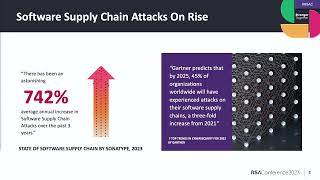
Scaling Software Supply Chain Source Security in Large Enterprises
Explore strategies for securing diverse software supply chains in large enterprises, including open-source, vendor, SaaS, and hardware. Learn to operationalize SBOMs for enhanced security and risk management.
Running in the Shadow - Perspectives on Securing the Software Supply Chain
Expert panel explores challenges and solutions for securing the software supply chain, offering insights from developer, CISO, and policymaker perspectives to address critical security issues.
Container Security
Explore container security fundamentals, shared kernel implications, and best practices with experts Liz Rice and Eoin Woods. Learn to assess and mitigate risks in containerized applications.
Software Supply Chain Security for Those in a Rush
Concise overview of software supply chain security concepts like SBOM, SLSA, and GUAC. Gain insights into emerging cybersecurity threats and their importance in the industry.
Demystify Secure Software Supply Chain Metadata
Explore secure software supply chain concepts, including SBOMs, SLSA, and attestations. Learn to create container images with signed metadata using Docker tools and GitHub Actions.

SLSA, SigStore, SBOM & Software Supply Chain Security - What Does It All Mean?
Demystifying software supply chain security: SLSA, SigStore, and SBOM explained. Learn about tools and methodologies to secure software from development to production in this comprehensive overview.
Securing CI/CD Pipelines - Exploring Vulnerabilities In Workflows
Explore security challenges in CI/CD platforms, focusing on GitHub Actions. Learn about threat modeling, taint tracking tools, and real-world vulnerabilities to enhance your software supply chain security.
How Much Do You Trust That Package? Understanding the Software Supply Chain
Explore software supply chain security risks, including package vulnerabilities and malicious code injection. Learn strategies to mitigate these risks in modern software development.
Are We Forever Doomed to Software Supply Chain Security?
Exploring software supply chain security challenges, from open-source vulnerabilities to cloud-native risks. Learn about developer-targeted attacks and the critical role of maintainers in safeguarding ecosystems.
Bad Actors vs Our Community - Detecting Software Supply Chain Attacks
Explore techniques used by bad actors in software supply chain attacks and learn about a large-scale vetting system for detecting malware in Python packages.
Securing the Open Source Software Supply Chain
Explore tools and best practices for securing the open-source software supply chain, addressing vulnerabilities, and enhancing trust in the ecosystem. Learn about recent developments and future improvements.
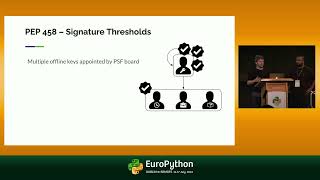
Implementing PEP 458 to Secure PyPI Downloads
Explore efforts to secure PyPI downloads through PEP 458 implementation. Learn about software repository attacks, The Update Framework, and the integration process with PyPI/Warehouse.