Enforcing a Secure Supply Chain on Kubernetes
Explore implementing and enforcing a secure supply chain in Kubernetes using open-source projects, including Sigstore keyless workflow and signature verification policies.
IoT Security - Ecosystem, Interoperability and Standards
Explore IoT security challenges and solutions with the Security & Privacy Development Lifecycle framework, addressing ecosystem complexities, privacy concerns, and compliance issues in rapidly evolving IoT landscapes.
Securing Your Infrastructure as Code Pipeline
Explore techniques for securing Infrastructure as Code pipelines, including static analysis, RBAC, and open-source tools like Open Policy Agent and Sigstore, to enhance productivity and compliance.
CRI-O's Graduation Celebration - Container Runtime Interface Overview and Future Plans
Explore CRI-O's CNCF graduation, architecture, and recent enhancements. Learn about its role as a stable, pluggable container runtime for Kubernetes and future project plans.
Creating Your First Snap Package - Interactive Workshop
Interactive workshop on creating Snap packages for Linux applications, featuring hands-on exercises with GTK/GNOME apps. Learn distribution-independent packaging for easy app distribution and installation across Linux systems.
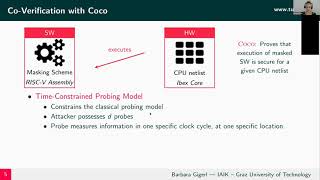
Co-Design and Co-Verification of Masked Software Implementations on CPUs
Explore co-design and co-verification of masked software implementations on CPUs, focusing on physical side-channel attacks, hardware/software gaps, and innovative solutions.
Hash Function Cryptanalysis - Techniques and Applications
Explore cryptanalysis techniques for hash functions, focusing on block ciphers and double block length constructions in this advanced cryptography session.
Hybrid Code Lifting - Award Paper Session
Explore cutting-edge research on hybrid code lifting techniques presented at Fast Software Encryption 2023, advancing the field of cryptography and software security.
Reproducible Builds for Ubuntu
Explore Ubuntu's reproducible builds effort, its progress compared to Debian, and potential community involvement in enhancing software transparency and security.
Fine-Grained Authorization with Topaz - Open Source Solutions
Explore Topaz: an innovative authorization engine uniting policy-as-code, relationship-based models, and real-time decision-making for enhanced security in zero-trust environments.
Control Flow Integrity on RISC-V
Explore hardware-assisted control flow integrity mechanisms for RISC-V, focusing on shadow stacks and landing pad instructions to enhance program safety and prevent memory-based attacks.
RISC-V-Based Sandboxing for Secure and Efficient Software Execution
Explore an efficient RISC-V virtual machine for sandboxed environments, featuring reduced memory usage and JIT compilation for secure software execution.
Securing the Container Supply Chain with Notary, TUF, and Gatekeeper
Explore container supply chain security using Notary, TUF, and Gatekeeper. Learn digital signature techniques and see a demo on implementing secure CI/CD processes and policy enforcement in Kubernetes clusters.
Open Tools for Secure Supply Chains in Kubernetes - From Release Engineering
Explore open-source tools for secure software supply chains, focusing on Kubernetes' journey to SLSA Level 3 compliance and how other projects can leverage these tools for enhanced security.
Linux Kernel Security Contributions by ANSSI
Explore ANSSI's contributions to Linux kernel security, including Landlock LSM and CLIP Linux. Learn about the benefits of open-source collaboration for government agencies and enterprises.

Securing the Continuous Integration Process
Explore best practices for integrating continuous integration securely into your software development lifecycle, focusing on technology and process changes rather than specific tools.
Making OpenSAMM More Effective in a DevOps World
Explore strategies to enhance OpenSAMM's effectiveness in DevOps environments, focusing on data-driven benchmarking, streamlined processes, and value communication for improved software assurance.
Patatt: End-to-End Patch Cryptographic Attestation for Patches
Learn about end-to-end cryptographic attestation for patches, exploring DKIM and Patatt solutions, their implementation, and best practices for secure patch management.
Demystify Modern Signing: Keys, Certificates, and Envelopes
Explore practical aspects of cryptographic signing tools, covering key algorithms, signing envelopes, certificates, and verification, with a focus on identity-based signing using short-lived keys.
How I Met Your Software - An Image's Journey of Consuming and Securing Software in Cloud Native
Explore software consumption in cloud-native environments, from distribution choices to Kubernetes workloads. Learn about trade-offs, security considerations, and optimizing image deployment.
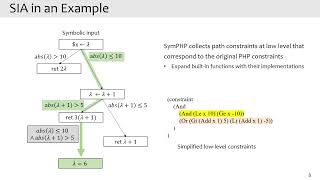
Holistic Concolic Execution for Dynamic Web Applications via Symbolic Interpreter Analysis - 2024
Explore advanced techniques for analyzing dynamic web applications using holistic concolic execution and symbolic interpreter analysis.