GitHub Copilot and Advanced Security - A Quick Tour
Explore GitHub Copilot's AI-powered development capabilities and GitHub Advanced Security's tools for identifying and fixing vulnerabilities, with live demonstrations and insights on enterprise applications.
Automated Modular Program Verification - From Testing to Mathematical Proofs
Dive into automated program verification techniques to mathematically prove software correctness, exploring tools, methodologies, and real-world applications like the Scion Internet Architecture.
Why AI Makes Us All Safety Engineers - Building Safety into AI Systems from the Start
Discover how AI's unique nature demands a new approach to software development, integrating safety and security considerations from the earliest stages of planning and design.
The GitHub Actions Worm - Understanding CI/CD Platform Vulnerabilities
Dive into the security vulnerabilities of GitHub Actions, exploring how malicious code can spread through Action dependencies and learning essential defense strategies against CI/CD platform attacks.
Securing GitOps Supply Chain with Sigstore and Kyverno
Learn to secure GitOps supply chain by signing and verifying container images using Sigstore and Kyverno, eliminating security risks and ensuring only trusted images are deployed in Kubernetes clusters.
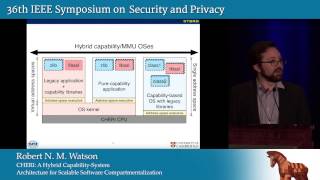
CHERI - A Hybrid Capability-System Architecture for Scalable Software Compartmentalization
Explores CHERI architecture for enhanced memory protection and software compartmentalization, demonstrating improved scalability and security benefits over traditional MMU designs.
Security While Scaling Agile - Lessons Learned
Integrating software security practices into scaled Agile frameworks: strategies, challenges, and lessons learned for maintaining security without impeding product delivery.
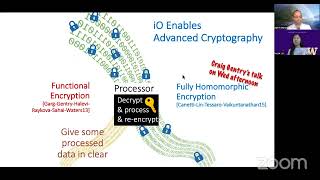
The Mathematics of Hiding Secrets in Software
Explore indistinguishability obfuscation, a powerful cryptographic tool for transforming programs into incomprehensible yet functionally equivalent versions, and its applications in securing software.
Securing Kubernetes Manifests with Sigstore and Kyverno
Learn to secure Kubernetes resources using Sigstore for signing YAML definitions and Kyverno for verification during admission controls, with real-world use cases for tamper-prevention and approval workflows.
Building Images for the Secure Supply Chain
Techniques and tools for building secure container images, including distroless philosophy, updating dependencies, using apko for reproducibility, and signing with Sigstore.
Trust But Verify: Bringing Supply Chain Integrity to CD GitOps
Explore how to enhance CD GitOps with supply chain controls, ensuring integrity and tamper-proof deployments through keyless signing, transparency logs, and cluster enforcement of signatures and policies.
CRI-O's Senior Year - Overview and New Developments
Explore CRI-O's journey towards CNCF graduation, including new developments like conmon-rs, sigstore integration, and Kubernetes alignment for enhanced container runtime stability and security.
Who's Verifying Your Signatures? Approaching Private Container Image Signing
Explore container image signing for private use, comparing open-source and internal challenges. Learn about leading frameworks and their scalability for secure software delivery.
Sigstore - How We Learned to Stop Trusting Registries and Love Signatures
Explore InfluxData's journey in implementing container image signing for their SaaS offering, covering the process, challenges, and technical details from DevOps and security perspectives.
Securing the IaC Supply Chain
Explore securing Infrastructure as Code supply chains, applying software security principles to IaC pipelines. Learn about Crossplane's integration with Sigstore for enhanced provenance and attestations.
Life of a CVE with Ingress-Nginx - Understanding the Project's Release Cycle
Explore Ingress-Nginx's release cycle, security measures, and ongoing improvements. Learn about efforts to enhance release processes, reduce complexity, and maintain CVE-free status in this critical Kubernetes component.
Zero Trust Workload Identity in Kubernetes
Explore Zero Trust principles in Kubernetes using SIFFE and Spire for workload identity-based authorization, eliminating the need for secrets and enhancing security across service meshes.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Unicodes Gone Wild - Handling Unicode Oddities and Problems
Explore Unicode oddities and common handling issues in operating systems, applications, and frameworks. Gain insights into proper Unicode implementation for enhanced application security.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
Using Docker Content Trust with Kubernetes Admission Controllers to Secure Runtime
Enhance container security by implementing image signing in CI/CD pipelines and restricting Kubernetes deployments to verified images using TUF/Notary and admission controllers.