Fuzzing the CNCF Landscape - Challenges and Results
Explore fuzzing techniques applied to CNCF projects, including Kubernetes and Etcd. Learn about challenges, results, and continuous integration with OSS-Fuzz for enhanced security.
Fuzz Testing of Envoy - Ensuring Security and Correctness
Explore Envoy's fuzz testing techniques, goals, and implementation for enhanced security and reliability in handling untrusted inputs and complex edge cases.
Securing Fluent Bit by Way of Fuzzing
Explore automated security testing for Fluent Bit using fuzzing techniques. Learn about implementation, bug detection, and the impact on overall security posture.
The Risks of Single Maintainer Dependencies
Explore challenges and implications of single maintainer dependencies in open-source projects, focusing on Cobra library and its impact on CNCF ecosystem. Insights on contributor community and secure software supply chain.
SBOM X-Ray Superpowers: Making Better SBOMs and Using SBOMs
Explore innovative techniques for enhancing SBOM accuracy and completeness using SBOM discovery, look-up, and transparency logs. Learn to leverage these methods to improve software security and vulnerability response.
Verifiable Build Environments in the Cloud - Powered by Sigstore and Enclaves
Explore how Sigstore enhances confidential computing security, minimizing trusted compute base while maintaining engineering velocity. Learn about cloud-based verifiable build environments.
Fuzzing - Finding Bugs and Vulnerabilities Automatically
Explore automated bug and vulnerability detection through fuzzing. Learn techniques, case studies, and key open-source projects for effective software testing and security enhancement.
Grip on Secure Software Development - Dutch Government Standard for Outsourcing - AppSecEU 2016
Learn about the Dutch government's standard for secure outsourcing, exploring key principles and practices for effective implementation in software development projects.
Security Touchpoints When Acquiring Software
Explore key security considerations and touchpoints in software acquisition, focusing on best practices for ensuring secure integration of third-party solutions.
Leveraging the ASVS in the Secure Software Development Lifecycle
Integrating OWASP ASVS into the secure software development lifecycle to create uniform security requirements, prioritize tasks, and track adherence across applications using existing tools and processes.
Java LangSec - New Security Controls in Java 8 and 9
Explore new security controls in Java 8 and 9 with expert Jim Manico. Learn about Java LangSec and enhance your secure coding practices for web applications.
A Static Tainting Analysis Method for Aspect-Oriented Programs
Introduces a new method for detecting vulnerabilities in aspect-oriented web applications, focusing on static tainting analysis to improve security in languages like AspectJ.
Turning Engineers into Extended Blue Team Members - Security Strategies
Strategies for empowering engineers to become part of the security team, including threat modeling, incident-driven learning, and security testing integration into development processes.
Real World Static Analysis for Real Humans
Explore practical static analysis techniques for software security, focusing on real-world applications and human-centric approaches to code analysis.
Top Ten Proactive Web Application Controls
Learn essential proactive controls for securing web applications, focusing on key strategies to prevent vulnerabilities and enhance overall security posture.
Going Beyond Metadata - Adopting Static Analysis in Dependency Tools
Explore the importance of static analysis in dependency tools for enhanced software security and reliability beyond traditional metadata approaches.
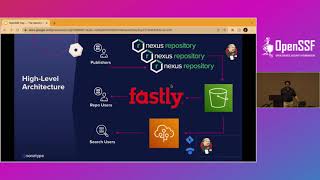
The Secret Life of Maven Central
Explore Maven Central's history, architecture, and security measures, including responses to critical events like Log4Shell and future directions for this vital Java ecosystem service.
Purl and Vers: Universal Package URL and Version Ranges Identifiers for Dependencies and Vulnerabilities
Explore universal identifiers for software dependencies and vulnerabilities, enhancing package management and security across diverse ecosystems.
What Makes a Build Reproducible?
Explore the concept of reproducible builds with VMware experts, focusing on key factors that ensure consistent and verifiable software compilation across different environments.
AMD Hypervisor Implementation in Rust
Explore the process of creating an AMD hypervisor using Rust, discussing its applications in FaaS, virtual machines, and security, as well as potential misuse in malware and game hacks.
Mobile Application Security Testing - Journey to Version 2.0
Explore the evolution of mobile app security standards and best practices in this insightful talk on the journey to OWASP Mobile Security Testing Guide v2.0.