Sigstore: Using Transparent Digital Signatures to Help Secure the Software Supply Chain
Explore transparent digital signatures with Sigstore to enhance software supply chain security and learn practical implementation strategies.
The OpenSSF Best Practices Badge Program for Open-Source Software Quality
Explore resources for creating and maintaining robust, high-quality, and secure open-source software through the OpenSSF Best Practices Badge Program.
Implementing DevSecOps in Production with Stackrox and Tekton
Implement robust DevSecOps pipelines using Stackrox and Tekton. Eliminate security risks, secure the software supply chain, and provide automated guardrails for developers.

Anchore Engine: DevSecOps Tool for Inspection, Analysis, and Certification of Infrastructure
Explore Anchore Engine for inspecting, analyzing, and certifying infrastructure, enhancing security in application development and QA processes.
Practical DevSecOps Transformation - 5 Key Tips for Building a Successful DevSecOps Program
Discover 5 essential tips for implementing a successful DevSecOps transformation, integrating security into development and operations workflows for robust software delivery.
AI for DevSecOps Engineers - Enhancing Security Culture and Education
Explore AI technologies to enhance security testing, analysis, and education for DevSecOps engineers. Learn to automate processes, identify threats, and improve software quality in CI/CD environments.
Securing Software That Will Change the World
Explore innovative technologies and learn strategies to secure software that will shape the future. Gain insights from global engineers on protecting transformative systems.
Motivating Developers to Engage in DevSecOps - Hands-on Docker Security
Dive into DevSecOps with hands-on Docker activities, learning to identify and prevent vulnerabilities while strengthening your software security skills.
Unveiling Invisible Vulnerabilities: Proactive Strategies for Early Detection
Explore proactive strategies for early vulnerability detection in DevSecOps. Learn how Secure Code Review transforms software security, uncovering hidden threats and fortifying digital ecosystems.
Building Your First DevSecOps Pipeline
Demystify DevSecOps and build a functional pipeline with cutting-edge security testing, including SCA, SAST, and DAST tooling. Supercharge software security and achieve true "Shift Left" success.
How Hacking Works - Web Edition - NDC Oslo 2024
Explore web exploitation techniques and tools to enhance software security through gamified environments. Learn to think like a hacker for safer development.
DCMS' Approach to Software Security and Resilience Policy
Explore DCMS' approach to software security and resilience policy with insights from Naomi Gilbert, Head of Cyber Resilience Policy at the Department of Culture Media & Sport.
The Need for Software Bills of Materials (SBOMs) - Why You Should Disclose Your Software Usage
Explore the importance of Software Bills of Materials (SBOMs) in modern software development and understand their role in enhancing transparency and security.
CVE Triage, CVE Checker Analysis, and Vendor PR in Yocto Project Security - YPS 2023.11
Explore CVE triage initiatives, SRTool enhancements for CVE Checker analysis, and potential "vendor_pr" system to address package patching recognition in Yocto Project security.
Let Devs Be Devs Without Sacrificing Security
Explore flexible, secure CI pipelines using Tekton, Chains, and Enterprise Contract to balance developer innovation with robust security measures for various software targets.
Enforcing Organization Policies with Enterprise Contract
Learn to enforce organizational policies on container images using Enterprise Contract, leveraging Sigstore signatures and in-toto attestations within the Tekton ecosystem.
Reviewing NuGet Packages Security Using OpenSSF Scorecard
Explore OpenSSF Scorecard for assessing NuGet package security. Learn to evaluate maintenance, workflows, and security tools to improve application safety and make informed decisions.
Secure Software Supply Chain: Current State in PHP and Drupal Ecosystem
Explore the secure software supply chain, recent global events, and tools for digital signatures, SBOM generation, and vulnerability scanning in PHP and Drupal projects.
Counting Down for CRA - Updates and Expectations
Explore the EU's Cyber Resilience Act: timeline, critical discussions, and new responsibilities for software developers. Learn about PSF's preparations and how to ready your Python projects for increased security liability.
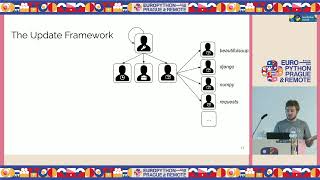
TUF Joins PyPI - Securing Package Delivery with The Update Framework
Explore TUF integration with PyPI using RSTUF, addressing security challenges in package delivery and updates. Learn about PEP 458 and Warehouse implementation.
Keep Your Dependencies in Check
Explore tools and strategies for efficiently managing and updating dependencies to enhance application security and maintain business value delivery.