Leveraging SBOMs to Automate Packaging, Transfer, and Reporting of Dependencies Between Secure Environments
Explore innovative uses of Software Bill of Materials (SBOMs) for secure asset transfer, dependency management, and cloud-native infrastructure deployments using CycloneDX and open-source tools.
How to Trust Your Open Source Software Using Scorecards
Explore OSSF Scorecards to assess open source software health, automate risk evaluation, and build dependency policies for informed decision-making in software development.
Kubernetes Community Days: Impact, Organization, and Benefits
Discover the impact of Kubernetes Community Days, learn how to organize successful events, and explore ways to contribute to the cloud native community without coding.

SBOMs, VEX, and Kubernetes - Software Supply Chain Security in Cloud Native Environments
Explore software supply chain security with experts discussing SBOMs, VEX, and their practical applications in Kubernetes environments, from open-source projects to regulated industries.
Secure Your Project with the SIG Release Supply Chain Kit
Explore tools for enhancing supply chain security in open-source projects, including SBOMs, signed attestations, and secure release pages. Learn how to implement these features using reusable GitHub actions.
Updates from The Update Framework
Explore The Update Framework's role in secure content delivery, its protection against supply chain attacks, and its evolving ecosystem with insights from TUF maintainers.
Green Software and Open Hardware: Addressing Ecological Impact in IT
Exploring the ecological impact of software and IT infrastructure, discussing best practices and technologies to reduce the carbon footprint of digital systems and data centers.
How to Reduce CVE Noise with VEX - Vulnerability-Exploitability eXchange
Explore VEX, a tool to enhance vulnerability management by providing context to CVEs, improving risk assessment, and streamlining communication between vendors and consumers.
An Open Source Telco Cloud Stack to Accelerate Cloud Native Operator Model Adoption
Explore an open-source Telco Cloud stack for 5G CNF support, featuring cloud-native infrastructure, scalability, and automation. Learn about its ecosystem integration and see a demo of distributed lab testing.
Dissecting the 0-Day Supply Chain Vulnerability in Argo CD
Explore the discovery and implications of a critical 0-day vulnerability in Argo CD, including attack methods, remediation steps, and its impact on the ecosystem.
Securing Your Container Native Supply Chain with SLSA, GitHub and Tekton
Practical guide to securing container native supply chains using SLSA principles, in-toto attestations, and step-by-step demos for achieving SLSA Level 2 in Tekton and Github Actions.
Cybersecurity Integration from the Beginning - Perils and Benefits
Explores challenges and benefits of integrating cybersecurity from project inception, offering insights on overcoming resistance, developing secure designs, and building value chains in early-stage cybersecurity implementation.
Overcoming Barriers in Security DSLs with BabbelPhish - Empowering Detection Engineers
Explore BabbelPhish, an innovative approach using large language models to bridge natural language queries and security DSLs, streamlining threat detection and making detection-as-code platforms more accessible.
Building Secure Hybrid Mobile Applications - A Security Professional's Guide
Learn to assess and secure hybrid mobile apps by understanding threat models and vetting external libraries, enhancing your ability to build robust applications.
Security Risks of Low-Code/No-Code Applications - What Could Go Wrong?
Explores security risks of low-code/no-code platforms used by business professionals. Presents research findings, demonstrates common security issues, and introduces OWASP framework for mitigating risks in business-led development.
Perfect Vulnerability Reports and Still Getting Hacked - Limitations of Security Tools
Explore limitations of vulnerability detection tools, challenges in vulnerability management, and strategies for improving application security despite imperfect reporting systems.
The Importance of Engineering Privacy From the Start
Explore strategies for protecting user data and identity in software development, emphasizing the ethical responsibility of engineers as stewards of sensitive information.
Hiding in Plain Sight - The Untold Story of Hidden Vulnerabilities
Uncover limitations of vulnerability scanners and SCA tools through groundbreaking research. Learn about hidden vulnerabilities, scanner blindspots, and the need for holistic software security approaches.
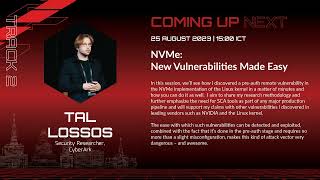
NVMe: New Vulnerabilities Made Easy - Exploiting Cloud Storage Protocols
Exploring pre-auth remote vulnerabilities in NVMe implementation, emphasizing the importance of SCA tools in production pipelines and showcasing discoveries in Linux kernel and NVIDIA.
Analyzing Cellular Basebands with FirmWire
Explore FirmWire, an open-source platform for analyzing cellular basebands. Learn about baseband vulnerabilities, emulation techniques, and how to uncover security flaws in LTE and GSM stacks.
Ethical Hacking: Good Intentions and Questionable Outcomes
Explore ethical boundaries in security testing, from fuzzing servers to buying dark web credentials. Discuss grey areas and the need for beneficial practices that maintain moral high ground.