Cloud Native Evolution in Telecom Infrastructure
Exploring telecom operators' visions for cloud-native infrastructure, addressing challenges, and discussing collaboration with CNCF communities to shape the future of telecom networks.
Automated Incident Response - Streamlining Processes and Enhancing Efficiency
Explore innovative Slack-based tools for streamlining incident response processes, reducing overhead, and enhancing efficiency through automation and integration with critical cloud-based systems.
Cyber Resilience Act: Concerns for Open Source Software Development
Explores EU's Cyber Resilience Act's impact on open source software, highlighting concerns about lack of consultation with experts and potential burdens on developers. Discusses Linux Foundation's efforts to address these issues.
SBOMs - Are They a Threat or a Menace?
Explore the implications of Software Bill of Materials (SBOMs) in cybersecurity, examining their potential benefits and challenges for software supply chain management.
Writing a New Decompiler for JRuby Security Audits
Explore JRuby vulnerabilities and learn about YBurj, a new open-source decompiler for JRuby IR, enabling recovery of compiled source code for enhanced security audits.
Designing Your Own Electronic Attack Device
Learn to design and create custom electronic attack devices, from circuit boards to complete Linux systems, for personalized and efficient security testing and penetration tasks.
Exploiting the Lexmark PostScript Stack
Explore Lexmark PostScript stack exploitation, covering internals, language basics, mitigations, and achieving remote code execution through out-of-bounds read and type confusion vulnerabilities.
The Future of Hacking: OpenAI's GPT-4 Code Interpreter - Cybersecurity Applications
Explore AI's potential in cybersecurity with GPT-4 Code Interpreter. Learn to simplify complex issues, analyze diverse programming languages, and manage cryptocurrency data for enhanced bug hunting and communication.
Mender - Current and Future Status of Open Source OTA Updates for Embedded Systems
Explore Mender's open-source project for OTA updates to embedded systems. Learn about challenges, solutions, and future developments in this informative session.
Grow Your Own Community - Lessons from Kubernetes Community Days in Europe
Insights and best practices for organizing successful Kubernetes Community Days events in Europe, covering team building, diversity, logistics, sponsorship, and finances.
Making Sense of Security Supply Chain - An Overview for Beginners
Explore supply chain security fundamentals, tools like Fulcio, Rekor, and cosign, and their integration in this beginner-friendly overview of the rapidly evolving landscape.
Cyber Gym: Open-source Security Labs in Google Cloud
Hands-on Google Cloud environment for cybersecurity training, offering customizable workouts mapped to industry standards. Flexible for instructors and students, with automated assessment and scalable deployment.
Securing Software Supply Chains with In-Toto
Explore in-toto, a framework for securing software supply chains, and learn its implementation strategies for enhancing cybersecurity in software development processes.
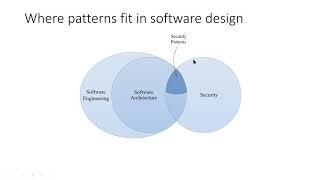
Building Secure Software Systems Using Security Patterns
Learn to create secure software systems using proven security patterns, enhancing your ability to design robust and protected applications in today's cybersecurity landscape.
SPDX 3.0 Update
Learn about the latest updates and improvements in SPDX 3.0, exploring its enhanced capabilities for software bill of materials (SBOM) and supply chain security.
Beyond the Trend: Authentic Approaches to Fostering Diversity in Open Source
Explore authentic approaches to fostering diversity in open source, avoiding common pitfalls and implementing concrete strategies for genuine inclusivity, based on a blind woman's tech journey.
The Future of the Internet - A Mozilla Perspective
Explore Mozilla's vision for the internet's future, addressing challenges like closed systems, surveillance, and data privacy while discussing aspirations for a free and open web.
Smarter Than Your Average SBOM - Understanding the SBOM Lifecycle
Explore the SBOM lifecycle, including creation, storage, distribution, trust verification, and enrichment. Learn about emerging practices and companion formats in software security.
Understanding the Sec in DevSecOps: Beyond Just Shifting Left
Explore attack vectors, preventive measures, and compliance strategies in DevSecOps. Learn innovative approaches to enhance software security beyond shifting left.
SEAPATH: A LF Energy Project for Critical Infrastructure with Emphasis on Software Supply Chain Security
Explore SEAPATH, an LFEnergy project revolutionizing electrical grid substations through virtualization, enhancing adaptability and interconnections while prioritizing reliability and cybersecurity for critical infrastructure.
Security Research with Open Source Software - Volume Omega
Explore open source software security with the OpenSSF Alpha-Omega team. Learn about automated security patches, vulnerability research, and tools to address global security concerns in the OSS ecosystem.