Building with Privacy by Design
Explore privacy-by-design principles and their practical implementation in software development, enhancing user trust and data protection.
Building SLSA 3 Conformant Attestors for Artifacts Generated on GitHub
Learn to create SLSA 3 compliant attestors for GitHub artifacts, enhancing software supply chain security with minimal effort using recent framework extensions.
Improve Vulnerability Management with OCI Artifacts - It Is That Easy
Learn to enhance vulnerability management using OCI artifacts. Discover how to efficiently utilize SBOMs, signed attestations, and open-source tools for improved supply chain security at scale.
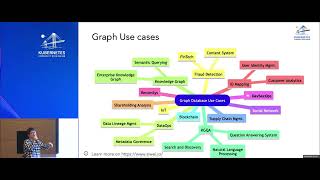
Graph Driven DevSecOps in Practice
Explore graph-driven DevSecOps implementation strategies, enhancing security integration in cloud-native development pipelines for improved efficiency and risk mitigation.
Software Bill of Materials (SBOM) in Kubernetes - Best Practices and Approaches
Explore SBOM implementation in Kubernetes, comparing approaches and best practices. Learn how Paketo Buildpacks embeds SBOMs in application images using Syft, enhancing software supply chain security.
What Data Tells Us About Software Supply Chain Security and What To Do About It
Experts analyze data from surveys and reports on cloud-native and open source software security, providing actionable insights to improve software supply chain security for organizations and projects.
Securing Open Source Software Supply Chain - Continuous Secure Software Ingestion
Explore secure OSS ingestion in enterprises using Continuous Secure Software Ingestion (CSSI) application, built on Tekton & Open Policy Agent, for automated artifact grooming and policy-driven security checks.
Lessons Learned from Securing 40,000 C++ Packages with Conan.io
Discover how Conan.io maintains zero security incidents while managing 11 million C/C++ binaries. Learn about automated checks, compiler mitigations, and efficient review processes for package security.

Secure CI/CD Using JSON Web Token (JWT)
Explore how GitLab leverages JWT for secure access to secret management solutions, enhancing DevSecOps practices and addressing challenges in retrieving sensitive data across cloud providers.
Sigstore for Python Packaging - Next Steps for Adoption
Explore Sigstore integration in Python packaging, its benefits for users, and strategies for adoption. Learn about enhancing security in package publishing and consumption workflows.
SBOM is Coming - Why You Should Care and How You Can Help
Explore the importance of Software Bill of Materials (SBOM) in cloud-native ecosystems, its impact on security, and how you can contribute to its implementation and adoption.
Sigstore: Evolution and Future of Software Security Signing
Explore Sigstore's journey in software security signing, its impact on Kubernetes, and future directions. Learn about supply chain security and cutting-edge cryptographic technologies.
SBOM: The Rest of the Story - Understanding Software Bill of Materials
Experts discuss Software Bill of Materials (SBOM), addressing misconceptions, sharing challenges, and exploring implementation strategies for enhanced software supply chain security.
Telepresence Case Studies - From First Experience to Fast Feedback at Scale
Explore how Telepresence improves developer experience, accelerates inner dev loops, and reduces costs in microservice-based applications. Learn implementation through case studies and a demo.
Looking Ahead to the Future with Project Sylva - Energy Efficiency and Telco Cloud Platforms
Exploring Project Sylva's impact on telco cloud platforms, focusing on energy efficiency, sustainability, and cloud-native innovations in the European telecommunications industry.
OmniBOR: Bringing the Receipts for Supply Chain Security
Discover OmniBOR, a revolutionary approach to capture artifact dependency graphs in software development, enhancing supply chain security and reducing false positives in vulnerability scanning.
Security as Code - A DevSecOps Approach
Explore DevSecOps and Security as Code with CodeQL. Learn to implement security checks, detect vulnerabilities, and foster collaboration between development and security teams for a robust security culture.
Software Supply Chain Security with TAG Security
Explore software supply chain security with insights on guidance, resources, and recent developments. Learn about the whitepaper, compromise catalog, and reference architecture for secure supply chains.
From Illuminating to Eliminating Crypto Jacking Techniques in Cloud Native
Explore cryptojacking evolution in cloud environments, from basic attacks to sophisticated techniques targeting containers and Kubernetes. Learn proactive protection strategies using open-source tools for enhanced security.
Securing Diverse Supply Chains Across Interconnected Systems
Explore how SpaceX integrates SBOM and vulnerability discovery tools to enhance security across diverse software systems, reducing response time and improving prioritization for developers.
Learning from Supply Chain Failures and Best Practices in Other Industries
Explore supply chain best practices and failures across industries to enhance software supply chain security. Gain insights from physical world processes and apply lessons to critical infrastructure protection.