Cuckoo for Malware - Cuckoo Sandbox and Dynamic Malware Analysis
Explore dynamic malware analysis using Cuckoo Sandbox, covering setup, features, and practical applications for effective threat detection and analysis.
Getting Permission to Break Things
Learn ethical hacking techniques, navigate legal issues, and gain stakeholder buy-in for security testing. Discover how to define scope, address client needs, and handle potential pitfalls in penetration testing.
Cross Origin Resource Sharing Kung Fu
Explore Cross-Origin Resource Sharing (CORS) security implications, common developer mistakes, and best practices for implementing secure web applications.
Intro to Fuzzing for Fun and Profit
Explore fuzzing techniques for software security, covering tools like AFL and Python fuzzers, memory error detection, debugging strategies, and advanced fuzzing methods.
Hacking the Sabbath
Explore the intersection of technology and religious observance, examining innovative solutions for maintaining Sabbath traditions in the modern digital age.
What I've Learned Writing CTF Challenges
Insights from creating Capture The Flag challenges, covering design, development, deployment, and best practices for reliable and educational cybersecurity competitions.
0 to 31337 Real Quick - Lessons Learned by Reversing the Flare On Challenge
Explore reverse engineering strategies and anti-analysis techniques through lessons learned from the Flare-On Challenge, covering file types, encryption methods, and obfuscation tactics.
From Zero to Bender in 12 Months - How a Software Guy Turned Hardware
Learn how a software developer transitioned to hardware hacking, exploring the journey from novice to expert in just one year. Gain insights into the challenges and rewards of this exciting field.
Springtime for Code Reviews - Ryan Goltry
Discover effective code review techniques, focusing on security vulnerabilities, validation, and best practices to enhance software quality and maintainability.
Threat Modeling 101
Learn essential threat modeling techniques to identify and mitigate security risks in software systems, enhancing your ability to build robust and secure applications.
You Have Updates - A Look at an Old Tool Making a Comeback - Evilgrade
Explore Evilgrade, a resurgent tool for exploiting software update processes, and learn about its attack structure, technical factors, and potential applications.
The AppSec Starter Kit
Learn essential tools and techniques for application security, including vulnerability assessment and penetration testing, from expert Timothy De Block.
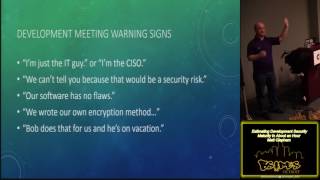
Estimating Development Security Maturity in About an Hour
Discover techniques for assessing development security maturity quickly. Learn to identify key behaviors, conduct effective meetings, and evaluate training, threat modeling, and analysis practices.
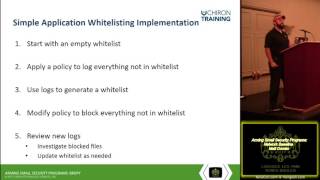
Arming Small Security Programs - Network Baseline - Matt Domko
Learn to establish network baselines for small security programs, covering malware detection, logging, and traffic analysis using tools like Bro and Security Onion.
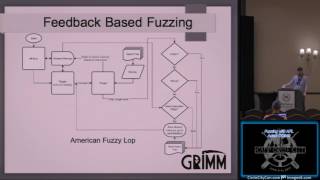
Fuzzing with AFL
Explore fuzzing with AFL, covering traditional methods, monitoring execution, and applications in Google and Windows. Learn about limitations, instrumented fuzzing, and open problems in this field.
Morning Keynote
Explore cybersecurity challenges in healthcare, including patching complexities, system dependencies, and the need for sustainable solutions in an evolving threat landscape.
Better Manual Web Application Testing Through Automation
Learn techniques to enhance manual web app testing with automation, improving efficiency and effectiveness in identifying vulnerabilities and security issues.
JReFrameworker One Year Later
Explore Java-based managed code rootkits with JReFrameworker. Learn techniques for adding, replacing, and merging code, as well as improvements in annotations, building, and backdoor creation.
Kali Linux Johnny Long
Explore advanced hacking techniques and tools with renowned security expert Johnny Long, focusing on the powerful Kali Linux distribution for penetration testing and ethical hacking.
Web Application Testing Approach and Cheating to Win
Learn effective web application testing techniques and strategies to uncover vulnerabilities, including unconventional methods for successful penetration testing.
Drone Delivered Attack Platform DDAP
Explore the design, components, and potential applications of a drone-based attack platform, including hardware options and remote access capabilities.