Automating Security Testing with the OWTF
Learn to automate security testing using OWTF, enhancing efficiency and effectiveness in identifying vulnerabilities and strengthening web application defenses.
Active Defense - Helping Threat Actors Hack Themselves
Explore innovative active defense strategies to turn the tables on cyber threats, helping attackers inadvertently compromise themselves while protecting legitimate users.
Leveraging DevSecOps to Escape the Hamster Wheel of Never Ending Security Failures
Explore DevSecOps strategies to break free from recurring security failures, focusing on integration, collaboration, and proactive measures in software development.
How to Conduct a Product Security Test and How it Fits Into the Larger Security Strategy
Learn how to conduct thorough product security tests, from initial investigation to reporting, using various tools and techniques for static and dynamic analysis, fuzzing, and ethical hacking.
CTF Tips and Tricks
Explore CTF design strategies to create engaging, accessible challenges. Learn tips for crafting immersive stories, reducing barriers, and fostering lateral thinking in cybersecurity competitions.
Abuse Case Testing in DevOps
Explore abuse case testing in DevOps, covering threat modeling, test development, and integration. Learn to enhance application security through continuous improvement and monitoring.
Lessons Learned from Development and Release of Blacksmith - The Meltdown
Explore memory side channel attacks, speculative execution, and Meltdown vulnerability. Learn about Blacksmith, an autonomous endpoint protection tool, and its development challenges.
Reflective PE Unloading
Explore reflective PE unloading techniques, their importance in cybersecurity, and practical applications through code analysis and comparisons using tools like IDA Pro and PE Bear.
My First Year in Application Security
Insights and experiences from a first year in application security, offering valuable lessons and perspectives for those entering or interested in the field.
InSpec Compliance as Code
Explore InSpec for compliance-as-code, learning how to automate security and compliance testing in infrastructure and applications.
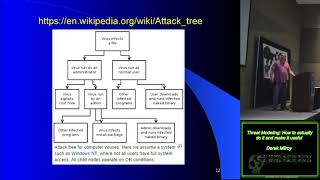
Threat Modeling - How to Actually Do It and Make It Useful
Learn practical threat modeling techniques for effective cybersecurity. Explore various methodologies, tools, and frameworks to identify and mitigate potential risks in software and systems.
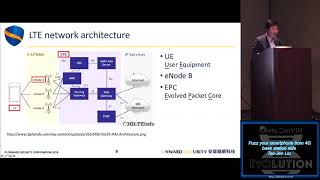
Fuzz Your Smartphone from 4G Base Station Side
Explore smartphone vulnerabilities through 4G base station fuzzing techniques, enhancing mobile security knowledge and practical skills.
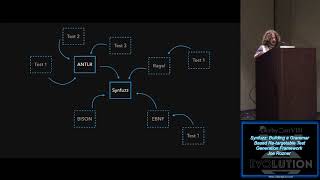
Synfuzz - Building a Grammar Based Retargetable Test Generation Framework
Explore a grammar-based, retargetable test generation framework for efficient and comprehensive software testing, enhancing security and reliability.
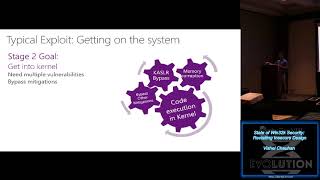
State of Win32k Security - Revisiting Insecure Design
Explore Win32k security vulnerabilities and design flaws, focusing on recent developments and potential attack vectors in Windows operating systems.
Hacking Mobile Applications with Frida
Learn to hack mobile apps using Frida, a dynamic instrumentation toolkit. Explore techniques for analyzing and modifying app behavior in real-time on iOS and Android platforms.
Web App Testing Classroom in a Box - The Good, the Bad, and the Ugly
Explore web app testing strategies, from ideal scenarios to real-world challenges. Learn effective techniques for red and blue teams, ethical hacking, and auditing.
Mixing and Baking a New AppSec Person - Some Missing Audio
Learn strategies for developing application security professionals, including key skills, training approaches, and industry best practices.
API Security Tokens Flows and the Big Bad Wolf
Explore API security, authorization flows, and authentication methods to protect digital resources from potential threats and ensure secure access in modern applications.
Keynote - The Declarative Future
Explore the future of cybersecurity with insights on containerization, declarative systems, and the psychology of app development. Learn about emerging trends and strategies for a more secure digital landscape.
Its Malware Time - A Bar Crawl from Skunked Homebrew to Rotten Apples
Explore the evolution of malware through real-world examples, from initial infection to advanced techniques. Learn detection and prevention strategies for various attack vectors.
Empathy for the Developer - Lessons Learned Building an Application Security Module
Explore lessons learned in building an application security module, focusing on developer empathy and effective security implementation strategies.