Track202 Building a Sturdy Foundation - A Program Based Approach to IT Operations Application Development
Explore a program-based approach to IT Operations and Application Development, focusing on building a robust foundation for organizational success.
Getting the Data Out Using Social Media
Explore techniques for data exfiltration using social media platforms, including testing, demos, and defensive strategies. Learn about multichannel capabilities and message size limits.
Crema - A LangSec Inspired Language
Explore LangSec principles and the Crema language for secure programming, focusing on least computational privilege and sub-Turing execution to enhance software security.
Harvesting Passwords from Source Code Scripts and Code Repositories
Explore techniques for extracting passwords from source code, scripts, and repositories, enhancing security awareness and vulnerability detection skills.
Hacking Virtual Appliances
Explore techniques for hacking virtual appliances, including command injection, filesystem analysis, and undocumented accounts. Learn about security vulnerabilities and vendor communication.
Mobile Application Reverse Engineering Under the Hood
Explore mobile app reverse engineering techniques, from sensitive data extraction to analyzing Android package files, with practical tools and methods for both iOS and Android platforms.
Dynamic Analysis of Flash Files
Dynamic analysis techniques for Flash files, exploring methods to uncover vulnerabilities and potential security risks in SWF content.
Stable35 Spy Vs Spy - How to Use Breakable Dependencies to Your Advantage
Learn to leverage breakable dependencies strategically in cybersecurity, exploring techniques to gain advantages in offensive and defensive operations.
The Problems with JNI Obfuscation in the Android Operating System
Explore JNI obfuscation issues in Android OS, covering build process, software stack, and practical reverse engineering techniques for both static and dynamic analysis.
My Little P0ny - What You Can Do With 20 Lines of Code and an Open Machine
Explore the potential of minimal code and open machines, demonstrating powerful capabilities achievable with just 20 lines of programming in a security context.
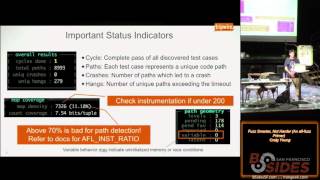
Fuzz Smarter Not Harder - An AFL Fuzz Primer
Explore advanced fuzzing techniques with AFL, including parallel and LLVM fuzzing, persistent mode, and crash assessment. Learn to optimize your fuzzing process for better vulnerability detection.
Building an Application Security Program
Strategies for establishing and expanding an effective application security program, including policy development, metrics, and alignment with software development lifecycle.
IAST Deep Dive - Understanding Interactive Application Security Testing
Explore Interactive Application Security Testing (IAST) with Ofer Maor, covering automation, integration, and real-world cases to enhance agile security practices and continuous integration.
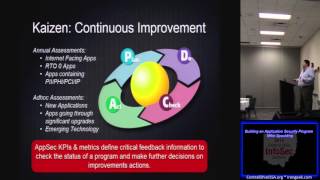
Building an Application Security Program
Aprenda a construir um programa de segurança de aplicações eficaz, abordando análise estática e dinâmica, verificação manual e melhoria contínua para reduzir riscos e alinhar-se ao ciclo de desenvolvimento.
Fail Now So I Don't Fail Later - A Look into Security Testing and Training Methodologies
Explore security testing and training methodologies to prevent data breaches. Learn about network infrastructure, prevention techniques, two-factor authentication, and effective detection strategies.
AppSec Without Additional Tools
Learn application security integration techniques, from requirements to operations, without additional tools. Explore best practices, dynamic and static scanning, and continuous integration for successful AppSec implementation.
Hacking Web Apps
Learn techniques for identifying and exploiting web application vulnerabilities, focusing on practical methods to enhance security testing skills.
Don't Be Stupid with GitHub - Metacortex
Learn best practices for secure GitHub usage, avoiding common pitfalls and protecting sensitive information in repositories. Enhance your development workflow and safeguard your projects.
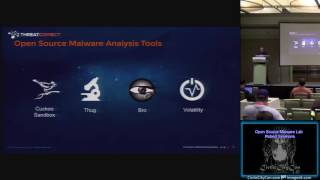
Open Source Malware Lab
Learn to build and use an open-source malware analysis lab with tools like Cuckoo Sandbox, Thug, Bro, and Volatility Framework for effective threat detection and analysis.
Intro to Mobile Device Testing
Learn essential techniques for testing mobile devices, covering key aspects of security assessment and vulnerability identification in mobile applications.
Its Not a Sprint
Explore strategies for sustainable long-term success in information security, emphasizing the importance of pacing and continuous improvement over quick fixes and burnout.