A Developer's Guide to Pentesting
Explore pentesting from a developer's perspective, learning essential techniques and strategies to enhance software security and vulnerability assessment.
Decoding Bug Bounty Programs - Jon Rose
Explore bug bounty programs' benefits, challenges, and impact on cybersecurity. Learn how to participate effectively and understand their role in modern security practices.
So Hopelessly Broken - The Implications of Pervasive Vulnerabilities in SOHO Routers
Explore vulnerabilities in SOHO routers, covering security risks, testing methods, and exploit development. Learn about command injection, directory traversal, and buffer overflows with live demonstrations.
Gitdigger - Creating Useful Wordlists From Public Github Repositories
Explore techniques for generating effective wordlists from public GitHub repositories, enhancing penetration testing and security assessments.
STRC - The Security Training and Research Cloud
Explore cloud-based cybersecurity training and research with STRC, covering defense, networking, data centers, automation, and practical labs for skill development.
Introduction to Hacking with PowerShell
Learn to leverage PowerShell for ethical hacking and penetration testing, exploring its powerful scripting capabilities for security professionals and system administrators.
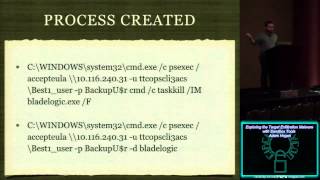
Exploring the Target Exfiltration Malware with Sandbox Tools
Explore target exfiltration malware using sandbox tools. Learn static and dynamic analysis techniques, process management, and considerations for effective malware detection and security automation.
Gitdigger - Creating Useful Wordlists and Hashes from GitHub Repositories
Learn to extract valuable data from GitHub repositories using GitDigger, creating wordlists and hashes for security testing and analysis.
Step On In The Waters Fine - An Introduction to Security Testing Within a Virtualized Environment
Explore virtualized security testing with hands-on guidance, from hardware setup to offensive VMs. Learn essential skills for self-taught hackers and aspiring cybersecurity professionals.
Gone in 60 Minutes - A Practical Approach to Hacking an Enterprise
Practical approach to hacking an enterprise using Yasuo tool. Covers shell generation, exploiting vulnerabilities in Tomcat and Jenkins, and password extraction techniques.
Third Party Code - Fix All the Things
Explore strategies for managing third-party code vulnerabilities and learn effective approaches to mitigate risks in software development and security.
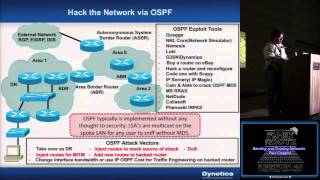
Bending and Twisting Networks
Explore network manipulation techniques for security testing, including bending and twisting methods to identify vulnerabilities and strengthen defenses.
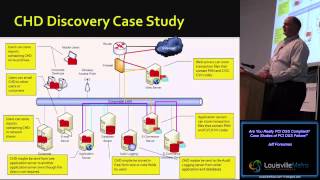
Are You Really PCI DSS Compliant - Case Studies of PCI DSS Failure
Explore PCI DSS compliance challenges, common failure points, and case studies. Learn about cardholder data segmentation, scoping, vulnerability management, and security testing for better implementation.
Exercising with Threat Models
Explore practical threat modeling techniques to enhance cybersecurity strategies and identify potential vulnerabilities in systems and networks.
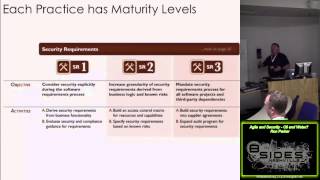
Agile and Security - Oil and Water
Explore the integration of Agile methodologies and security practices, addressing challenges and proposing solutions for effective implementation in software development.
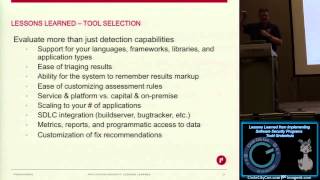
Lessons Learned from Implementing Software Security Programs
Insights on implementing software security programs, covering challenges, training, threat modeling, design reviews, testing, vendor management, and metrics for effective cybersecurity strategies.
Reverse Engineering Windows AFD.sys
Explore Windows AFD.sys reverse engineering techniques, covering static analysis, fuzzing, and Project Zero's goals. Learn about registry inputs, dispatch calls, and bug hunting strategies.
PlagueScanner - An Open Source Multiple AV Scanner Framework
Explore an open-source framework for scanning with multiple antivirus engines, enhancing malware detection capabilities and improving overall security posture.
Building a Sturdy Foundation - A Program-Based Approach to IT Operations and Application Development
Learn to build a robust IT operations foundation using a program-based approach, covering essential management areas like asset, change, configuration, and incident management for improved efficiency and resilience.
Malware Armor
Explore malware analysis techniques, including dynamic and static analysis, anti-virtualization detection, anti-debugging, and obfuscation methods. Learn to use various tools for effective malware armor analysis.
Security Culture in Development
This lecture by Wolfgang Goerlich introduces problem-solving techniques to create secure, reliable, and accessible software, from security cultures to truck factors and exploitable code.