Effective Vulnerability Management for Over 400 Projects at the Eclipse Foundation
Discover how Eclipse Foundation streamlines vulnerability management across 400+ projects, enhancing security practices and reporting processes for researchers and developers.
How AI Impacts Reconnaissance and Bug Bounties in Cybersecurity
Exploring AI's impact on cybersecurity, this interview covers its role in bug bounties, potential risks, job market effects, and defensive strategies against malicious AI use.
Beyond Quick Cash: Rethinking Bug Bounties for Greater Impact
Explore the evolution of bug bounty hunting, focusing on strategic approaches to uncover chainable vulnerabilities and create greater impact in cybersecurity.
Defensive Counting - Quantifying ICS Exposure on the Internet
Explore techniques for accurately quantifying ICS exposure on the Internet, addressing challenges like honeypots and non-critical devices to provide a comprehensive yet measured analysis of real ICS vulnerabilities.
Hitchhikers' Guide to the Vulniverse
Explore key elements of vulnerability disclosure and management, including CVE, CVSS, CWE, and VEX. Gain insights into communication between security teams and researchers.
Secure Logging Practices: Protecting Sensitive Information in Python Applications
Explore secure logging practices to protect sensitive data in Python applications. Learn to identify, redact, and safeguard confidential information from accidental disclosure in log files.
SAP Password Security Vulnerabilities - Dmitry Chastuhin and Alex Polyakov
Explore SAP password vulnerabilities and security risks with experts Dmitry Chastuhin and Alex Polyakov, offering insights into potential threats and protection strategies.
Privilege Escalation from Medium to High Integrity Level in Windows
Unveiling a Windows design flaw allowing privilege escalation from Medium to High integrity level, demonstrating a 100% reliable exploit on the latest Windows versions.
Click and Dagger - Denial and Deception on Android Smartphones
Explore advanced techniques for denial and deception on Android smartphones, focusing on security vulnerabilities and potential exploits in mobile operating systems.
Turbo Intruder: Abusing HTTP Misfeatures to Accelerate Web Application Attacks
Explore advanced HTTP exploitation techniques using Turbo Intruder, a high-speed Burp extension for automated web application attacks, with insights on payload generation and response analysis.
The Tales of a Bug Bounty Hunter - 10 Interesting Vulnerabilities
Explore 10 fascinating vulnerabilities discovered by a bug bounty hunter, offering insights into real-world security flaws and their implications for web application security.
Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Android MRI Interpreter: Taking Pictures of App Code for Vulnerability Analysis
Explore Android app vulnerability detection through a novel OS with MRI-like functionality, enabling non-invasive code analysis and data flow tracing for enhanced mobile security.
Hacking Into iOS's VoLTE Implementation
Unveiling a critical VoLTE vulnerability in iOS devices, exploring its technical details, impact on user privacy, and Apple's response to this long-standing security flaw in 4G implementation.
Allowing an Intel TDX Module to Run Without SEAM - Development Techniques
Explore techniques to run modified Intel TDX modules without SEAM, balancing security and convenience in VM isolation. Learn about environment, methods, and options for development using Intel TDX.
Fuzzing at Mach Speed: Uncovering IPC Vulnerabilities on MacOS
Explore macOS IPC security, focusing on Mach message handlers. Learn about custom fuzzing techniques to uncover vulnerabilities in privileged RPC-like functions, potentially leading to sandbox escapes and privilege escalations.
Bugs Are Shallow - Finding Vulnerabilities in Top GitHub Projects
Explore techniques for identifying vulnerabilities in popular open-source projects on GitHub, enhancing your security research skills and contributing to safer software.
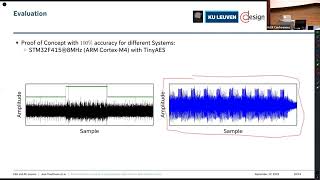
Tools for Side-Channel Analysis and Cryptanalysis
Explore advanced tools and techniques for Side-Channel Analysis (SCA) and cryptanalysis, enhancing your understanding of hardware security and cryptographic vulnerabilities.
Cryptographic Backdooring - Techniques and Implications
Explore cryptographic backdooring techniques and their implications for security systems in this insightful conference talk from SyScan'15 Singapore.
RFIDler: RFID Hacking and Security Analysis Tool
Explore RFID technology and security with Adam Laurie's presentation on RFIDler, covering vulnerabilities, hacking techniques, and practical demonstrations of RFID exploitation.
Analyzing Wi-Fi Wardriving Data with Google Colab
Learn to analyze Wi-Fi wardriving data using Google Colab. Explore captured data, detect access points, and gain insights into wireless device mapping with this hands-on tutorial led by security researcher Alex Lynd.