Finding Multiple Bug Effects for More Precise Exploitability Estimation
Explore advanced techniques for estimating software vulnerabilities and enhancing exploit detection through multi-effect bug analysis and precise exploitability assessment.
100 Bug Bounties and Security Research - Lessons from BSides Tampa 2015
Explore security research, bug bounties, and ethical considerations in cybersecurity with insights from Kevin Johnson's experiences and industry examples.
Building a Security Research Framework - Discussion for Researchers
Explore security research challenges, motivations, and ethical considerations. Learn about legal issues, reproducibility, and resources for independent researchers in this insightful discussion.
Reticle Dropping - An Intelligent F-BOMB
Explore the innovative F-BOMB device for covert network infiltration and data exfiltration, discussing its design, capabilities, and potential applications in cybersecurity.
Everything You Always Wanted to Know About Security Academia
Explore the intersection of cybersecurity and academia, uncovering insights and opportunities for those interested in pursuing academic careers or research in the field of information security.
Grey Hats and Bug Bounties
Explore ethical hacking, bug bounty programs, and the role of grey hat hackers in improving cybersecurity. Learn about responsible disclosure and the benefits of participating in vulnerability research.
SPArring with the Security of Single Page Applications
Explore security challenges in Single Page Applications with insights on automating detection and mitigation strategies for modern web development vulnerabilities.
Normalizing AppSec Issues for Contextual Risk-Based Prioritization at Enterprise Scale
Explore a new approach to Application Security that focuses on critical risks by incorporating contextual intelligence, improving efficiency and delivery in enterprise-scale programs.
Time Lock Puzzles for Good and Evil
Explore timelock puzzles in cybersecurity: their history, offensive and defensive applications, novel constructions, weaponization techniques, detection methods, and challenges in both malicious and benign use cases.
Working with the Security Community - A Decade of Evolution
Veteran security expert reflects on a decade of application security evolution, community interactions, and future trends in vulnerability management and response.
Practical Tips for Running a Successful Bug Bounty Program
Practical tips for running a successful bug bounty program, including scope definition, communication strategies, and vulnerability rating. Insights from experienced professionals on managing crowdsourced security testing effectively.
Simplifying Coordinating Vulnerabilities and Disclosures in Open Source Projects
Learn best practices for handling vulnerability disclosures in open source projects. Discover tools and templates to streamline the process and reduce stress when dealing with security reports from researchers.
Vulnerability Discovery in Unexpected Places - Hack.lu 2017
Explore unexpected security vulnerabilities discovered in everyday scenarios, from web automation to airport security. Learn how seemingly innocuous systems can be exploited for data theft or financial gain.
Perfect Vulnerability Reports and Still Getting Hacked - Limitations of Security Tools
Explore limitations of vulnerability detection tools, challenges in vulnerability management, and strategies for improving application security despite imperfect reporting systems.

Disclosure, Hack and Back - Vulnerability Reporting and Cybersecurity Insights
Explore real-world vulnerability reports and hacking incidents, revealing common mistakes in both corporate security responses and cybercriminal operations. Gain insights into improving cybersecurity practices.
The Future of Hacking: OpenAI's GPT-4 Code Interpreter - Cybersecurity Applications
Explore AI's potential in cybersecurity with GPT-4 Code Interpreter. Learn to simplify complex issues, analyze diverse programming languages, and manage cryptocurrency data for enhanced bug hunting and communication.
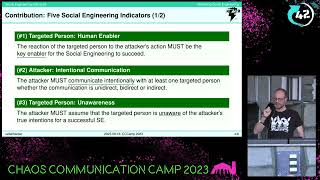
Identifying Social Engineering - Five Key Indicators
Explore five key indicators to identify social engineering in real-world scenarios, literature, and experimental design, enhancing your ability to recognize and mitigate manipulation tactics.
Exploit Hall of Fame - Techniques and Innovations
Renowned security researcher Thomas Dullien explores notable exploits, offering insights into vulnerability analysis and exploitation techniques in this engaging presentation.
Exploit Hall of Fame - Techniques and Innovations
Renowned security researcher Thomas Dullien explores notable exploits in this insightful talk, offering valuable insights for cybersecurity professionals and enthusiasts.
Horror Stories from the Automotive Industry - Security Challenges and Solutions
Unveiling critical security flaws in automotive industry through penetration testing experiences. Explores industry behavior, proposes improvements for safer, more reliable future in vehicle development and cybersecurity.
macOS Red Teaming in 2023 - Zero-Day Edition
Explore cutting-edge macOS red teaming techniques, including 0-day vulnerabilities, presented by a principal security specialist at DefCamp 2023, a major cybersecurity conference.