Exploring Process Capabilities with eBPF - Monitoring and Security in Cloud Native Applications
Explore eBPF's capabilities for scaling, monitoring, and securing cloud-native apps. Learn to run ad hoc experiments using BumbleBee and expose kernel events as Prometheus metrics for enhanced security research.
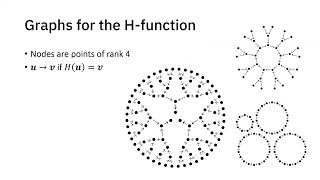
Cryptanalysis of Digital Signatures - Crypto 2023
Explore cutting-edge research on digital signature vulnerabilities and attack methods in this comprehensive cryptography conference session.
Investigating WebSocket Server Security - Beyond HTTP
Investigates WebSocket server security, introducing new tools for endpoint discovery, server fingerprinting, and vulnerability detection. Focuses on implementation-level differences in open-source libraries.
Empowering Security with Generative AI - Fundamentals and Applications of GPT Models
Explore GPT models' potential in security research, covering semantic searching, few-shot learning, and code generation. Gain insights and inspiration for leveraging AI to empower security teams.

The Evolution of Exploiting Memory Vulnerabilities in Linux
Explore the evolution of memory vulnerability exploitation in Linux, covering outdated techniques, binary hardening, and cutting-edge bypass methods, with real-world examples and statistical insights.
Binary Fuzzing With Snapshot-Assisted-Driven Comparison Branch Analysis
Innovative binary fuzzing technique using snapshot-assisted comparison branch analysis to efficiently find vulnerabilities in complex software, overcoming limitations of traditional symbolic execution methods.
A Journey Into Synology NAS
Exploring Synology NAS security: environment setup, device fingerprinting, local services analysis, remote access flow, and vulnerability discoveries from local and remote perspectives.
Fuzzing RDP Client and Server
Exploring innovative techniques to fuzz RDP protocol using WinAFL, uncovering vulnerabilities in both client and server implementations for enhanced remote connection security.
Scaling the Security Researcher to Eliminate OSS Vulnerabilities Once and For All
Explore innovative strategies to scale security research and eradicate vulnerabilities in open-source software, enhancing overall cybersecurity and software reliability.
Blurred Lines - The Mixing of APTs with Crimeware Groups
Exploring the blurred lines between state-sponsored actors, APT groups, and crimeware gangs, challenging traditional classifications and discussing the emergence of second-tier APT categories.
The Next Generation of Virtualization Based Obfuscators
Explore next-gen virtualization obfuscators: design principles, weaknesses, and future challenges. Learn about advanced code protection techniques and their impact on modern software security.
Instrumenting System Applications on Android Images
Instrumenting Android system apps on stock images using Frida for dynamic analysis. Explores various approaches, their limitations, and a successful method for analyzing Google Play Protect Services.
Breath of the RF Field
Explore Amiibo technology, reverse engineering, and NFC protocol vulnerabilities in Nintendo consoles using software-defined radio and a custom simulator for security research.
Static Instrumentation Based on Executable File Formats
Static instrumentation techniques for executable files without modifying code or system environment. Enables architecture-independent injection and hooking without privileged access, suitable for integrity checking and non-rooted environments.
Pulling MikroTik into the Limelight
Explore MikroTik's RouterOS internals, including IPC protocols, message formats, and cryptography. Learn about a new remote jailbreak and gain insights to accelerate RouterOS security research.
Linux Vulnerabilities, Windows Exploits - Escalating Privileges with WSL
Explore WSL vulnerabilities and Windows kernel exploitation techniques. Learn about reverse engineering, syscall manipulation, and bypassing modern anti-exploitation defenses to achieve privilege escalation.
Taking the Guess Out of Glitching
Explore fault injection techniques in hardware hacking with practical tips on timing, intensity, and effectiveness. Learn innovative methods to determine optimal glitch timing for successful attacks.
Automatic Automotive Hacking
Explore automotive security vulnerabilities and hacking techniques with Craig Smith, founder of Open Garages and author of the Car Hacker's Handbook, in this insightful presentation.
Hypervisors in Your Toolbox - Monitoring and Controlling System Events with HyperPlatform
Explore HyperPlatform, a thin hypervisor for Windows, enabling flexible handling of system events and rapid implementation of hypervisor-based tools with high compatibility and efficiency using Intel VT-x technology.
The Unbearable Lightness of BMCs
Explora vulnerabilidades críticas en dispositivos de gestión remota de centros de datos, revelando riesgos de ejecución de código y movimiento lateral entre servidores y BMCs.
Finding and Exploiting Vulnerabilities in Mobile Point of Sales Systems
Exploración de vulnerabilidades en sistemas de pago móvil: demostraciones en vivo de ataques MitM, modificación de valores y explotación de firmware en dispositivos mPOS de principales proveedores.