Sentinel Policy-as-Code: Implementing Security and Compliance Guardrails in Financial Services
Discover how Fannie Mae implements 400+ security and compliance guardrails using Sentinel policies for infrastructure automation in regulated financial environments.
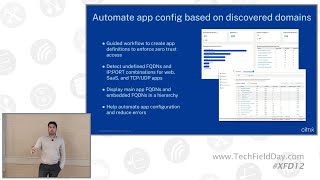
Citrix Secure Private Access - Zero Trust Network Administration Demo
Discover how to implement zero trust access through Citrix Secure Private Access, from initial setup to policy configuration and troubleshooting for IT administrators.
Taype: A Policy-Agnostic Language for Oblivious Computation
Explore Taype, a novel language for secure multiparty computation that decouples security policies from program logic. Learn about oblivious algebraic data types and tape semantics for flexible, policy-agnostic development.
Reinventing Compliance with Platform Engineering
Discover how to align platform engineering with compliance standards, creating secure and compliant Internal Developer Platforms without sacrificing team autonomy or developer productivity.
Unlocking Security Policies and Guardrails - The Bridge Between Dev, Sec and Ops in Kubernetes Deployments
Explore security policies and guardrails in Kubernetes deployments, bridging the gap between development, security, and operations teams for enhanced collaboration and protection.
Simplifying IaC Security
Explore open-source tools for securing IaC pipelines, learn management techniques, and discover a new tool for simplified deployment. Gain insights on implementing security scans without disrupting existing workflows.
Securing Cloud Native Resources with Open Policy Agent
Explore Open Policy Agent for securing cloud-native resources, covering fundamentals, integration with Kubernetes, and strategies for enforcing security policies in dynamic environments.
Integrity Policy Enforcement - Full System Integrity Verification
Explore comprehensive system integrity verification techniques and policy enforcement strategies for enhanced security in modern computing environments.
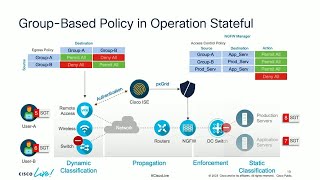
Common Enterprise Security Policy - Simplifying Network Security Automation
Discover how to unify enterprise security policies across platforms using Cisco's Security Group Tagging, enabling seamless hybrid cloud management and simplified network automation for better security control.
The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.
Руководство по выращиванию политик безопасной разработки
Discover effective strategies for implementing secure development policies while maintaining developer productivity and organizational harmony, with practical guidance on incident prevention.
Zero Trust Security Fundamentals for Storage Developers
Discover the essential principles of Zero Trust security methodology and its critical role in storage development, focusing on dynamic enforcement and comprehensive network protection.
Shield Your Backend from Outside Attacks with API Managers
Discover how to protect backend systems using API Managers, implement security layers, and defend against vulnerabilities while centralizing security configurations for robust API protection.

OPA - Extended Kubernetes Controller for Cloud-Native Security Policies
Explore creating security policies for Kubernetes using OPA, a unified framework for policy across the cloud-native stack.

Kontena Lens: Kubernetes IDE for Managing Multiple Clusters
Explore Kontena Lens, a powerful desktop app for managing multiple Kubernetes clusters, enhancing developer understanding and streamlining cluster operations.
Defining Security Baselines and Guardrails with Access and Organization Policies
Learn to build effective security guardrails using access and organization policies for cloud environments, featuring insights from Box and best practices for managing security access policies.
CEL-Ebrating Simplicity: Mastering Kubernetes Policy Enforcement
Master Kubernetes policy enforcement using Common Expression Language (CEL), from basic integration to advanced security implementations. Learn practical applications through live demos and CEL Playground testing.
Elevate Your Kubernetes Policy Game with Kyverno - Policy as Code Lifecycle Management
Master Kubernetes policy management with Kyverno through real-world insights from Robinhood's migration journey, covering validation, enforcement, lifecycle management, and performance optimization for large-scale deployments.
Scanning Infrastructure as Code for Security Vulnerabilities with Terraform
Master infrastructure security scanning with Checkov OSS, focusing on Terraform vulnerabilities and exploring policy-as-code solutions like Bridgecrew and Hashicorp Sentinel for enhanced cloud security.
Artifact Hub - Discover, Analyze, and Share Cloud Native Artifacts
Discover how to effectively find, analyze, and share cloud native artifacts using Artifact Hub, exploring its features for managing over 20 different artifact types and improving project discoverability.
Understanding Zero Trust Architecture - Principles and Implementation
Explore the transformative principles of Zero Trust security, from "never trust, always verify" mindset to practical implementation strategies for enhanced network protection.