Aus Sicherheitsgründen muss das Grundgesetz leider abgeschafft werden - Schluss mit
Kritische Analyse der Gleichsetzung von Sicherheit und Repression, die Grundrechte gefährdet. Plädoyer für echte Sicherheitsmaßnahmen und Freiheitsschutz statt Überwachung und Angstmacherei in Politik und Wirtschaft.
Practical Physical Security Advice for the Modern Enterprise
Practical advice on improving physical security, covering common weaknesses, bypass techniques, vulnerability mapping, and cost-effective solutions for modern enterprises.
Open Source Security Tools for Kubernetes Applications
Explore open-source tools for securing Kubernetes applications, covering image scanning, runtime security, and anomaly detection. Learn practical strategies for maintaining a secure cloud-native environment.
Dynamic Management of Docker Containers in Multi-Cloud and Edge Using MiCADO
Explore MiCADO: an open-source framework for dynamic management of Docker containers across multi-cloud and edge environments, built on Kubernetes. Learn about its components, policies, and applications in various scenarios.
Running KubeVirt Workloads with No Additional Privileges
Explore running VMs on Kubernetes without root privileges using KubeVirt. Learn about security practices, SELinux integration, and the journey to achieve rootless VM execution.

Dynamic Authorization and Policy Control for Docker Container Environments
Explore fine-grained policy enforcement in Docker container environments using Open Policy Agent. Learn to balance security requirements with rapid application deployment and developer productivity.
So You’re the First Security Hire - Creating a Security Program and Integrating Security into Your Company’s Culture
Guidance for pioneering security professionals on establishing a robust security program, integrating it into company culture, and balancing protection with business needs.
Into the Mind of an IoT Hacker - How to Protect IoT Networks & Devices
Explore IoT hacking techniques and learn effective strategies to secure networks and devices against cyber threats, vulnerabilities, and attacks in various organizational settings.
Pen-Testing the Supply Chain
Explore software supply chain risks through enhanced security testing and adversary simulation. Learn to identify vulnerabilities, assess vendor risks, and implement effective security measures.
What Is a Security Analyst and What Job Role Will They Perform
Explore the role of a security analyst, their responsibilities, and key cybersecurity concepts. Learn about attack chains, compliance, and the security investigation process.
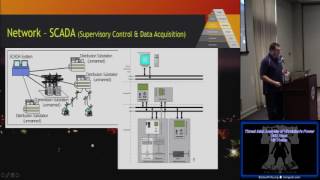
Threat Intel Analysis of Ukrainians Power Grid Hack
Analyze the Ukrainian power grid hack, exploring tools, techniques, and implications. Learn about ICS vulnerabilities, attack stages, and strategies to enhance critical infrastructure security.

Building Secure Systems in Haskell
Explore building secure web applications using Haskell's LIO and Hails framework, focusing on data privacy protection through language-level information flow control and declarative policy specification.
STORM - Refinement Types for Secure Web Applications
STORM: A web framework for building MVC applications with compile-time enforcement of security policies, reducing trusted code to under 1% and providing static security enforcement with minimal overhead.
Micro-Policies - Formally Verified, Tag-Based Security Monitors
Explore formally verified tag-based security monitors for low-level policies. Learn about dynamic sealing, compartmentalization, control-flow integrity, and memory safety implementation.
Deploying & Securing Microsoft Internet Security & Acceleration Server
Comprehensive guide on deploying and securing Microsoft ISA Server, covering advanced techniques for network protection and optimal performance in enterprise environments.
Securing Danish Healthcare Using Cloud Native
Explore cloud-native security practices for healthcare, covering provider security, Kubernetes infrastructure, cluster management, runtime security, and container protection through demos and real-world examples.
Security Control Wins - Fails
Explore common security control successes and failures, focusing on network access, segmentation, antivirus, awareness training, and privileged account management.
Why I Quit My Dream Job at Citi - A Data Centric Approach to Key Management
Explore key management challenges in large organizations, data protection strategies, and the need for human-readable, machine-enforceable policies in this insightful talk by a former Citi executive.
HIPAA for Infosec Professionals
Comprehensive overview of HIPAA regulations for information security professionals, covering key concepts, compliance requirements, and best practices in healthcare data protection.
Network Isolation and Security Policies for Kubernetes Bare-metal Nodes
Explore network isolation and security policies for Kubernetes bare-metal nodes using SDN, OVN, and OVS, with Smart NIC offloading for efficient multi-tenant cloud environments.
Protecting Pentests - Recommendations for Performing More Secure Tests
Comprehensive recommendations for building secure penetration testing operations, including technical aspects, policies, procedures, and client communication strategies.