
Automating Configuration and Permissions Testing for GitOps with OPA Conftest
Learn how The New York Times automates configuration and permissions testing for GitOps using OPA Conftest, enabling secure self-service deployments while maintaining developer autonomy.
Kubernetes SIG Auth Deep Dive
Explore Kubernetes authentication, authorization, and security features with experts from Google, Microsoft, and Red Hat. Learn about ongoing projects and opportunities for involvement in SIG Auth.
Creating Security Policies and Controls for Kubernetes Using ChatGPT
Explore how to leverage ChatGPT for creating robust security policies and controls in Kubernetes environments, enhancing your cloud-native security practices.
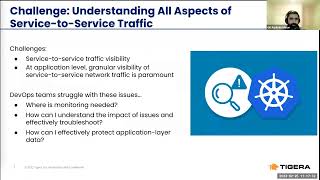
Container and Kubernetes Security Policy Design - 10 Critical Best Practices
Explore 10 crucial best practices for designing robust security policies in container and Kubernetes environments, enhancing protection and mitigating risks.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
BPF LSM - Updates and Future Developments
Explore BPF LSM's latest updates, real-world applications, and future developments. Learn about new features, case studies, and challenges in building advanced security policies.
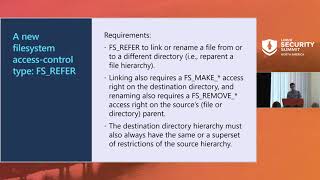
Landlock Update: File Reparenting and Network Rules Support
Explore Landlock's latest updates: file reparenting improvements and new network access controls for enhanced app and container security in Linux systems.
Dev-Driven Automated Deployments Like a Cloud Native Pro - Even for Beginners
Discover automated Kubernetes deployments for developers and platform teams. Learn to streamline workflows, enhance security, and boost productivity using GitOps and open-source tools.
Secure Container Deployments - Time for Refresh
Explore modern container security practices, focusing on pod security, policy implementation, and admission controllers for enhanced protection in Kubernetes environments.
SELint - An SELinux Policy Static Analysis Tool
Explore SELint, a static analysis tool for SELinux policies, addressing challenges and improving security through practical examples and insights.
Secure the Linux Kernel with eBPF Linux Security Module
Explore eBPF Linux Security Module for implementing granular security policies in the Linux kernel without configuration or kernel modules. Learn to leverage BPF LSM hooks for MAC and DAC policies.
Making Remote Attestation Useful on Linux
Explore TPM remote attestation on Linux, its current limitations, and potential improvements for enhanced security and trust in boot processes.
Cybersecurity Certification for IoT Software - Pros and Cons
Experts debate the pros and cons of a CyberUL certification for IoT devices, discussing its potential impact on security, innovation, and industry standards in the rapidly expanding digital infrastructure.
Deep Dive into Landlock Internals
Explore Landlock's security sandboxing features, internals, and roadmap. Learn about access control, ruleset creation, and policy composition for enhanced system protection.
Beyond Labels: Evolving Data Classification
Explore advanced data classification strategies balancing security, privacy, and business needs. Learn to create flexible programs that meet departmental demands while ensuring compliance and protection.
The Right Feature at the Right Place - Authorization Example
Explore moving authorization from code to a readable, accessible place using Open Policy Agent and Apache APISIX API Gateway for improved system auditability.
Update on Landlock: IOCTL Support
Explore Landlock security module's features, recent developments, and new IOCTL restriction support for enhanced Linux process sandboxing and security policies.
Security-as-Code to Accelerate DevSecOps - A Practical Guide to Get Started
Practical guide for implementing security-as-code in DevSecOps, covering automation of security policies, common barriers, and six steps to get started with this approach.
Using Automation to Help Achieve Security in a Multicloud Environment
Explore strategies for automating security in multicloud environments, focusing on critical components, tools, and data utilization to enhance operational security and inform decision-makers.
Network Security for Apps on OpenShift
Explore network security strategies for OpenShift apps, covering secure tiers, external connections, and ingress protection. Learn practical solutions for enterprise-level container platform security.
Digital Safety for Politically Vulnerable Organizations
Learn strategies for protecting politically vulnerable organizations from digital threats, covering physical and psychological security, incident response, and data retention policies.