Fortify Your Code: Secure Your Supply Chain with Scorecard
Discover how to assess and strengthen open-source software security using Scorecard, gaining practical insights into dependency risk management and implementing robust supply chain protection measures.
Physical Security Assessment: Doors, Cameras, and Mantraps - A Practical Guide
Discover practical approaches to physical security assessments, from door systems to mantraps, while learning effective client communication techniques for security consulting.
Check Your Google Cloud Security Posture
Discover methods to assess and enhance your Cloud Security posture, avoiding common pitfalls and leveraging new features for a more secure environment.
Scorecard at Scale: Old and New Possibilities for Lifting Security on All Repositories
Discover strategies for implementing OpenSSF Scorecard at scale, exploring various tools and methods to assess, monitor, and enhance repository security across large organizations.
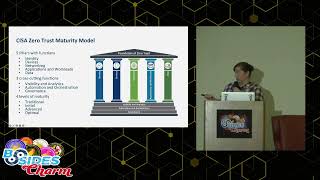
Measuring Your Zero Trust Maturity Using the CISA Framework
Discover how to assess and enhance zero trust architecture using CISA's Maturity Model, with practical insights from Centers for Medicare and Medicaid Services' implementation framework and tracking methods.
Ten Ways to Frustrate Attackers in Network Security
Discover practical network security strategies and tools from a pentester's perspective to strengthen defenses and make attackers' work significantly more challenging and time-consuming.
Everything You Didn't Want to Know About CVE - Understanding Vulnerability Disclosure Challenges
Dive into the complexities of vulnerability disclosure and CVE processes, exploring recent events that highlight systemic issues and their impact on security professionals' ability to manage threats effectively.
Open Source Intelligence Gathering for Security Testing - Recon 101
Master essential OSINT techniques and reconnaissance tools to efficiently gather critical intelligence about organizational infrastructure and potential security vulnerabilities without active network engagement.
Leave Home Safe App Security Assessment - The Good, the Bad, the Ugly
Explore security vulnerabilities in Hong Kong's LeaveHomeSafe app, from assessment techniques to disclosure challenges. Gain insights on securing contact tracing apps and improving data privacy.
Building and Leading Advanced Red Teams
Discover advanced strategies and methodologies for building, managing, and leading effective red teams in cybersecurity operations and penetration testing environments.
Open Source Security Is Not a Spectator Sport
Discover how CNCF leads open source security innovation through TAG Security initiatives, supply chain recommendations, and community-driven solutions for cloud-native environments.
Reviewing NuGet Packages Security Using OpenSSF Scorecard
Discover how to assess NuGet package security using OpenSSF Scorecard, focusing on maintenance quality, workflow safety, and security tools implementation for better application security.
PentestGPT: Evaluating and Harnessing Large Language Models for Automated Penetration Testing
Explore how PentestGPT leverages LLMs to automate penetration testing, addressing challenges in context maintenance and demonstrating significant improvements in task completion for security testing.
Hacker Numerology - Understanding System Security Through Number Analysis
Explore the fascinating relationship between numbers and system security, learning to deduce security properties through identifier pattern analysis and observation.
Modern AppSec vs. GenAI Applications - Is Your Security Program Ready?
Explore how traditional AppSec programs measure up against emerging GenAI security challenges, evaluating threat mitigation strategies and necessary program adaptations for AI-assisted development.