Scaling Security through Context-Based Security Assessments
Streamlining security assessments through context-based automation, enabling efficient scaling and tailored workflows for product security teams in rapidly growing organizations.
OWASP Software Assurance Maturity Model - SAMM
Explore OWASP's Software Assurance Maturity Model (SAMM), a framework for improving software security practices across organizations, presented by expert Bart De Win.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
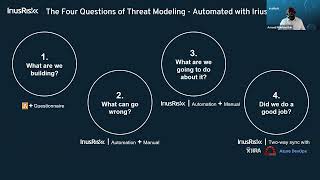
Using IAC to Accelerate Threat Modeling
Explore innovative techniques for accelerating threat modeling using Infrastructure as Code (IAC), enhancing security practices in software development and deployment.
Docker for Pentesters
Learn essential Docker techniques for penetration testing, enhancing your cybersecurity skills and improving your ability to identify vulnerabilities in containerized environments.
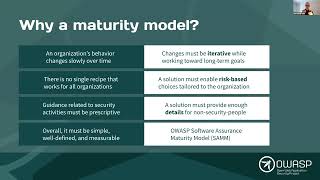
OWASP SAMM Project - Introduction to Software Assurance Maturity Model
Explore the OWASP SAMM framework for software assurance, learning key strategies to integrate security practices throughout the software development lifecycle.
OWASP DSOMM Project - Introduction to DevSecOps Maturity Model
Explore the OWASP DSOMM Project, a framework for enhancing software security practices and measuring DevSecOps maturity in organizations.
AppSec Awareness - A Blueprint for Security Culture Change
Discover strategies for building a sustainable security culture through AppSec awareness, focusing on human factors, knowledge sharing, and effective program architecture.
reNgine - An Automated Reconnaissance Framework
Explore an automated reconnaissance framework for efficient cybersecurity assessments, enhancing vulnerability detection and streamlining security workflows.
Implementing OpenSSF Best Practices Badges and Scorecards for Project Security
Learn to enhance open-source project security using OpenSSF Best Practices Badges and Scorecards. Gain practical tips for implementation and addressing common issues to improve your project's security posture.
Breaking ML Services: Finding Zero-Days in Azure Machine Learning
Uncover critical vulnerabilities in Azure Machine Learning, including credential leaks, information disclosure, and persistence techniques. Learn assessment methods for cloud-based MLaaS platforms and shared responsibility models.
How to Break, Then Fix, Differential Privacy on Finite Computers
Exploring vulnerabilities in differential privacy implementations, focusing on precision-based attacks and proposing solutions to address floating-point behavior issues in open-source libraries.
Passive Reconnaissance Techniques for Ethical Hacking - Webinar 3
Explore passive reconnaissance techniques for ethical hacking and cybersecurity, focusing on gathering information without direct interaction with target systems.
Why Security Fails and How to Solve It - Lessons from Real-World Assessments
Explore real-world security failures and innovative solutions with insights from Praetorian's field experiences. Learn actionable steps to enhance cybersecurity through smarter practices and cutting-edge tools.
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
Reviewing NuGet Packages Security Using OpenSSF Scorecard
Explore OpenSSF Scorecard for assessing NuGet package security. Learn to evaluate maintenance, workflows, and security tools to improve application safety and make informed decisions.
Unlocking Startup Success: The Vitality of Security Assessments and How to Master Them
Discover essential security assessment strategies for startups. Learn to establish robust security controls, navigate audits, and build a strong security posture to protect innovative ideas and ensure market success.
How to Use WPScan - A Walkthrough with the Author
Comprehensive walkthrough on using WPScan for WordPress security assessment, featuring insights from the tool's creator ethicalhack3r during a Live Recon episode.
Security TAG Closing - Highlights and Future Work
Wrap-up of Cloud Native Security Con, highlighting Security TAG's work, future plans, and ways to get involved. Covers whitepapers, assessments, audits, and ecosystem insights.
Assessing Environments Against Cloud Native Security Best Practices
Insights on assessing cloud native environments against security best practices, including CNCF white papers and NIST controls. Explores open-source automation for efficient audits and cross-mapping frameworks.
Using the O2 Platform to Automate Application Security Knowledge and Workflows
Explore the O2 platform for automating web application security reviews, enhancing visibility, and streamlining security workflows for both experts and non-experts.