You're Going to Need a Bigger Shovel - A Critical Look at Software Security Assurance
Explore software security assurance strategies, from assessment to implementation, and learn how to adapt to evolving threats and disruptive technologies in this comprehensive overview.

Dirty Red Team Tricks
Explore devious tactics and advanced techniques for penetration testing and red team operations, enhancing your cybersecurity skills and strategies.
Installing Nessus on Kali Linux and Doing a Credentialed Scan
Learn to install Nessus on Kali Linux and perform credentialed scans for comprehensive vulnerability assessments, enhancing your cybersecurity skills and network protection capabilities.
Seeing Purple - Hybrid Security Teams for the Enterprise
Explore hybrid security teams for enterprise, combining blue and purple team strategies for proactive protection, threat modeling, and effective exercises.
Web App Hacking and So Can You
Learn web application hacking techniques and methodologies to identify vulnerabilities and improve security posture. Gain practical skills for ethical hacking and penetration testing.
Gray Hat PowerShell
Explore advanced PowerShell techniques for ethical hacking and security testing, focusing on leveraging built-in Windows tools for penetration testing and system analysis.
Pentesting with Docker
Learn to leverage Docker for efficient and scalable penetration testing. Explore containerization techniques to enhance your security assessment toolkit and streamline your workflow.
Submersion Therapy - Security Frameworks - What Was Once Old Is New Again
Explore 10 security frameworks, their evolution, benefits, and challenges. Learn to choose the right framework, assess security, set priorities, and measure results for effective information security management.
Cross Industry Collaboration
Explore cross-industry collaboration in cybersecurity, covering research, talent acquisition, public boards, assessments, and risk transfer with insights from Helen Patton.
Metasploit Townhall
Explore Metasploit's latest developments and future plans with key team members in this informative townhall discussion from DerbyCon 2016.
Red Team Yourself - Thomas Richards
Learn adversary emulation techniques, build an in-house red team, and master reconnaissance and attack planning for comprehensive security assessments.
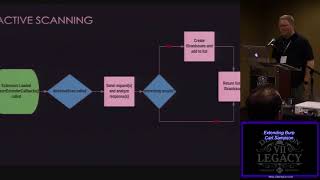
Extending Burp
Explore techniques for enhancing Burp Suite's functionality through extensions, improving web application security testing capabilities and efficiency.
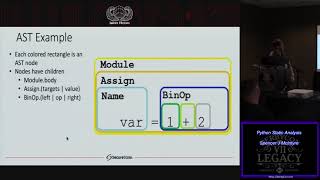
Python Static Analysis
Explore Python static analysis techniques for security assessments, focusing on AST modules, Bandit tool, and practical demonstrations.
Common Assessment Mistakes Pen Testers and Clients Should Avoid
Explore common pitfalls in penetration testing and client assessments, learning strategies to enhance security evaluations and avoid critical mistakes.
SDR RF Hacking Primer
Comprehensive primer on SDR and RF hacking techniques, covering essential concepts and practical applications for security professionals and enthusiasts.
Wacky and Wild Security - Getting Things Under CIS Controls V7
Explore CIS Controls V7 implementation strategies, from history to practical application, including matrix creation, heat mapping, and assessment techniques.
Metasploit Town Hall 0x4
Explore Metasploit updates, community support, and new features with the development team. Learn about evasion modules, external tool integration, and contributing to the project.
Battling Magecart - The Risks of Third Party Scripts
Explore the risks of third-party scripts and learn strategies to combat Magecart attacks, enhancing your website's security and protecting user data.
BloodHound - From Red to Blue
Explore BloodHound's versatility in both offensive and defensive cybersecurity, enhancing your ability to identify and mitigate potential vulnerabilities in network environments.
Common Observations from a Security Assessor
Insights from a security assessor on common vulnerabilities, cloud security best practices, and strategies to enhance organizational cybersecurity posture.
Combining the Power of Builders and Breakers in Cybersecurity - USENIX Enigma 2018
Exploring the evolving relationship between companies and security researchers in bug bounty programs, examining challenges, benefits, and future implications for cybersecurity.