
Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
Kernel Mode Threats and Practical Defenses
Explore advanced kernel mode threats, Microsoft's defenses, and practical strategies for detecting and mitigating sophisticated attacks on Windows operating systems.
Behind the Scenes of iOS and Mac Security
Explore iOS and macOS security features, including Find My, Gatekeeper, and kernel integrity protection. Learn about Apple's innovative approaches to user privacy and device security.
The One Weird Trick SecureROM Hates - Vol. 2
Exploring checkm8 vulnerability in iOS SecureROM, its exploitation for jailbreaking, and updates on pongoOS development. Insights into cross-platform challenges and future plans for iOS security research.
I Boot when U-Boot
Explore a custom bootkit for U-Boot devices, its persistence techniques, and implications for IoT security. Learn about backdooring methods and potential countermeasures.
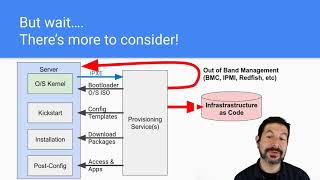
Give Your PXE Wings - Bootstrapping Explained
Demystifying system bootstrapping: explore PXE, multi-stage processes, and automation techniques for faster, simpler, and more reliable IT provisioning and day-two operations.
Fault Injection Attacks on Secure Boot
Exploring fault injection attacks on secure boot, this talk introduces techniques, impacts, and practical mitigation strategies for embedded systems security, with real-world examples and key takeaways.
TOCTOU Attacks Against Secure Boot and BootGuard
Explore TOCTOU attacks on Intel's BootGuard, learn about vulnerabilities in secure boot processes, and discover open-source tools for testing system security.
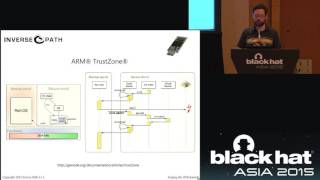
Forging the USB Armory
Explore the development of an open-source USB-sized computer for security applications, featuring advanced SoC technology, secure boot, and ARM TrustZone implementation.
Linux Secure Boot
Erfahrungen und Konzepte zur Implementierung von Secure Boot auf Linux-Systemen, um Schadsoftware und manipulierte Betriebssysteme zu verhindern.
Rethink, Repurpose, Reuse - Rain Hell
Explore innovative ways to repurpose and reuse technology, focusing on Android devices and Linux installations on various platforms. Learn about security implications and future possibilities.
Bypassing Secure Boot Using Fault Injection
Explore fault injection techniques to bypass Secure Boot in embedded systems, focusing on hardware-based attacks when logical vulnerabilities are absent.
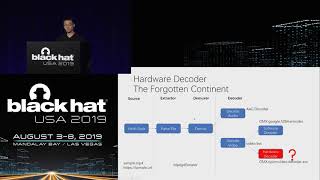
Bypassing the Maginot Line - Remotely Exploit the Hardware Decoder on Smartphone
Explore vulnerabilities in Qualcomm's Venus hardware decoder, learn its architecture, and discover remote exploitation techniques for smartphone security research.

Secure Boot Under Attack - Simulation to Enhance Fault Attacks & Defenses
Explore fault injection attacks on Secure Boot, their impact on embedded systems, and strategies for enhancing defenses through simulation techniques.
Breaking Samsung's Root of Trust - Exploiting Samsung S10 Secure Boot
Exploración de vulnerabilidades en el arranque seguro de Samsung S10, analizando el manejo de solicitudes USB en S-Boot y sus implicaciones para la seguridad del dispositivo.
Forging the USB Armory
Explore the development of the USB armory, an open-source hardware device for security applications. Learn about its architecture, security features, and potential uses as a trusted USB device.

Securing Firmware - Secure and Trusted Boot in OpenBMC
Explore secure and trusted boot in OpenBMC, covering hardware root of trust, TPMs, keys, and signing while preserving user freedom to replace firmware securely.

Becoming a Tyrant - Implementing Secure Boot in Embedded Devices
Explore secure boot implementation in embedded devices, covering mechanisms, reasons, experiences, and considerations. Learn about chain of trust, adversaries, and implications for device modification and security.
What Does It Mean to Trust Your Boot Process
Explore boot processes, secure boot, and trust establishment in x86 and ARM architectures. Learn about firmware, TPM, and measured boot to enhance device security from startup.
If You Can't Open It, You Don't Own It
Exploring hardware vulnerabilities and their impact on C++ systems, this talk delves into side-channel attacks, physical penetrations, and supply chain risks, offering insights for securing modern C++ designs.
Hardening the Kernel for Secure Boot
Explore kernel hardening techniques for Secure Boot, focusing on preventing privileged code execution and securing kernel entry points to maintain a trusted boot process.