Application Security Training Impact on Developer Code Vulnerability
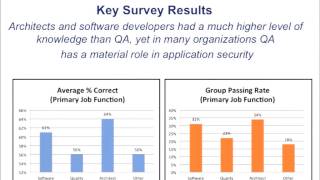
Explores the effectiveness of application security training for developers through a yearlong survey, revealing surprising insights for risk managers and security strategies.
Mantra OS - Penetration Testing Tools and Methodologies
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and controlled environment testing techniques.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.
Application Security - Challenging Traditional Approaches and Controls
Challenging traditional application security approaches, this talk explores innovative strategies for developing and testing secure software, emphasizing the need for consistency and proactive security measures.
Aim-Ready-Fire: Software Assurance and Cybersecurity Panel Discussion
Panel discussion on software assurance trends, challenges, and best practices in cybersecurity. Industry experts share insights on application security, threat intelligence, and risk management strategies for organizations.
Thinking Differently About Security - What Could Possibly Go Wrong?
Explore innovative security perspectives, blending technical expertise with insights from economics and military history to effectively communicate and address cybersecurity challenges.
OWASP A9: Using Components with Known Vulnerabilities - A Year Later
Explore real-world case studies and industry trends on managing component vulnerabilities in applications, with insights on best practices and challenges in following OWASP A9 guidelines.
11,000 Voices - Experts Shed Light on 4-Year Open Source and AppSec Survey
Experts discuss findings from a 4-year study on open source security practices, revealing surprising trends in policy enforcement, vulnerability tracking, and organizational preparedness for security threats like Heartbleed.
Lean Security for Small or Medium-Sized Businesses
Introduces a framework for SMBs to focus security efforts, discussing prevention, limitation, detection, and response capabilities. Provides cost-effective techniques to transform security into a business enabler.
BSIMM: A Decade of Software Security Evolution - Keynote
Explore the evolution of software security over a decade, from early concepts to modern practices, highlighting the BSIMM framework for measuring and improving security initiatives in software development.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
The Cavalry Is Us - Cybersecurity Activism in the Internet of Things Era
Exploring cybersecurity challenges in IoT and the need for collective action. Calls for researchers and professionals to shape the future of digital security and address emerging threats.
Intelligence-Led Cybersecurity - Balancing Global Operations, Risk, and Speed
Experts discuss global cybersecurity challenges, balancing risk and speed in intelligence-led operations, and the interplay between public and private sectors in addressing cyber threats.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
Seeing Around Corners - The Intelligence Professional's Challenge
Intelligence experts discuss strategies for anticipating and addressing unforeseen threats and challenges in national security, offering insights on navigating uncertainty in a complex global landscape.
Open Source in Safety Critical Applications
Explore the role of open source software in safety-critical systems with insights from Kate Stewart of The Linux Foundation.
How to Secure Your App With AppSweep
Learn to scan and secure your app against vulnerabilities using AppSweep, a powerful tool for identifying and addressing security issues in mobile applications.
Revisiting Total Cost of Ownership for External Dependencies
Explore unaccounted risks of external dependencies in software development with Paul Vixie. Learn strategies to mitigate vulnerabilities and improve security practices in IoT and beyond.
Understanding the Impact of Critical Vulnerabilities in Critical Infrastructure: A Detective Story
Explore strategies for assessing and mitigating critical infrastructure vulnerabilities, focusing on novel threats and their potential ecosystem-wide impacts across various sectors.