(In)Security is Eating the World - Speed and Autonomy for Defense
Explore the future of cybersecurity with Michael Coates as he discusses the need for automation, scale, and speed in addressing critical security failures in our technology-driven world.
Building a Security Culture - Digital Transformation and Breach Prevention
Explore strategies for creating a robust security culture amid digital transformation, addressing cloud risks, BYOD challenges, and persistent breaches despite technological investments.
Hard to Port - A Snapshot of the Vulnerability Landscape in 2015
Explore the 2015 vulnerability landscape through anonymized data, discussing trends, challenges, and the shift towards continuous application security and risk management.
Software Security Metrics - Developing Key Indicators for Executives
Techniques for effective communication with executives about software security, focusing on developing meaningful metrics to demonstrate progress and maturity in security capabilities.

Integrating Mobile Devices into Penetration Testing Programs
Explore techniques for assessing mobile device security risks in enterprise environments, including phishing, undermining controls, and using compromised devices as pivot points.
Attack Tree Vignettes for Containers as a Service Applications - Risk-Centric Threat Modeling
Explore attack tree vignettes and risk-centric threat models for Containers as a Service applications, focusing on security challenges in cloud adoption and containerization.
Taking AppSec to 11: Pipelines, DevOps and Making Things Better
Scaling AppSec through DevOps: Learn strategies to enhance application security programs using pipelines, automation, and iterative improvements for large-scale organizations.
50 Shades of AppSec - Lessons from Diverse Application Security Scenarios
Explore the diverse landscape of application security, from sophisticated to absurd, and learn valuable lessons for future security efforts in this engaging keynote by Troy Hunt.
Why Secure Development Programs Are Essential for Application Security
Explore integrating application security into development processes, focusing on proactive measures, resource allocation, and adapting to Agile and DevOps methodologies for effective risk management.
OWASP CISO Survey Report: Tactical Insights for Managers
Gain tactical insights for managers from OWASP's CISO Survey Report, covering threat sources, risks, trends, investments, challenges, and strategies for effective application security management.
Internet Banking Safeguards Vulnerabilities - AppSecEU 2016
Explore internet banking vulnerabilities, attack patterns, and safeguards. Learn about transaction authorization best practices, user authentication, and regulatory requirements for secure online banking.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Practical Tips for Running a Successful Bug Bounty Program
Practical tips for running a successful bug bounty program, including scope definition, communication strategies, and vulnerability rating. Insights from experienced professionals on managing crowdsourced security testing effectively.
Best Practices for Structuring Effective Bug Bounty Programs
Explore best practices for structuring effective bug bounty programs, addressing concerns like security, privacy, and legal issues while maximizing vulnerability identification.
Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.
Using JIRA to Manage Risks and Security Champions Activities
Learn how to effectively manage risks and security champion activities using JIRA, enhancing your organization's application security practices and workflows.
Practical Threat Modeling with Microsoft's Threat Modeling Tool 2016
Learn practical threat modeling using Microsoft's Threat Modeling Tool 2016. Explore data flow-based techniques, risk assessment, and countermeasures for effective application security.
Maliciously Monetizing AppSec Features - It's All About the Money
Explore malicious monetization of AppSec features with Or Katz and Ezra Caltum. Learn about potential security vulnerabilities and their financial implications in application development.
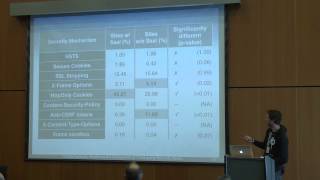
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
OpenSAMM Best Practices - Lessons from the Trenches
Experts share insights on implementing OpenSAMM framework for software security, covering optimal maturity levels, integration with agile development, supplier management, and metrics for secure development lifecycle.
OWASP CISO Survey Report 2013 - Tactical Insights for Application Security Managers
Insights from OWASP-CISO Survey 2013: Application security risks, best practices, and management strategies for CISOs. Covers threat sources, investment plans, and security frameworks.