Measure and Improve Software Supply Chain Assurance with OWASP SCVS
Learn to assess and enhance software supply chain security using OWASP's Software Component Verification Standard (SCVS), improving overall cybersecurity posture.
Under Assault: Assessing Top Threats to US National Security
Former CIA and National Intelligence directors discuss current external and internal threats to US national security, offering expert insights on pressing global challenges.
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.
Homeland Insecurity - Assessing Global Dangers in the Modern World
Explore global security challenges, from terrorism to health crises, and their impact on politics. Experts discuss real threats, perceptions, and strategies for navigating an uncertain world.
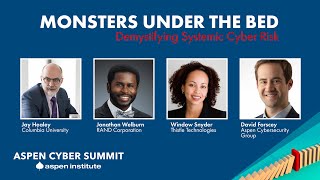
Demystifying Systemic Cyber Risk
Explore systemic cyber risks, their growing complexity, and strategies for management with experts from Columbia, RAND, and Thistle Technologies in this insightful panel discussion.
Can We Put the Pandemic Behind Us? - Assessing COVID-19's Current Impact
Experts discuss the current state of COVID-19, examining falling rates of severe disease and death, while considering ongoing threats and the challenge of balancing public health measures with societal fatigue.
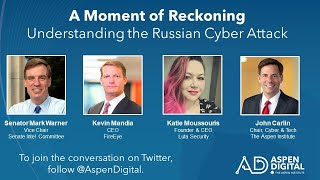
A Moment of Reckoning - Understanding the Russian Cyber Attack
Explore the severe 2020 Russian cyber infiltration of US federal agencies and corporations, examining cybersecurity failures, potential risks, and necessary actions moving forward.
Emergency Planning and Preparing for Wildfire Evacuations
Learn essential strategies for wildfire preparedness, including emergency planning and evacuation procedures. Gain valuable insights to protect your community before disaster strikes.

Integrating Mobile Devices into Penetration Testing Programs
Explore techniques for assessing mobile device security risks in enterprise environments, including phishing, undermining controls, and using compromised devices as pivot points.
Attack Tree Vignettes for Containers as a Service Applications - Risk-Centric Threat Modeling
Explore attack tree vignettes and risk-centric threat models for Containers as a Service applications, focusing on security challenges in cloud adoption and containerization.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Practical Tips for Running a Successful Bug Bounty Program
Practical tips for running a successful bug bounty program, including scope definition, communication strategies, and vulnerability rating. Insights from experienced professionals on managing crowdsourced security testing effectively.
Practical Threat Modeling with Microsoft's Threat Modeling Tool 2016
Learn practical threat modeling using Microsoft's Threat Modeling Tool 2016. Explore data flow-based techniques, risk assessment, and countermeasures for effective application security.
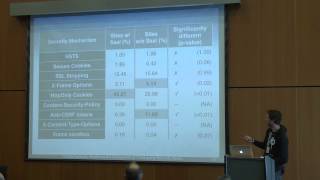
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
11,000 Voices - Experts Shed Light on 4-Year Open Source and AppSec Survey
Experts discuss findings from a 4-year study on open source security practices, revealing surprising trends in policy enforcement, vulnerability tracking, and organizational preparedness for security threats like Heartbleed.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.