Everything You Always Wanted to Know About Fingerprinting Browser Extensions
Explore browser extension fingerprinting techniques, their implications for user privacy, and current browser defenses. Learn about DOM modifications, stylesheet hijacking, and web-accessible resources.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
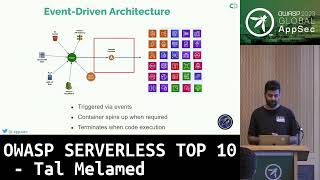
OWASP Serverless Top 10 - Understanding Security Risks in Serverless Applications
Explore the top 10 security risks in serverless architectures, understanding vulnerabilities and best practices for securing cloud-native applications.
Automated Security Testing With OWASP Nettacker
Learn automated security testing techniques using OWASP Nettacker, a powerful open-source tool for vulnerability assessment and information gathering in web applications and networks.
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
Reducing Software Vulnerability at a Global Scale
Explore strategies for reducing software vulnerabilities on a global scale, leveraging collective efforts of millions to enhance cybersecurity and protect digital ecosystems.
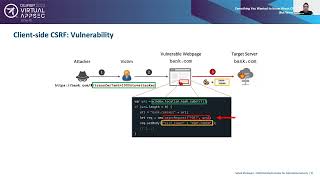
Everything You Wanted to Know About Client-Side CSRF But Were Afraid to Ask
Explore client-side CSRF vulnerabilities, detection challenges, and advanced analysis techniques using hybrid property graphs for improved web application security.
Preventing Subdomain Takeover with OWASP Domain Protect
Learn to prevent subdomain takeovers using OWASP Domain Protect. Enhance your application security knowledge with practical strategies and tools.
OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
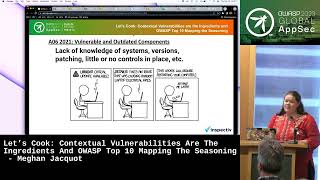
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
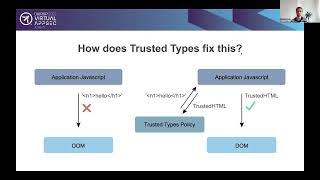
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.