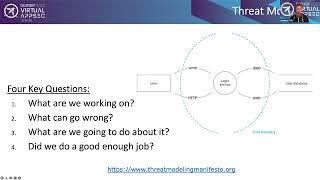
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
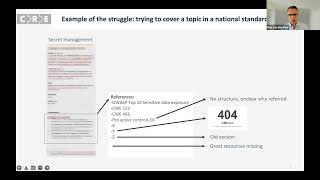
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
OWASP Web Honeypot Project
Explore web application security through honeypot technology. Learn deployment strategies, data analysis, and threat intelligence gathering to enhance your cybersecurity defenses.
Security Begins with Secure Development Environments
Explore supply chain security threats in development environments, focusing on vulnerabilities in Visual Studio Code extensions and their potential for remote code execution.
Common Application Security Mistakes Enabling Automated Attacks
Explore common security flaws enabling automated attacks on applications, including retail fraud and account takeovers. Learn from real-world examples and discover effective prevention strategies.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
Scaling AppSec through Education
Strategies for scaling application security through developer education, addressing the imbalance between security teams and developers and emphasizing code review for early bug detection.
AppSec Champions Programs - Best Practices and Survey Results
Explore AppSec champions programs: research findings, best practices, and strategies for influencing developers to write secure code. Learn to implement and improve these programs in your organization.
Five Philosophies for Building Better Application Logs
Discover five philosophies for creating application logs that enhance breach readiness and forensic capabilities, empowering developers to build more secure and analyzable systems.
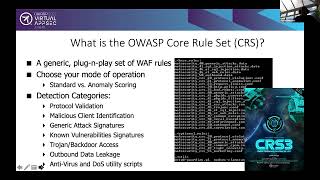
Big Data Intelligence - Harnessing Petabytes of WAF Statistics for Web Protection
Explore big data analysis of web application security trends, focusing on WAF statistics, attack patterns, and OWASP ModSecurity Core Rule Set accuracy. Learn to navigate and improve cloud-based web protection.
Top Ten Proactive Controls for Secure Software Development
Explore essential software security controls for developers, covering authentication, access control, validation, and more. Learn proactive strategies to build robust, secure applications.
2013 AppSec Guide and CISO Survey - Making OWASP Visible to CISOs
Insights from OWASP's 2013 AppSec Guide and CISO Survey, focusing on application security governance, risk management, and investment strategies for Chief Information Security Officers.
Introduction to Emerging JSON-Based ID and Security Protocols
Explore emerging JSON-based identity and security protocols with Brian Campbell, focusing on JOSE and its applications in modern authentication and authorization systems.
Telecom User Group and Cloud Native Network Functions Testbed - Introduction and Deep Dive
Explore the evolution of telecom network functions to cloud-native, discussing challenges, architecture, and performance testing in Kubernetes environments.
The Next Generation of Cybersecurity Threats
Explore emerging cybersecurity threats with NSA Director Rob Joyce, covering VPN vulnerabilities, nation-state actors, ransomware, and quantum-resistant encryption in this insightful discussion.
Fast Follower Strategy and Preserving America's Technological Edge
Explore strategies for maintaining America's technological edge, focusing on innovation, cybersecurity, and competition with China in this insightful panel discussion with industry experts.
User Groups: The Gateway to Apache
Discover strategies to leverage user groups for promoting open source ecosystems, engaging communities, and fostering active participation in software development.
Diversity for Those Playing Life on Easy
Explore diversity challenges in open source communities, learn from personal experiences, and gain actionable insights to foster inclusivity and build stronger collaborative environments.
Agreeing to Disagree - Philanthropy and the Marketplace of Ideas
Explore the role of philanthropy in shaping public discourse and policy debates, examining criticisms and arguments for diverse viewpoints in a democratic society.