Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
OWASP CycloneDX - Software Bill of Materials Standard
Explore OWASP CycloneDX, a lightweight software bill of materials (SBOM) standard, with experts Steve Springett and Patrick Dwyer. Learn about its features, applications, and importance in modern software development.
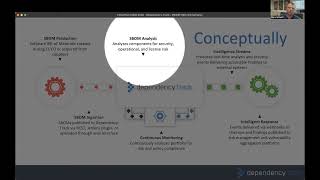
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
Stop the Looters: Method to Detect Digital Skimming Attacks
Discover a method to detect and prevent digital skimming attacks on websites, protecting sensitive customer data from theft by malicious actors like Magecart.
OWASP Top 10 Privacy Risks 2021 - Understanding and Mitigating Web Application Privacy Threats
Explore OWASP's updated Top 10 Privacy Risks for web applications, covering vulnerabilities, consent issues, and data quality. Learn countermeasures to build a more private digital future.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
Secure Messengers and Man in the Contacts Attack
Explore the Man in the Contacts attack, its implementation in a mobile game, and its potential for spear phishing in secure messaging apps. Learn about vulnerabilities and possible mitigations.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
Passive Fingerprinting of HTTP/2 Clients
Explore HTTP/2 protocol nuances for passive client fingerprinting. Learn about implementation differences, potential use cases, and security implications in this comprehensive overview.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Secure Coding Lessons for Mobile Apps - Insights from the Trenches
Explore common mobile app coding pitfalls, their real-world impacts, and learn effective strategies to enhance security. Includes demonstrations of attacker techniques and protective code samples.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
Pwning WhatsApp - The Dark Side of Web-based Messaging Apps
Explore vulnerabilities in web-based messaging apps, focusing on WhatsApp. Learn about potential security risks and exploitation techniques in popular communication platforms.
Privacy Threat Modeling - Analysis of Cloud Services Against Privacy Regulations
Learn to analyze cloud services for privacy threats and regulatory compliance using threat modeling techniques, enhancing your ability to protect sensitive data.
Impact of Diversity on Software and Security Teams
Explore the impact of diversity on software and security teams, examining its influence on team dynamics, problem-solving, and overall effectiveness in the tech industry.
Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.