Error Handling and Security Management in AI Powered Apps - Web Development With AI Episode 7
Learn to handle errors and manage security in AI-powered web apps. Covers bug fixing, input validation, protection against bad actors, and AI-specific attack prevention.
The Evolving Community of Application Security
Explore the evolution of Application Security, its growing importance, and the role of the community in addressing future security challenges at scale.
Webhooks Hookups - Abusing API Developers
Explore the security risks of Webhooks in API development, including potential vulnerabilities, real-world examples, and preventive measures. Learn about a new toolkit for auditing Webhook exposure.
Rhyming with Hacks - The Ballad of Supply Chain Attacks
Explore supply chain attacks, their anatomy, and prevention strategies. Learn about real-life examples, existing solutions, and a new DOM monitoring approach with live demonstration.
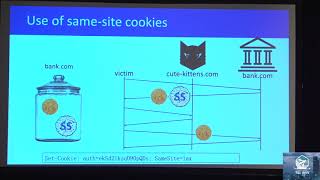
Bypassing Browser Policies and Privacy Extensions for Cookies
Explore bypasses to browser policies and extensions for cookie security. Learn about an automated framework for evaluating countermeasures against cross-site attacks and third-party tracking.
Automated Cyber Security Platform at Scale
Explore the vision and demo of an open-source Automated Security Platform, addressing sophisticated threats through security orchestration and automation to overcome data and process overload.
Software Bill of Materials (S-BoM) - Reducing Risk in Third-Party Components
Explore best practices for managing third-party component risks using software bill-of-materials (S-BoM). Learn to create S-BoMs, identify vulnerabilities, and automate security responses in polyglot environments.
An Attacker's View of Serverless and GraphQL Apps
Explore attack vectors and security vulnerabilities in serverless and GraphQL applications from a red-team perspective. Learn practical exploitation techniques and defense strategies for modern distributed systems.
Adding Privacy to Threat Modeling - Game On!
Explore how LogMeIn extended the Elevation of Privilege card game to incorporate privacy considerations, bridging knowledge gaps between development, security, and compliance teams through gamification.
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
AppSec is Dead - Long Live DevSecOps
Explore the shift from AppSec to DevSecOps, focusing on creating secure code, working smarter, and implementing key pillars for effective security integration in software development.
OWASP Distinguished Lifetime Member Award - Jeff Williams' Contributions
Explore Jeff Williams' contributions to OWASP, including foundational projects, non-profit creation, and innovative security concepts, in this insightful 20th anniversary recognition.
What's The Future - Automation, Jobs, and the Human-Centered Economy
Explore the impact of automation on jobs and the economy, discussing strategies to leverage technology for growth and create a human-centered future.
OWASP NL Chapter Meeting - SKF News
Learn about the latest developments in OWASP's Security Knowledge Framework (SKF) from experts Riccardo and Glenn ten Cate, enhancing your understanding of web application security best practices.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.

WebAuthn - Balancing Strong Authentication, Privacy, and Convenience
Explore the balance between robust authentication, user privacy, and ease of use in WebAuthn implementation for enhanced online security.
Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
SBOM SmackDown - Conquering Software Supply Chain Risks with OWASP CycloneDX
Explore Software Bill of Materials (SBOM) and learn how OWASP CycloneDX standard enhances software supply chain transparency, enabling better risk-based decisions and compliance with government mandates.
Practical Threat Modeling for Real-World and Cloud Situations in Hybrid Work Environments
Practical guide to threat modeling for cloud and hybrid work environments, covering creation, identification, addressing, and validation of threats with real-world examples and tools.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Understanding the API Attack Vector - How Attackers Exploit Application Communications
Explore attacker techniques for targeting API-driven applications, including code manipulation, mobile vulnerabilities, and advanced attacks. Learn strategies to secure apps in cloud-native environments.