Code Deobfuscation - Intertwining Dynamic, Static and Symbolic Approaches
Explore advanced code deobfuscation techniques combining dynamic, static, and symbolic approaches to enhance software analysis and reverse engineering capabilities.
Command Injection in F5 iRules
Explore command injection vulnerabilities in F5 iRules, focusing on syntax, exploitation techniques, and security implications for BigIP F5 products used in high-performance web traffic routing.
Under the SEA - A Look at the Syrian Electronic Army's Mobile Tooling
Explore the Syrian Electronic Army's mobile surveillance tools, focusing on SilverHawk, its capabilities, and deployment methods in this cybersecurity analysis.
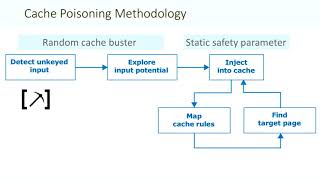
Practical Web Cache Poisoning - Redefining 'Unexploitable'
Explore web cache poisoning techniques to compromise websites by exploiting caches and content delivery networks, turning them into exploit delivery systems targeting unsuspecting visitors.
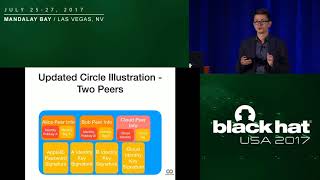
Intercepting iCloud Keychain
Discover critical cryptographic flaws in iCloud Keychain's end-to-end encryption, potentially allowing attackers to access plaintext secrets through man-in-the-middle attacks on iCloud communications.
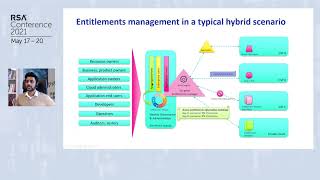
Managing Access Entitlements and Their Lifecycle in a Multi-Cloud Environment
Explore strategies for managing access entitlements across multi-cloud environments, addressing security risks and improving governance practices for effective IAM controls.
Building Secure and Reliable Systems at Scale
Learn Google's best practices for building secure, reliable systems at scale through automated security, containment, and multi-party techniques that foster a culture of review and resilience.
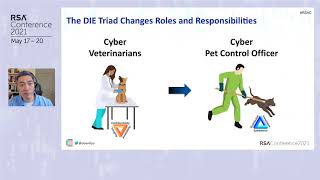
Death to CIA! Long Live DIE! - How the DIE Triad Helps Us Achieve Resiliency
Explore the DIE Triad (Distributed, Immutable, Ephemeral) as an alternative to CIA, reducing security burden and enabling true resiliency. Learn to apply DIE principles for tackling security, resiliency, and privacy challenges.
Remember When We Used to Call It "Information Security"? Let's Go Back to That
Experts discuss shifting focus back to information security, exploring advancements in identity management and encryption to better protect data in an interconnected world.
Confidential Computing in Cloud and Edge
Explore Confidential Computing in cloud and edge environments, focusing on Trusted Execution Environments, data protection, and scalable implementation solutions for enhanced security.

Post-Exploitation of Cloud Service Providers
Explore AWS post-exploitation techniques, including cloud-wide credential theft and backdooring compromised accounts, to enhance penetration testing skills for cloud environments.
Cloud Threat Modeling - From Architecture Design to Application Development
Learn cloud threat modeling techniques to identify and mitigate security risks in architecture design and application development, focusing on determining attack surfaces and eliminating common flaws.
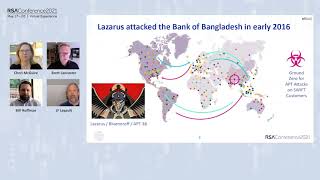
Reducing Payment Fraud with SWIFT Customer Security Controls Framework
Explore SWIFT's Customer Security Program: its impact on reducing payment fraud, enhancing cyber hygiene, and evolving to meet future challenges in the global financial ecosystem.
The Crash Course - A Non-Programmer's Guide to Fuzzing
Hands-on workshop for non-programmers to learn fuzzing techniques. Covers environment setup, tools like AFL and Honggfuzz, instrumentation, input selection, and crash analysis. Suitable for beginners to intermediate level.
Migrate Securely from On Prem to Azure Cloud
Learn strategies for secure migration from on-premise to Azure Cloud, focusing on real-time scenarios, architecture design considerations, and Azure services for seamless transition while addressing security challenges.
From Reactive to Proactive - Operationalizing Your Threat Intel
Cybersecurity experts discuss operationalizing threat intelligence, moving from reactive to proactive approaches, and addressing challenges in cloud adoption and workforce training for enhanced security.
Security Research and Disclosure - The Unauthorized Biography
Explore the evolution of security research and disclosure, from historical "unbreakable locks" to modern challenges in IoT, blockchain, and AI, with insights on ethical hacking and vulnerability reporting.
Enterprise Security Architecture - Is It Time for a Booster Shot?
Explore evolving enterprise security architecture beyond traditional layered defense, addressing modern challenges like advanced hacking, cloud adoption, and remote work to enhance organizational cybersecurity.
Extract Data from Damaged Android Mobile Device - Version 7.X.X
Comprehensive workshop on extracting data from damaged Android devices, covering soldering, retrieval of device information, and extraction of various data types for forensic analysis.
Exploiting Android Messengers with WebRTC
Explore WebRTC vulnerabilities in Android messaging apps, their exploitation, and mitigation strategies. Learn about security research techniques and mobile application security.
The Great Sandbox Escape
Explore novel ransomware techniques, including virtual machine deployment for attacks. Learn about attacker strategies, detection methods, and cybersecurity insights from a malware specialist.