Effective Vulnerability Discovery with Machine Learning
Explore machine learning techniques for effective vulnerability discovery in software dependencies, enhancing security analysis beyond traditional methods.
Securing the Next Version of HTTP - How QUIC and HTTP-3 Compare to HTTP-2
Explore QUIC and HTTP/3 protocols, their security features, and improvements over HTTP/2. Learn about encryption, handshakes, and performance enhancements in next-gen web communication.
Hey Google, Activate Spyware! - When Google Assistant Uses a Vulnerability as a Feature
Explore Android vulnerabilities allowing unauthorized camera control, revealing security flaws in Google Assistant and discussing implications for user privacy and smartphone security.
Complexity Killed Security
Explore how increasing hardware complexity impacts software security, challenges in documentation access, and potential solutions for modern cybersecurity threats.
Lateral Movement and Privilege Escalation in GCP - Compromise Organizations without Dropping an Implant
Explore techniques for identity compromise, privilege escalation, and lateral movement in Google Cloud. Learn about GCP's unique security model and default permissions, with demonstrations and tool releases.
Stealthily Access Your Android Phones - Bypass the Bluetooth Authentication
Explore Android Bluetooth vulnerabilities, including BlueRepli, and learn stealthy access techniques. Discover security risks in AOSP and mobile manufacturers' oversights.
Web Cache Entanglement - Novel Pathways to Poisoning
Explore novel web cache poisoning techniques, probing cache inconsistencies to build sophisticated exploit chains. Learn to uncover vulnerabilities in caching systems across the internet.
My Cloud is APT's Cloud - Investigating and Defending Office 365
Investigate and defend Office 365 against sophisticated attacks. Learn authentication types, attack lifecycle, and effective countermeasures for cloud-based enterprise security.
A Hacker's Guide to Reducing Side-Channel Attack Surfaces Using Deep Learning
Explore deep-learning techniques to identify and reduce side-channel attack vulnerabilities, leveraging AI explainability for efficient implementation assessment and improved security.
TiYunZong Exploit Chain to Remotely Root Modern Android Devices - Pwn Android Phones from 2015-2020
Comprehensive exploit chain analysis for remotely rooting modern Android devices, focusing on Pixel phones. Explores attack surfaces, introduces new vulnerabilities, and demonstrates practical exploitation techniques.
Attacking iPhone XS Max
Explore iPhone XS Max vulnerabilities, including PAC implementation, XNU bug exploitation, and kernel read/write access. Learn about Unix Domain Socket, race conditions, and unprotected control flow transfer points.
API-Induced SSRF - How Apple Pay Scattered Vulnerabilities Across the Web
Explore API security vulnerabilities, focusing on Apple Pay's impact, with live demos and actionable strategies for improving defensive programming practices.
The Enemy Within - Modern Supply Chain Attacks
Practical guidance on defending against and responding to supply chain attacks, covering prevention strategies, risk assessment, and best practices for both SecOps and App Development professionals.
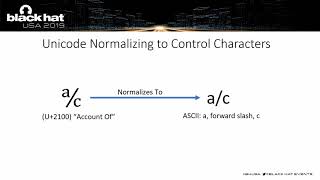
HostSplit - Exploitable Antipatterns in Unicode Normalization
Explore new exploit techniques using Unicode normalization to bypass URL security filters and enable domain impersonation, with focus on software-fooling attacks beyond visual spoofing.
Preventing Authentication Bypass - A Tale of Two Researchers
Explore techniques for identifying authentication bypass vulnerabilities, learn effective researcher-company partnerships, and discover secure coding practices to prevent similar flaws in web applications.
Unveiling the Underground World of Anti-Cheats
Explore anti-cheat techniques in gaming, from market analysis to advanced methods like memory manipulation, with insights on implementation and real-world examples.
Behind the Scenes of iOS and Mac Security
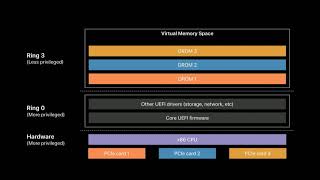
Explore iOS and macOS security features, including Find My, Gatekeeper, and kernel integrity protection. Learn about Apple's innovative approaches to user privacy and device security.
Transparency in the Software Supply Chain - Making SBOM a Reality
Explore the concept of Software Bill of Materials (SBOM) and its potential to enhance transparency in the software supply chain, discussing benefits, challenges, and implementation strategies.
HTTP Desync Attacks - Smashing into the Cell Next Door
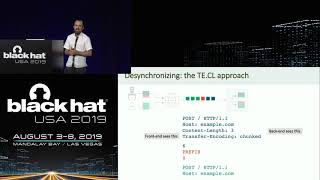
Explore techniques for HTTP request splicing, enabling remote attackers to manipulate web infrastructure, exploit visitors, and breach system isolation. Learn detection, case studies, and mitigation strategies.
DIFUZE - Android Kernel Driver Fuzzing
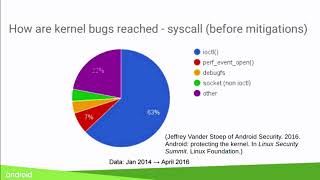
Explore Android kernel driver fuzzing with DIFUZE, a tool for identifying vulnerabilities in third-party driver code. Learn techniques to improve Android security infrastructure and discover potential weaknesses.
Talking Behind Your Back - Attacks and Countermeasures of Ultrasonic Cross-Device Tracking
Explore ultrasonic cross-device tracking: its marketing potential, privacy implications, and vulnerabilities. Learn about attacks, countermeasures, and the future of this emerging technology.