Alexa, Hack My Serverless Please
Explore serverless security risks, focusing on event injection attacks across various platforms. Learn to identify and mitigate vulnerabilities in cloud-based applications.
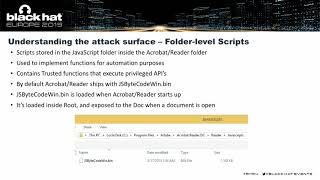
Tackling Privilege Escalation with Offense and Defense
Explore privilege escalation in JavaScript engines, focusing on offensive techniques and defensive strategies. Learn about vulnerabilities, attack surfaces, and security model improvements.
What the Fuzz
Explore cutting-edge fuzzing technologies, their potential, and future developments through demos, CVEs, and research insights from experts in the field.
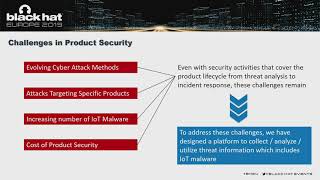
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.
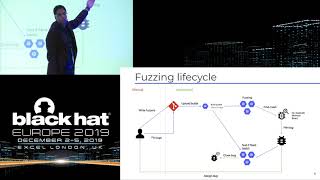
ClusterFuzz - Fuzzing at Google Scale
Explore Google's massive fuzzing infrastructure, ClusterFuzz, and learn how it finds thousands of security vulnerabilities across Google products and open-source projects.

Reverse Engineering and Exploiting Builds in the Cloud
Explore security vulnerabilities in cloud-based CI/CD and container build environments. Learn about potential attack scenarios, remediation strategies, and best practices for securing the software supply chain.
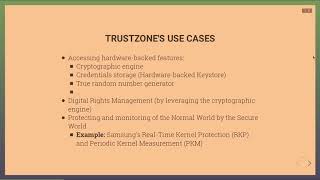
Breaking Samsung's ARM TrustZone
Explore Samsung's TrustZone vulnerabilities and learn techniques to exploit trusted components, execute high-privilege code, and bypass security measures in ARM-based systems.
The Metaverse of Vulnerability
Explore the cybersecurity challenges and vulnerabilities in the metaverse, from technical issues to operational risks, and learn proactive strategies to address these concerns.
The State of State Machines
Explore mobile security threats, the evolving landscape, and Zero Trust principles in this insightful discussion on protecting mobile devices and data.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.
Mac-A-Mal - An Automated Platform for Mac Malware Hunting
Automated platform for macOS malware analysis, featuring kernel-level behavioral monitoring and extending Cuckoo sandbox capabilities. Supports various sample types and detects evasion techniques.
Static Detection and Automatic Exploitation of Intent Message Vulnerabilities in Android
Explore Android app vulnerabilities, static analysis techniques, and automated exploitation methods for intent message flaws. Learn to identify and mitigate security risks in mobile app development.
Fingerprinting Web Application Platforms by Variations in PNG Implementations
Explore PNG implementation variations across web platforms for enhanced fingerprinting techniques in security audits, overcoming traditional methods and identifying platforms even with anti-fingerprinting measures.

IoT Malware - Comprehensive Survey, Analysis Framework and Case Studies
Comprehensive exploration of IoT malware, covering its evolution, analysis frameworks, and real-world case studies. Insights into vulnerabilities, detection methods, and future challenges in securing connected devices.
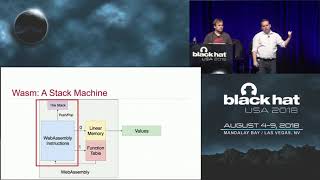
WebAssembly - A New World of Native Exploits on the Browser
Explore WebAssembly's security risks, low-level semantics, and potential vulnerabilities in browser-based applications. Learn about linear memory, function tables, and mitigation strategies.
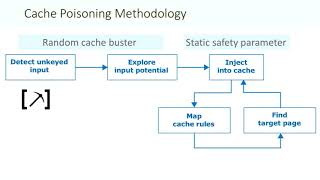
Practical Web Cache Poisoning - Redefining 'Unexploitable'
Explore web cache poisoning techniques to compromise websites by exploiting caches and content delivery networks, turning them into exploit delivery systems targeting unsuspecting visitors.
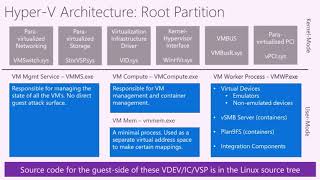
A Dive into Hyper-V Architecture and Vulnerabilities
Explore Hyper-V architecture, vulnerabilities, and security implications in virtualization technology. Gain insights into guest-to-host exploits and platform security challenges.
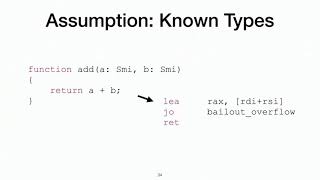
Attacking Client-Side JIT Compilers
Explore JIT compiler security in JavaScript engines, focusing on challenges, solutions, and potential vulnerabilities. Learn about optimization techniques and their impact on browser exploitation.
A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages
Explore a new SSRF exploit technique targeting URL parsers in popular programming languages. Learn about protocol smuggling, fuzzing tools, and discover vulnerabilities in widely-used libraries.
Inside Android's SafetyNet Attestation
Explore Android's SafetyNet Attestation, its role in ecosystem security, and potential vulnerabilities. Learn about attack patterns, device integrity detection, and implementation challenges.
CALDERA - Automating Adversary Emulation
Automate adversary emulation for network security using CALDERA. Replicate realistic post-compromise techniques, leveraging benign system functionality to enhance defensive strategies.