Data & Software Sharing Guidance for Early Career Researchers - AGU Journal Requirements
Learn best practices for citing and sharing research data and software, focusing on AGU journal requirements and tools that simplify the process for early career researchers.
Managing the Reactive World with RxJava - Jake Wharton
Explore asynchronous programming with RxJava: model reactive sources, handle data streams, and learn about Java 9's Flow API for building robust, responsive applications.
What's New in Grails 2.0
Explore Grails 2.0's new features: agent-based reloading, unit testing mixins, advanced GORM queries, and more. Ideal for both new users and experienced Grails 1.x developers seeking to upgrade.
Tired of Playing Exploit Kit Whack-A-Mole? Let's Automate
Explore automated detection of Exploit Kits using headless browsers, JavaScript, and DOM inspectors for efficient web crawling and analysis of malware delivery techniques.
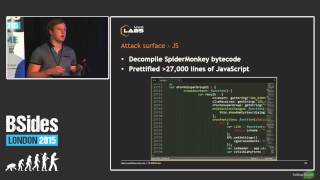
Why Bother Assessing Popular Software
Explore assessing popular software like Adobe Reader, discussing fuzzing, sandboxes, and JavaScript APIs. Learn approaches for complex targets and making a security impact.
Penetration Testing Must Die
Explore the limitations and challenges of penetration testing in cybersecurity, discussing its effectiveness, terminology issues, and potential alternatives for improving security assessments.
Cloud Computing
Explore cloud computing risks, certifications, and security considerations with insights on virtualization and the Cloud Security Alliance.
Practical Crypto Attacks Against Web Applications
Explore practical crypto attacks on web apps, covering ECB and CBC modes, block swapping, padding oracles, and signed cookies. Gain insights into vulnerabilities and defense strategies.
RATs and IOCs - The Easy Way
Explore techniques for extracting and analyzing Remote Access Trojan (RAT) configurations, focusing on static analysis methods and utilizing the extracted data for threat intelligence and defense.
How We Hacked Your Billion Dollar Company For Forty-Two Bucks
Discover how a small investment can expose major vulnerabilities in billion-dollar companies. Learn about red teaming, user enumeration, and password spraying techniques used by ethical hackers.
Securing Cloud Delivery Pipelines - Findings From A Blue-Red Team Security Simulation
Explore findings from a blue/red team security simulation focused on securing cloud delivery pipelines, with insights on tooling, advanced attackers, and best practices.
The Little Phone That Could Ch-ch-chroot
Explore cost-effective Red Team tactics using a covert disposable phone for reconnaissance, including device rooting, functionality, and anti-forensics techniques.
Assessing the Embedded Devices On Your Network
Explore embedded device security challenges, threat modeling, and assessment techniques through a VoIP phone case study. Learn hardware tricks, debugging methods, and potential mitigations for vulnerabilities.
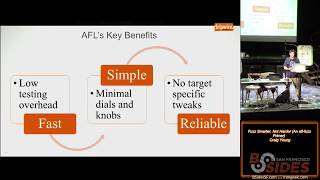
Fuzz Smarter, Not Harder - An AFL-Fuzz Primer
Comprehensive guide to efficient fuzzing using afl-fuzz, covering instrumentation techniques, optimization strategies, and crash analysis for effective bug hunting and software security testing.
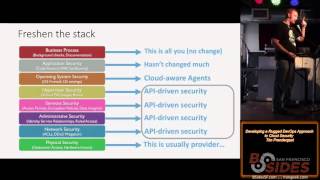
Developing a Rugged DevOps Approach to Cloud Security
Strategies for integrating continuous security into DevOps processes, emphasizing automation, monitoring, and agile security practices for cloud environments.
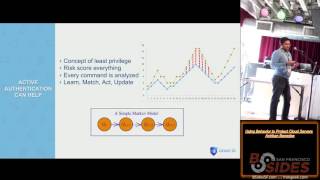
Using Behavior to Protect Cloud Servers
Explore behavior-based analytics for cloud server security, focusing on dynamic privilege management to identify and prevent insider threats and privilege escalation attacks in real-time.
Secure by Design - Usable Security Tooling
Explore strategies for creating effective security products by prioritizing usability, leading to better and more secure experiences for users.
Owning the Smart Home with Logitech Harmony Hub
Explore reverse engineering of Logitech's Harmony smart home hub, uncovering vulnerabilities and discussing their implications for device security and potential exploitation.
Fighting Email Phishing with a Custom Cloud IDS
Learn to build a custom cloud-based email IDS to combat phishing, enhancing security while improving operational efficiency. Explore real-time threat adaptation and AWS implementation.
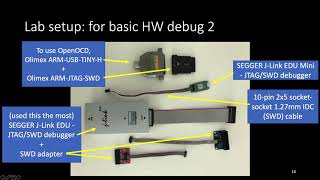
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
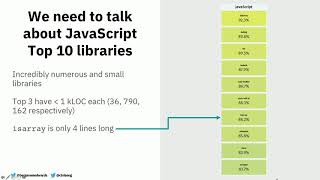
The Devils in the Dependency - Data Driven Software Composition Analysis
Análisis de datos sobre el uso de bibliotecas de código abierto en aplicaciones, examinando vulnerabilidades, dependencias y patrones de actualización para mejorar la seguridad del software.