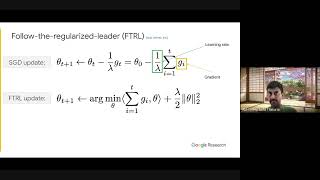
Federated Learning with Formal User-Level Differential Privacy Guarantees
Explore federated learning with user-level differential privacy guarantees. Discover scalable algorithms for industrial workloads in data privacy and machine learning.
Privacy-Preserving Machine Learning with Fully Homomorphic Encryption
Explore Fully Homomorphic Encryption for privacy-preserving machine learning, enabling zero-trust interactions and secure model deployment on untrusted servers.
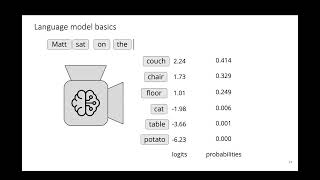
Publicly Detectable Watermarking for Language Models - PPML 2024 Invited Talk
Explore cutting-edge research on publicly detectable watermarking for language models in this invited talk by Sanjam Garg at PPML 2024, addressing privacy concerns in machine learning.
Practical Cryptographic Solutions for Secure Inference and Private Benchmarking
Explore practical cryptographic solutions for secure inference and private benchmarking in machine learning, presented by Nishanth Chandran at PPML 2024.
Samplable Anonymous Aggregation for Private Federated Data Analysis
Kunal Talwar explores samplable anonymous aggregation for private federated data analysis, discussing innovative approaches to privacy-preserving machine learning in distributed settings.

Federated User Representation Learning: Privacy-Preserving Personalization in Distributed Systems
Explore federated user representation learning for privacy-preserving collaborative personalization in machine learning, improving model quality while maintaining user privacy.
OblivGNN: Oblivious Inference on Transductive and Inductive Graph Neural Networks
Discover a privacy-preserving solution for secure GNN inference in cloud services, enabling protected analysis of sensitive graph data while maintaining model confidentiality and efficiency.
Scalable Multi-Party Computation Protocols for Machine Learning in the Honest-Majority Setting
Discover groundbreaking advances in privacy-preserving machine learning through scalable multi-party computation protocols, featuring efficient methods for secure operations and unprecedented performance with up to 63 parties.
MD-ML: Super Fast Privacy-Preserving Machine Learning for Malicious Security with Dishonest Majority
Explore groundbreaking advances in privacy-preserving machine learning with MD-ML framework, offering enhanced security and efficiency for multi-party computation in neural network inference and training.
Differentially Private Diffusion Probabilistic Models for Image Synthesis
Explore how dp-promise leverages diffusion model noise to achieve differential privacy in image synthesis while maintaining high image quality and protecting sensitive training data.