World-leaders in Cryptography - Yuriy Polyakov
Explore lattice-based cryptography, homomorphic encryption, and privacy-preserving machine learning with Duality Technologies' VP of Cryptography, Yuriy Polyakov.
Differentially Private Synthetic Data for Private LLM Training
Explore cutting-edge techniques for generating private synthetic data in LLM training, focusing on differential privacy methods and their practical applications in AI development.
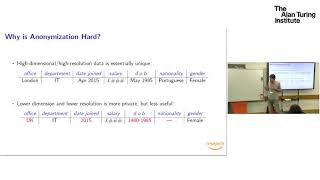
A Short Tutorial on Differential Privacy
Explore differential privacy fundamentals, applications in machine learning, and key definitions. Learn about privacy-preserving computations and various mechanisms for protecting sensitive data.
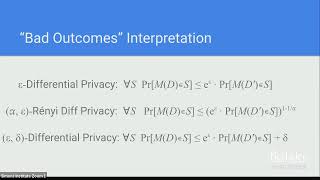
Differential Privacy & Variants
Explore differential privacy and its variants, focusing on information-theoretic methods for enhancing trustworthiness in machine learning algorithms and applications.
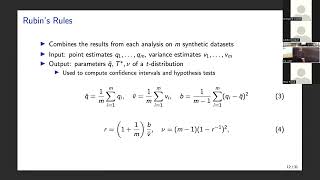
Noise-Aware Statistical Inference with Differentially Private Synthetic Data
Explore noise-aware statistical inference techniques for differentially private synthetic data, combining multiple imputation and Bayesian modeling to produce accurate uncertainty estimates for population-level quantities.
Deep Learning with Differential Privacy
Explore deep learning techniques for privacy-preserving machine learning, focusing on neural networks and differential privacy in crowdsourced, sensitive datasets.
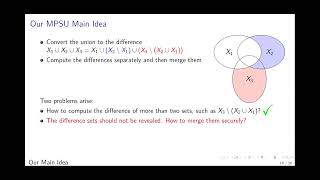
MPC for Specific Functionalities - AC 2023 Session
Explore advanced techniques in Multi-Party Computation (MPC) for specialized applications, focusing on cutting-edge research and practical implementations in cryptography.
Federated and Collaborative Learning - Session 2
Explore cutting-edge research in federated learning, collaborative AI, and privacy-preserving data analysis with expert talks on fast mean estimation and stable covariance techniques.
ABY3 - A Mixed Protocol Framework for Machine Learning
Explore privacy-preserving machine learning with ABY3, a framework addressing data collection concerns through encrypted computations and secure multi-party protocols.
CryptGPU: Fast Privacy-Preserving Machine Learning on the GPU
Explore GPU-accelerated privacy-preserving machine learning techniques for enhanced performance and scalability in image classification and private training.
SecureML - A System for Scalable Privacy-Preserving Machine Learning
Explores scalable privacy-preserving machine learning techniques for linear regression, logistic regression, and neural networks using secure two-party computation, with efficient protocols and MPC-friendly alternatives to nonlinear functions.
Privacy-Preserving Algorithms for Decentralised Collaborative Learning - Dr Aurélien Bellet
Explore privacy-preserving algorithms for decentralized collaborative learning, focusing on large-scale machine learning, distributed methods, and privacy protection in connected device data analysis.
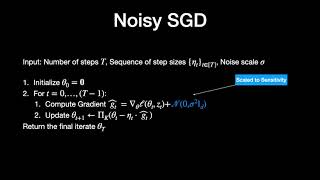
Private Stochastic Convex Optimization: Optimal Rates in Linear Time
Explore optimal rates and linear time solutions for private stochastic convex optimization, focusing on empirical risk minimization and privacy amplification techniques.
Federated Machine Learning with Kubernetes
Explore federated machine learning implementation on Kubernetes, enhancing data privacy and collaboration across distributed datasets without centralized storage.
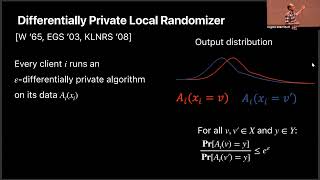
Low-Communication Algorithms for Private Federated Data Analysis - Invited Talk
Low-communication algorithms for private federated data analysis, offering optimal accuracy guarantees while preserving privacy in distributed settings.
Decentralized Data Science Made Easy
Explore decentralized data science techniques and applications in this comprehensive talk, focusing on simplifying complex concepts for practical implementation.
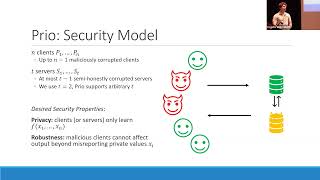
Privacy Preserving Aggregate Statistics via Boolean Shares - Part 3
Privacy-preserving aggregate statistics using Boolean shares, enhancing the Prio system for improved data collection and analysis while maintaining user privacy.
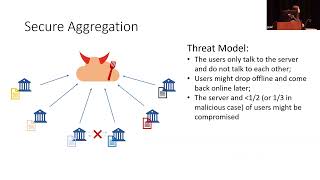
MicroFedML: Privacy Preserving Federated Learning for Small Weights
Privacy-preserving federated learning techniques for small weights, focusing on MicroFedML. Explores innovative approaches to enhance data privacy in machine learning collaborations.
Privacy-Preserving Machine Learning Workshop 2023 - Contributed Talks Session II
Explore cutting-edge research in privacy-preserving machine learning through expert presentations at the PPML 2023 workshop, covering innovative techniques and applications in the field.
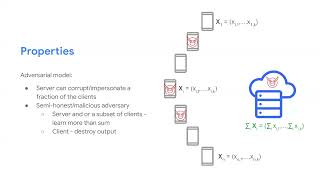
Privacy-Preserving Machine Learning - Invited and Contributed Talks
Explore privacy-preserving machine learning with expert Mariana Raykova and contributed talks from PPML 2023, covering cutting-edge research and advancements in secure AI and data protection.
Privacy-Preserving Machine Learning Workshop - Invited and Contributed Talks
Explore cutting-edge research in privacy-preserving machine learning with expert talks and contributions at PPML 2023, covering innovative techniques and advancements in the field.